-

Your PHP Installation Appears to Be Missing the MySQL Extension: What It Means and How to Fix It (2026)
TL;DRThe missing the MySQL extension message means PHP cannot find the function mysqli_connect, so WordPress stopped before it touched your database. Check the PHP version and the extension list for the account, choose one MySQL driver set, and reload. Plugins, themes and wp-config.php are not the cause.
Categories
- CMS
- Concrete5
- Drupal
- FFmpeg / Video Hosting
- Hosting Guides
- How To
- Joomla
- Security
- SEO
- Uncategorized
- Video Content
- Web Hosting News
- WooCommerce
- WordPress
Lets Connect!
-
413 Request Entity Too Large in WordPress: Find the Layer That Said No
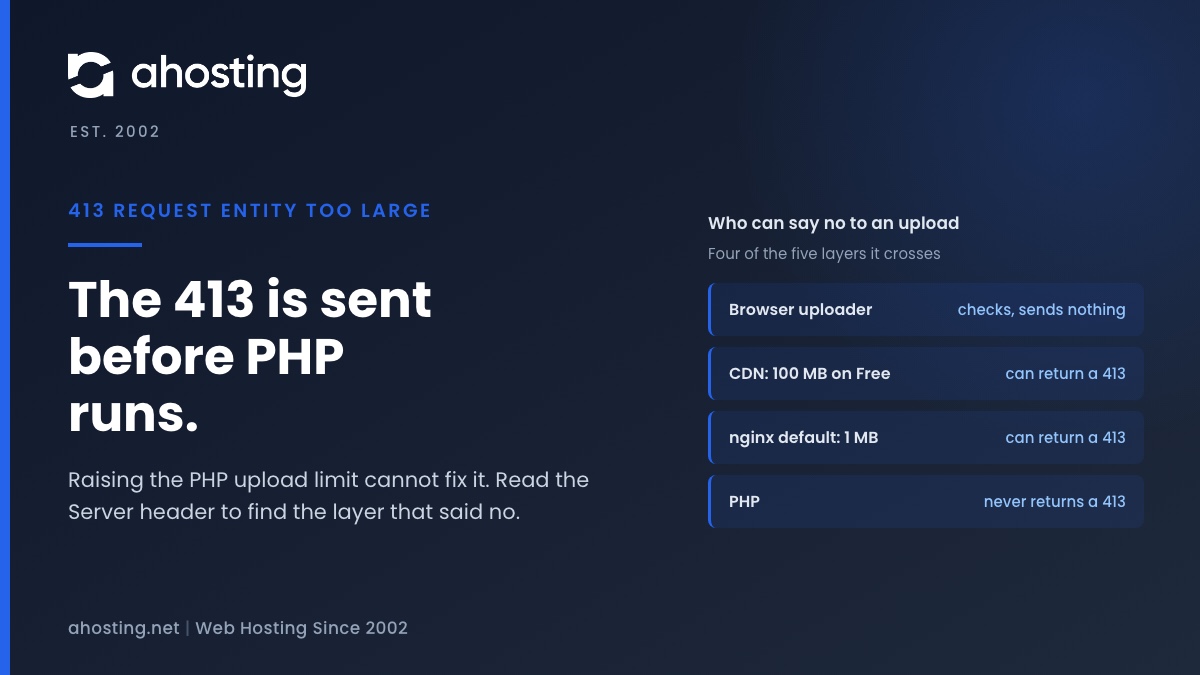
TL;DRA 413 request entity too large error means a layer in front of WordPress refused the upload before PHP saw it, so raising upload_max_filesize cannot fix it. Five layers can say no: the browser uploader, a CDN, the web server, PHP and WordPress. Read the Server header of the failed request to find the one that answered, then change the limit there. In a WordPress 7.1.3 lab, nginx rejected a 1 MB file while the Media screen promised 100 MB.
-
WordPress 7.1.3 Security Release: What Changed and How to Confirm Your Site Has It
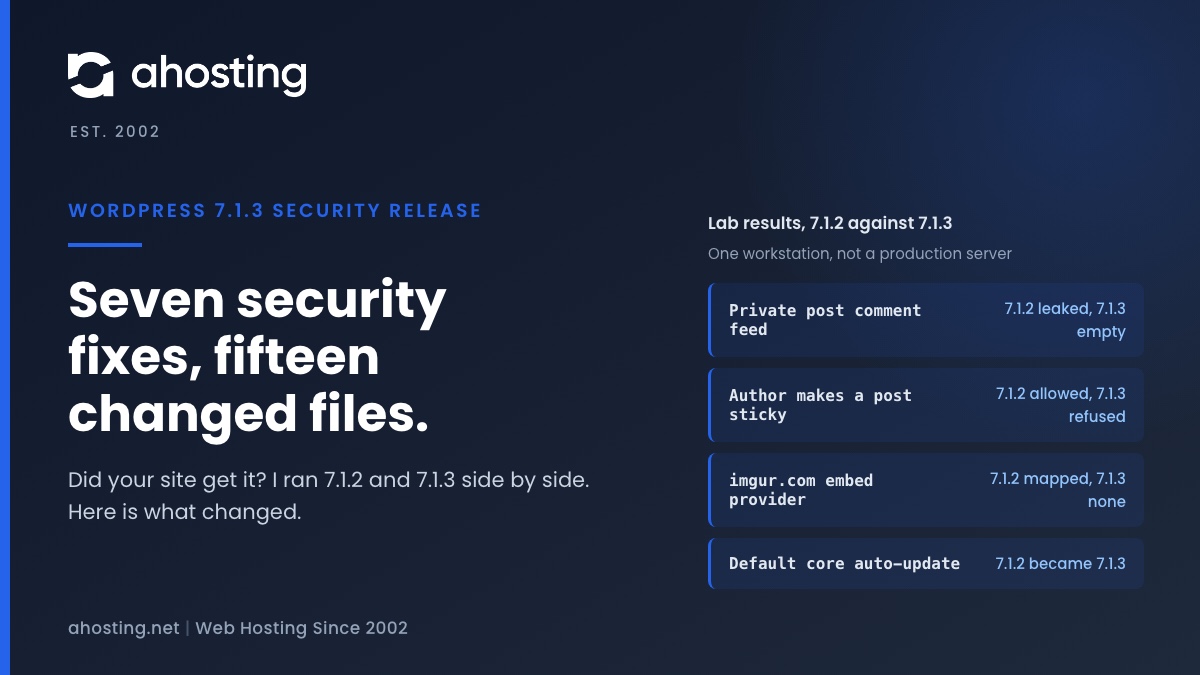
TL;DRThe WordPress 7.1.3 security release shipped on 6 October 2026 with seven security fixes and four bug fixes. Read your version under Tools, Site Health, Info, WordPress; 7.1.2 or any earlier 7.1 release needs the update. Minor releases install themselves by default, but a handful of switches stop that. In my lab, 7.1.2 handed an anonymous visitor the comments on a private post and a draft post and let an Author account make posts sticky; 7.1.3 refused both. WordPress published no CVE IDs, and none of the coverage I opened reports exploitation.
-
PHP Security Update: 8.5.12, 8.4.27, 8.3.36 and 8.2.35 for WordPress
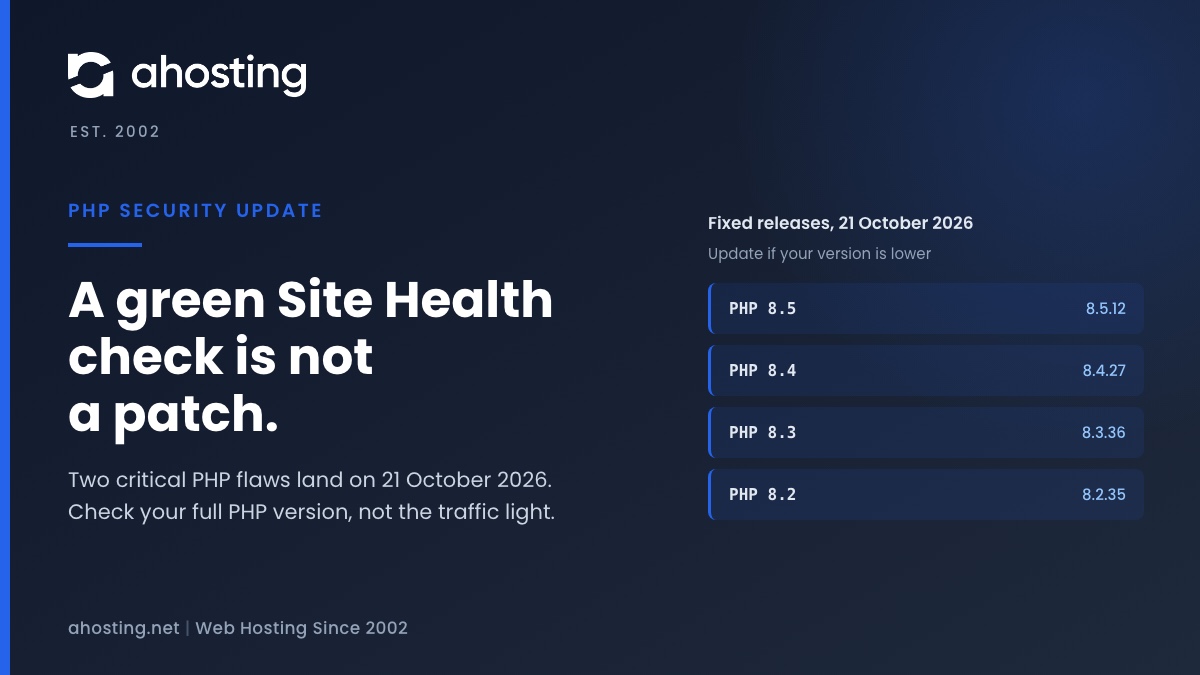
TL;DRPHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 are the php security update for two critical remote code execution flaws, released on 21 October 2026. Read your full PHP version now, and update if it is lower than the fixed release for your branch. A green WordPress Site Health check does not prove you are patched, and PHP 8.1 and older get no fix from PHP.
-
PHP Critical Security Release: What WordPress Site Owners Should Do Now
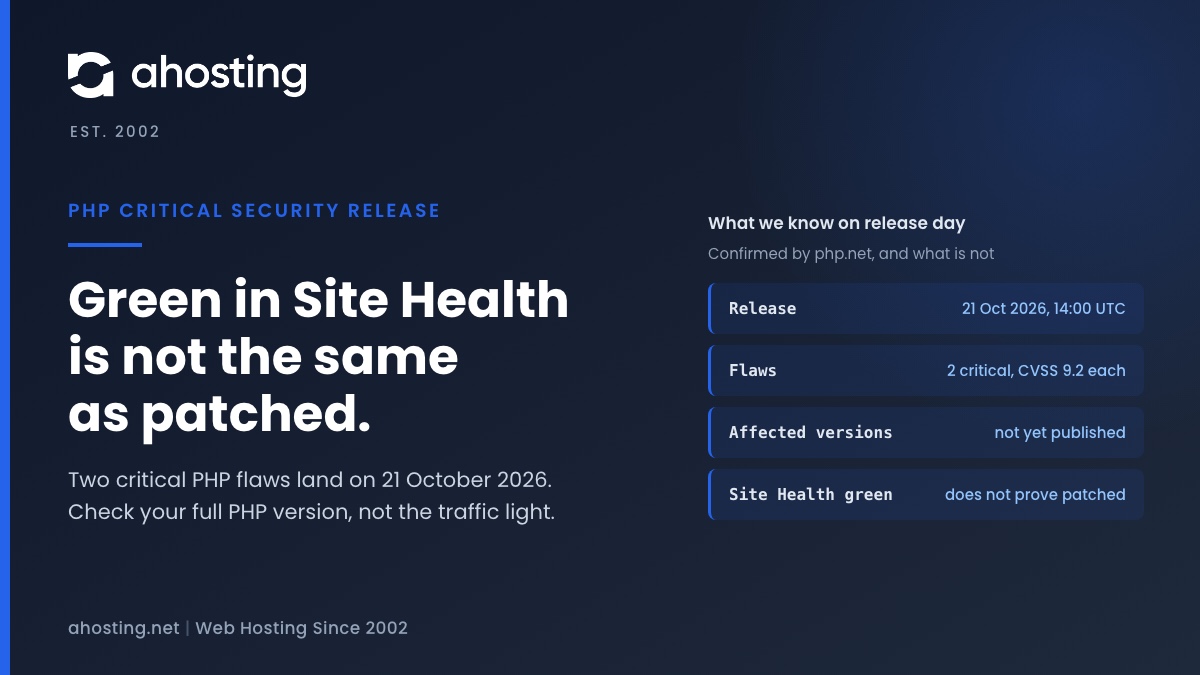
TL;DRThe PHP critical security release is due on 21 October 2026 at 14:00 UTC and fixes two flaws rated CVSS 9.2. PHP has not named the affected versions yet, so treat every WordPress site as exposed until it does. Check your full PHP version now, back up, and update as soon as the fixed version for your branch is published. A green Site Health PHP check does not prove you are patched.