Skip to content
Skip to main content
Ahosting Logo
  • Hosting
    • WordPress Hosting
      Fast, secure hosting for WordPress sites
    • Web Hosting
      Reliable, affordable hosting for sites
    • FFMpeg Hosting
      Fast hosting for FFmpeg projects
    • Reseller Hosting
      Start hosting biz with white-label plans
    • VPS Hosting
      Scalable VPS with full control & power
    • Dedicated Server
      High-power servers for max security
    • WooCommerce Hosting
      Fast hosting for WooCommerce shops
  • Domain
    • Register a Domain
      Secure your domain name in minutes
    • Domain Transfer
      Move domains to Ahosting with ease
    • Premium SSL Certificate
      Enterprise SSL to build customer trust
  • Support
    • Submit A Ticket
      Expert 24/7 help from our support team
    • Abuse Report
      Report abuse to keep network safe
    • Knowledge Base
      Quick answers via step-by-step guides
  • Company
    • Blog
      Expert articles to power your online growth
    • Compare Hosts
      Side-by-side comparison
    • Datacenter
      Secure, high tech datacenter for hosting
    • About Us
      Learn about our mission, values & team
    • Contact Us
      Contact sales for plans, pricing & advice
    • Sitemap
      Find info fast with our clear site map
My Account
Ahosting Logo
  • Hosting
    • Web Hosting
    • WordPress Hosting
    • FFMpeg Hosting
    • Reseller Hosting
    • VPS Hosting
    • Dedicated Server
    • WooCommerce Hosting
  • Domain
    • Register a Domain
    • Domain Transfer
    • Premium SSL Certificate
  • Support
    • Knowledge Base
    • Abuse Report
    • Submit A Ticket
  • Company
    • About Us
    • Contact Us
    • Blog
    • Sitemap
    • Datacenter
  • Legal
    • Privacy Policy
    • Terms of Service
    • Acceptable Use Policy
    • Service Level Agreement
    • Resource Abuse Policy
My Account

AHosting Blog

Category: WordPress

  • Disable WordPress AI Features in WordPress 7.0 (2026 Guide)

    Disable WordPress AI Features in WordPress 7.0 (2026 Guide)

    • How WordPress 7.0 Turned AI Connectors On by Default
    • How to Disable WordPress AI Features in 7.0
      • First, Back Up and Open a Staging Copy
      • Next, Open wp-config.php in cPanel File Manager
      • Then, Add the WP_AI_SUPPORT Constant
      • Finally, Verify That AI Support Is Off
    • Three Ways to Disable WordPress AI Features: Constant vs. Filter vs. Plugin
    • Disable WordPress AI Features: What's Covered and What Isn't
    • Optional: Hide the Settings → Connectors Screen With an mu-plugin
    • Diagnostic: Did You Fully Disable WordPress AI Features?
    • Editing wp-config.php Safely on AHosting WordPress Hosting
    • Frequently Asked Questions: Disable WordPress AI Features in 7.0
      • How do I disable WordPress AI features in WordPress 7.0?
      • WP_AI_SUPPORT constant vs. wp_supports_ai filter: which should I use?
      • Is it safe to disable WordPress AI features in 2026?
      • Should agencies disable WordPress AI features across client sites on AHosting reseller hosting?
      • Does WordPress 7.0 send my content to AI providers by default?
      • WP_AI_SUPPORT constant vs. the Turn Off AI Features plugin: which is more reliable?
      • Will disabling WordPress AI features also stop plugins that have their own AI?
      • What happens if I define WP_AI_SUPPORT as false on a WordPress multisite network?
      • Can I edit wp-config.php to disable AI on AHosting WordPress hosting in 2026?
      • Does AHosting support disabling WordPress AI features in 2026?
    TL;DR

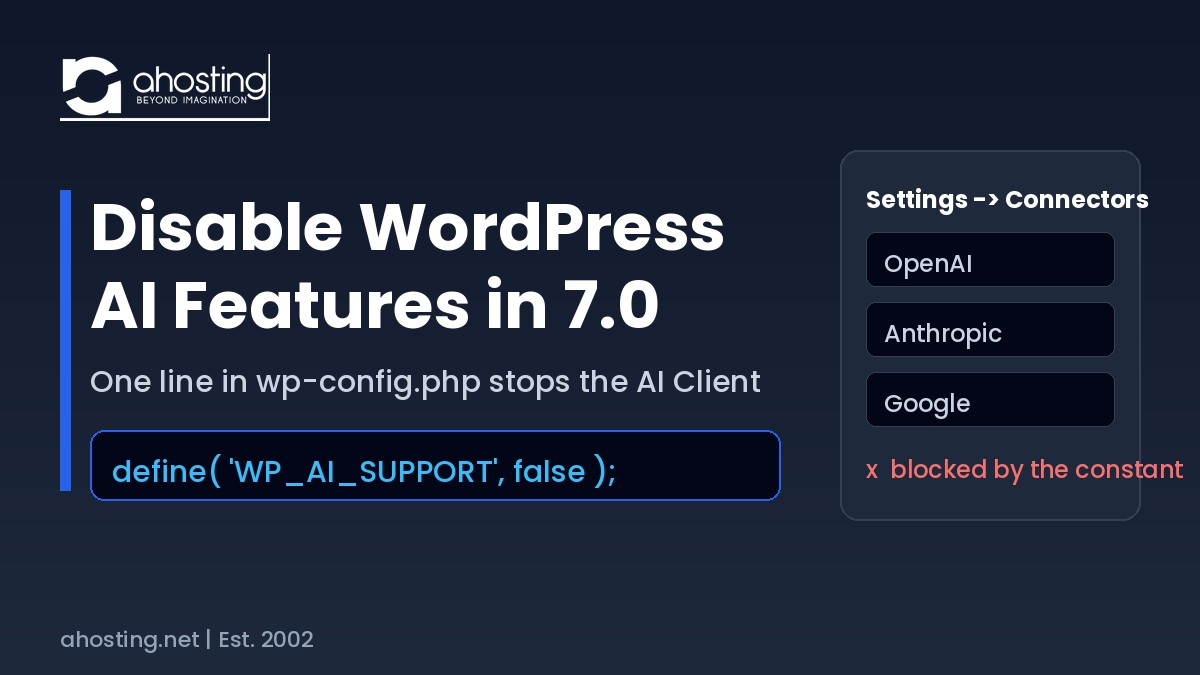
    To disable WordPress AI features in WordPress 7.0, add define( 'WP_AI_SUPPORT', false ); to wp-config.php. It overrides the wp_supports_ai filter, blocks every AI provider call site-wide, and a plugin cannot re-enable it.

    Disable WordPress AI Features: Audio Explainer

    WordPress 7.0 shipped a built-in AI Client and a Settings → Connectors screen that any administrator or editor can wire to OpenAI, Anthropic, or Google — and there is no dashboard switch to turn it back off. This guide shows how to disable WordPress AI features in minutes by adding one line to wp-config.php, then proving the change actually took effect. The whole fix is a single constant, but the reasons to apply it — contracts, data-protection rules, and a smaller attack surface — are worth understanding first.

    How WordPress 7.0 Turned AI Connectors On by Default

    WordPress 7.0, released May 20, 2026, added three AI building blocks to core: the AI Client (a provider-agnostic PHP API exposed through wp_ai_client_prompt()), the Connectors API, and a new Settings → Connectors admin screen. That screen lists three featured provider cards — OpenAI, Anthropic, and Google — and lets an administrator paste one API key that every compatible plugin then shares, as documented in the WordPress 7.0 Field Guide.

    Importantly, this infrastructure is inert until someone enters a key. WordPress core bundles no provider credentials, and per core changeset 61700, the platform “will not send prompts or data to any external service” without explicit configuration and explicit calling code. The provider-agnostic layer itself lives in the bundled WordPress php-ai-client library.

    However, “off until configured” is not the same as “safe to ignore.” Any user with the right capability can open Settings → Connectors and paste a key, at which point content can flow to a third-party model. Connector keys are also stored masked but not encrypted in the database (tracked in Trac #64789), so a live key can travel inside database dumps, staging refreshes, and backups. For a site under an NDA or a data-protection obligation, that is a surface most teams would rather remove than police. In practice, disabling the AI Client by default and opting sites in later is the cleaner policy — and it is one line.

    The WordPress 7.0 AI data path (and where to cut it) Editor / Plugin calls AI Client Settings -> Connectors stores provider API key OpenAI / Anthropic / Google your content leaves the server WP_AI_SUPPORT = false wp_supports_ai() returns false Cuts the path before any key is used

    How to Disable WordPress AI Features in 7.0

    To disable WordPress AI features, add define( 'WP_AI_SUPPORT', false ); to wp-config.php above the “stop editing” line, then confirm wp_supports_ai() returns false. The four steps below do exactly that, safely, using the tools included with your hosting.

    First, Back Up and Open a Staging Copy

    First and foremost, never edit wp-config.php straight on production. On AHosting, open cPanel, create a one-click staging clone, and confirm your daily backup is current so you have a restore point. Editing a staging copy first means a typo in the config file — the classic cause of a white screen — never touches your live site. If you also manage many sites, the same edit is easy to standardize across them, which is why the wp-config approach scales better than clicking through each dashboard.

    Next, Open wp-config.php in cPanel File Manager

    Next, in cPanel open File Manager, navigate to the site’s document root (typically public_html), select wp-config.php, and click Edit. Scroll to the line that reads /* That's all, stop editing! Happy publishing. */. Everything you add must go above that line, because WordPress ignores configuration defined after it. If you prefer SFTP, the same file in the same location works identically.

    Then, Add the WP_AI_SUPPORT Constant

    Then paste this single line above the “stop editing” comment and save. The constant is read at the very top of wp_supports_ai(), before any plugin or theme loads, which is why it is the most reliable off switch and cannot be reversed by a plugin at runtime, per the official wp_supports_ai reference.

    // Disable the WordPress 7.0 AI Client site-wide (enforced)
    define( 'WP_AI_SUPPORT', false );

    Finally, Verify That AI Support Is Off

    Finally, prove the fix took effect rather than assuming it. If you have terminal access, WP-CLI answers in one line and should print bool(false):

    wp eval "var_dump( wp_supports_ai() );"

    Alternatively, reload Settings → Connectors in wp-admin: with AI support off, provider connections no longer initialize. For a deeper look at editing configuration safely, our guide on why raising limits in wp-config often fails covers the same file and the two-ceiling gotcha that trips people up.

    Three Ways to Disable WordPress AI Features: Constant vs. Filter vs. Plugin

    Specifically, WordPress 7.0 gives you three levers, and they are not equal. The constant is enforced earliest and cannot be undone by a plugin; the filter is flexible but runs later and is override-able; a plugin is the no-code option for owners who cannot edit wp-config.php. The developer-friendly filter version, popularized in Shawn Hooper’s write-up, looks like this:

    add_filter( 'wp_supports_ai', static function ( $supported ) {
        return false;
    }, 1000 );

    Table 1 compares the three methods so you can match the lever to the site. Use it as a standalone reference when deciding what to deploy across a fleet versus a single site you fully control.

    Table 1 — WordPress 7.0 AI Disable Methods Compared
    Method Where it lives Can an editor undo it? Hides Connectors screen? Best for
    WP_AI_SUPPORT constant wp-config.php No — loads before plugins No (add the mu-plugin) Production sites, whole fleets
    wp_supports_ai filter Theme or snippet Yes — a later hook can override No Single sites you fully control
    Disable-AI plugin Plugins screen Yes — if deactivated Yes (most hide it) No-code owners, locked wp-config

    Consequently, the plugin route matters on managed platforms where wp-config.php is not directly editable. Two well-maintained options are “Turn Off AI Features” and “Disable AI for Security,” both of which wrap the same wp_supports_ai filter and add an admin badge. On AHosting you have full cPanel access, so the constant remains the recommended path.

    Disable WordPress AI Features: What’s Covered and What Isn’t

    In practice, the constant is comprehensive for core AI but has one honest boundary: it only governs code that checks wp_supports_ai(). Plugins that ship their own AI integration — rather than calling the core client — are unaffected and must be handled in their own settings. Table 2 draws that line clearly so you do not assume more coverage than the constant provides.

    Table 2 — What WP_AI_SUPPORT = false Stops (and What It Doesn’t)
    Surface Covered by the constant?
    Core AI Client calls (wp_ai_client_prompt()) Yes — short-circuited site-wide
    Featured connectors (OpenAI / Anthropic / Google) Yes — no prompts run, keys stay inert
    Settings → Connectors admin screen visibility No — still visible unless you add the mu-plugin
    Plugins with their own bundled AI No — disable each plugin’s AI separately

    Optional: Hide the Settings → Connectors Screen With an mu-plugin

    Additionally, the constant blocks AI calls but leaves the Settings → Connectors menu item visible. To remove it and block direct access, drop a small must-use plugin into wp-content/mu-plugins/ — a location that loads automatically, survives theme switches, and cannot be deactivated from the Plugins screen. The removal hooks admin_menu at a high priority (not admin_init, which would break admin-ajax) using the core remove_submenu_page function:

    <?php
    /**
     * Plugin Name: Hide WordPress AI Connectors
     * Description: Removes Settings -> Connectors and blocks direct access.
     */
    add_action( 'admin_menu', function () {
        remove_submenu_page( 'options-general.php', 'options-connectors.php' );
    }, 999 );
    
    add_action( 'admin_init', function () {
        global $pagenow;
        if ( 'options-connectors.php' === $pagenow ) {
            wp_safe_redirect( admin_url() );
            exit;
        }
    } );

    That said, screen names can change between releases, so treat the mu-plugin as belt-and-suspenders on top of the constant, not a replacement for it. The constant is what actually stops the AI calls; hiding the menu just removes the temptation.

    Diagnostic: Did You Fully Disable WordPress AI Features?

    Interestingly, most “still exposed” sites have the constant right but miss the two edge cases: the visible Connectors screen and plugins with their own AI. Answer the four checks below to see exactly where your site stands.

    AI Connector Exposure Check

    1. Is your site running WordPress 7.0 or newer?

    Yes No

    2. Is define( ‘WP_AI_SUPPORT’, false ); in your wp-config.php?

    Yes No

    3. Have you hidden the Settings -> Connectors screen (mu-plugin)?

    Yes No

    4. Do any active plugins ship their own built-in AI?

    Yes No
    Answer all four to see your exposure verdict.

    Editing wp-config.php Safely on AHosting WordPress Hosting

    Fortunately, the riskiest part of this fix is not the constant — it is editing wp-config.php without a safety net. Every AHosting WordPress hosting plan ships one-click staging, daily backups, and cPanel File Manager, so you can test the edit on a clone and restore instantly if anything looks off. That staging-plus-backup workflow is the same one we recommend in our server-level WordPress security guide.

    Moreover, if you run AI features intentionally, they make outbound calls from your server to provider endpoints — and every AHosting plan includes a free dedicated IP, so those calls carry a stable, isolated identity rather than a shared reputation. Agencies standardizing an AI-off policy across many client sites can do it per account on white-label reseller hosting, and sites that have simply outgrown shared concurrency can move the same configuration onto managed VPS without changing a line of it. For the full pre-update picture, see our WordPress 7.0 hosting requirements checklist.

    Frequently Asked Questions: Disable WordPress AI Features in 7.0

    How do I disable WordPress AI features in WordPress 7.0?

    Specifically, add define( 'WP_AI_SUPPORT', false ); to your wp-config.php file above the “stop editing” comment. The core function wp_supports_ai() then returns false everywhere, so no provider connector or AI-aware feature runs.

    WP_AI_SUPPORT constant vs. wp_supports_ai filter: which should I use?

    Fundamentally, the WP_AI_SUPPORT constant is the stronger control because it is read at the top of wp_supports_ai() before any plugin loads, so nothing can override it. The wp_supports_ai filter runs later and a higher-priority plugin can undo it.

    Is it safe to disable WordPress AI features in 2026?

    Yes. Disabling WordPress AI features only short-circuits the core AI Client; it does not affect posts, editing, media, or any non-AI functionality. You can re-enable it in seconds by removing the constant.

    Should agencies disable WordPress AI features across client sites on AHosting reseller hosting?

    Typically, defaulting AI off is the lower-risk posture for agencies. On AHosting reseller hosting each client account is isolated, so you can set WP_AI_SUPPORT per account and opt a client in only when their contract allows external AI processing.

    Does WordPress 7.0 send my content to AI providers by default?

    Notably, no. WordPress core ships no AI provider keys and, per changeset 61700, will not send prompts or data externally without explicit configuration and explicit calling code. The risk is that an editor can add a connector key later.

    WP_AI_SUPPORT constant vs. the Turn Off AI Features plugin: which is more reliable?

    Typically, the constant is more reliable for production because it lives in wp-config.php and cannot be deactivated from the Plugins screen. A plugin is easier for non-technical owners but only enforces the setting while it stays active.

    Will disabling WordPress AI features also stop plugins that have their own AI?

    Importantly, no. WP_AI_SUPPORT gates only plugins that call the core AI Client. A plugin bundling its own AI integration ignores the setting, so you must disable that plugin’s AI separately in its own settings.

    What happens if I define WP_AI_SUPPORT as false on a WordPress multisite network?

    On multisite, the constant applies network-wide from wp-config.php, so every subsite has AI off at once. The Settings → Connectors screen can still appear on subsites, so pair the constant with the optional mu-plugin to hide it.

    Can I edit wp-config.php to disable AI on AHosting WordPress hosting in 2026?

    Yes. Every AHosting WordPress plan includes cPanel File Manager, one-click staging, and daily backups, so you can edit wp-config.php on a staging clone, verify the fix, and push it live with a restore point in place.

    Does AHosting support disabling WordPress AI features in 2026?

    Indeed. AHosting runs WordPress 7.0 on LiteSpeed with cPanel access on every plan, so the WP_AI_SUPPORT constant, the wp_supports_ai filter, and the mu-plugin method all work without a support ticket.
    July 17, 2026
  • How to Disable the WordPress Heartbeat (Before It Eats Your PHP Workers)

    How to Disable the WordPress Heartbeat (Before It Eats Your PHP Workers)

    • What the WordPress Heartbeat Actually Does (And Why It Costs You If You Don't Disable WordPress Heartbeat)
      • The uncacheable-path problem in one sentence
      • Heartbeat is not WP-Cron — do not confuse the two
    • See the Problem: Watch Heartbeat Fire in Your Own Browser
    • Heartbeat Worker Cost vs Your AHosting Plan (The Numbers)
    • How to Disable WordPress Heartbeat Safely in 4 Steps
      • First Step: Choose Where the Code Lives
      • Second Step: Add the Throttle-and-Scope Filter To Disable WordPress Heartbeat
      • Third Step: Save and Clear Cache
      • Fourth Step: Verify in the Network Panel
    • Plugin vs Filter vs LiteSpeed Toggle: Which Method to Use
    • Heartbeat Decision Checker: Throttle, Scope, or Disable WordPress Heartbeat?
    • When Disabling Heartbeat Is a Symptom of Outgrowing Your Plan
    • Frequently Asked Questions: Disabling the WordPress Heartbeat
      • Does disabling the WordPress Heartbeat break autosave or post locking?
      • What is the safest way to disable the WordPress Heartbeat in 2026?
      • Heartbeat Control plugin vs the heartbeat_settings filter: which should I use?
      • Disable WordPress Heartbeat in functions.php or in a snippet plugin: what is the difference?
      • How much server load does the WordPress Heartbeat cause on AHosting shared hosting in 2026?
      • Why does admin-ajax.php show high CPU even when my WordPress site has no traffic?
      • Does AHosting's LiteSpeed cache stop Heartbeat from consuming PHP workers without needing to disable WordPress Heartbeat?
      • Should I throttle the WordPress Heartbeat or disable WordPress Heartbeat on a 2026 WooCommerce store?
      • Is the WordPress Heartbeat the same thing as WP-Cron?
      • Will my WordPress 7.0 dashboard on AHosting be faster if I disable WordPress Heartbeat?
    TL;DR

    To disable WordPress Heartbeat safely, throttle its interval to 60 seconds and deregister it on the front end with one heartbeat_settings filter — this cuts admin-ajax.php load about 75% while keeping autosave and post locking.

    Listen: why the Heartbeat costs PHP workers and how one filter fixes it. By Matt Chrust, Director of Business Development, AHosting.

    If you want to disable WordPress Heartbeat, the goal is almost never to kill it outright — it is to stop it from quietly flooding admin-ajax.php with requests that consume PHP workers while nobody is reading your site. The Heartbeat API polls your server on a timer every time an admin or editor tab is open, and because that request path cannot be cached, even a well-tuned WordPress hosting stack serves each tick through PHP. Fortunately, one filter fixes it without breaking autosave.

    Notably, this is a silent cost. There is no error, no warning, and no visible slowdown until concurrency stacks up and the server starts queuing requests. Below, we show you how to confirm the problem in your own browser, apply the safe fix, verify it worked, and — using AHosting’s published PHP-worker counts — see exactly how much of your plan the Heartbeat can occupy.

    What the WordPress Heartbeat Actually Does (And Why It Costs You If You Don’t Disable WordPress Heartbeat)

    Specifically, the Heartbeat API is a polling system introduced in WordPress 3.6 that lets your browser talk to the server on a fixed interval — a “tick” every 15 to 120 seconds. It powers autosave, post locking (so two editors do not overwrite each other), session expiry warnings, and plugin notifications. Under the hood it is a classic AJAX request pattern. According to the WordPress Heartbeat API handbook, each tick sends a POST to admin-ajax.php, the server prepares a response, and the browser waits for it.

    However, the design has a sharp edge. In practice the tick runs whether or not the site has visitors, and the admin-ajax.php path is uncacheable — it bypasses page caching entirely and executes PHP on every call. Consequently, an open dashboard left in a background tab keeps spending server resources on nothing. Multiply that by several editors, several tabs, and a few plugins hooking the stream, and you get high CPU that looks mysterious because traffic is low.

    The uncacheable-path problem in one sentence

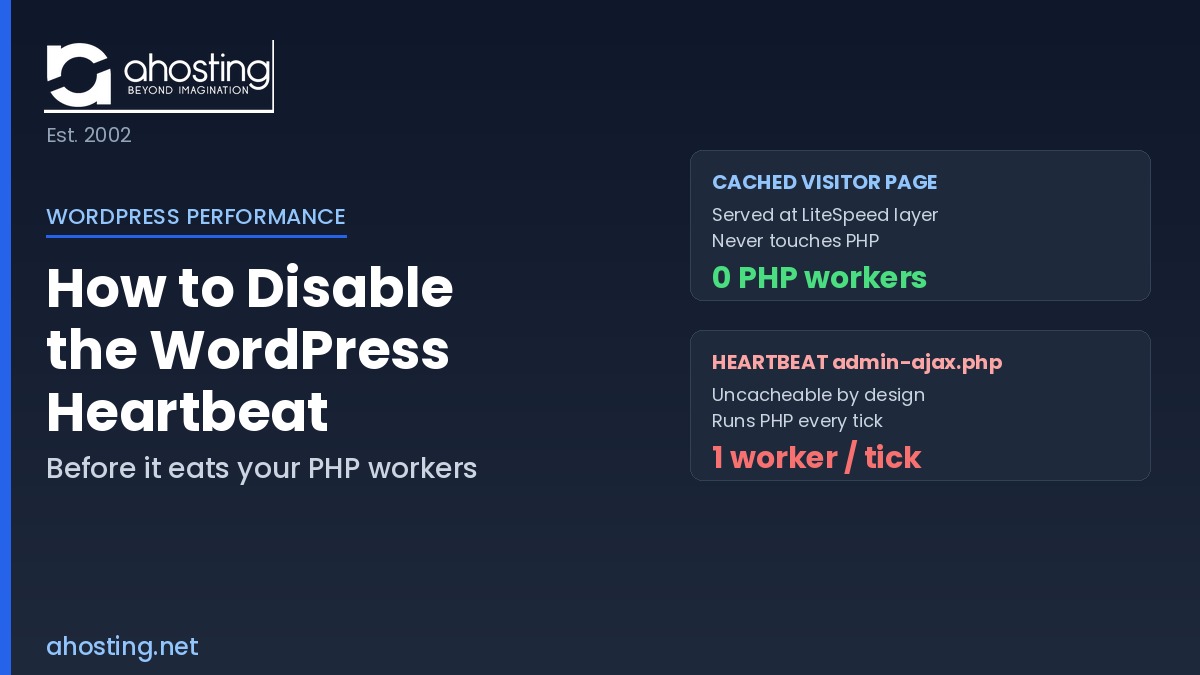
    Ultimately, this is why “just add more caching” does not help. Server-level caching — including the LiteSpeed and LSCache stack AHosting runs — serves a cached visitor page with zero PHP workers, but it cannot cache a logged-in admin-ajax.php POST. Therefore every Heartbeat tick is a full dynamic request. The fix is not more cache; it is fewer, smarter ticks. For the deeper server-side picture, our companion guide on the server-side factors no plugin can fix covers the caching layer in full.

    Heartbeat is not WP-Cron — do not confuse the two

    Importantly, the Heartbeat is often mistaken for WP-Cron, and the mix-up leads people to apply the wrong fix. In contrast, WP-Cron runs scheduled server tasks triggered on page loads, while the Heartbeat is a browser-to-server poll that only runs while an admin tab is open. They are separate subsystems on separate triggers. If your issue is scheduled jobs stacking up rather than idle-tab polling, see our guide on why WP-Cron fails and how to replace it instead.

    See the Problem: Watch Heartbeat Fire in Your Own Browser

    First, confirm the symptom before you change anything. Open any post in the editor, press F12 to open your browser’s developer tools Network panel, and watch the request list. Type admin-ajax into the filter box, then simply wait — without touching the keyboard. Within about 15 seconds a POST request to admin-ajax.php appears; roughly 15 seconds later, another. That steady pulse, with no visitor activity, is the Heartbeat.

    Furthermore, you can watch the same pattern in your hosting resource graphs. On a CloudLinux account, sustained admin-ajax.php processes appearing in the process list — often flagged near a 508 “resource limit reached” event — are the Heartbeat and similar loopback calls competing for the same PHP workers your visitors need. That connection to your plan’s worker ceiling is the part most guides skip, so we quantify it next.

    Cached visitor request vs uncacheable Heartbeat request A cached visitor page is served at the LiteSpeed cache layer using zero PHP workers, while each Heartbeat admin-ajax tick bypasses cache and consumes one PHP worker. Two requests, two very different costs CACHED VISITOR PAGE Served at the LiteSpeed layer Never touches PHP 0 PHP workers HEARTBEAT admin-ajax.php Uncacheable by design Runs PHP every tick 1 worker / tick AHosting.net — Est. 2002

    Heartbeat Worker Cost vs Your AHosting Plan (The Numbers)

    Here is the data no generic tutorial can give you, because it requires knowing the host’s real worker counts. AHosting publishes its PHP worker (entry-process) allocation per plan — Bronze 15, Silver 25, Gold 40 — so we can map the Heartbeat’s appetite directly onto a ceiling. Each open post-editor tab ticks about four times per minute, and each tick occupies one worker on the uncacheable path. The table below shows what that means as concurrent editors climb.

    Open post-editor tabs (15s ticks)Ticks / minShare of Bronze (15 EP)Share of Silver (25 EP)Share of Gold (40 EP)
    1 editor47%4%2%
    2 editors813%8%5%
    5 editors2033%20%12%
    10 editors4067%40%25%
    15 editors60100%60%38%
    Heartbeat Worker Cost vs AHosting Plan EP Ceiling. Each open post-editor tab ticks ~4×/min; each tick is one uncacheable admin-ajax.php request occupying one PHP worker. Cached visitor pages consume zero workers. Source: AHosting published per-plan entry-process counts.

    Consequently, the headline figure is stark: 15 editors with post-editor tabs open can occupy 100% of a Bronze plan’s PHP workers — spent entirely on polling, with zero visitors served. Even at throttled 60-second intervals, that pressure drops roughly fourfold, which is precisely why throttling beats brute-force disabling for busy teams. If your concurrency is regularly pushing these numbers, that is a genuine signal to move to a plan with more workers or to WordPress VPS hosting with dedicated resources.

    How to Disable WordPress Heartbeat Safely in 4 Steps

    Here is the shortest correct fix: add one heartbeat_settings filter that raises the interval to 60 seconds and deregisters Heartbeat on the front end, leaving the editor’s autosave and post locking intact. The four steps below walk through it and verify the result.

    First Step: Choose Where the Code Lives

    First, decide where to put the snippet. A code-snippet plugin such as WPCode or Code Snippets is the durable choice because it survives theme switches; a child theme’s functions.php works too but disappears if you change themes. Either way, you are adding a small PHP filter — no core files are touched. Avoid pasting into the parent theme’s functions.php, since a theme update will overwrite it.

    Second Step: Add the Throttle-and-Scope Filter To Disable WordPress Heartbeat

    Next, add the filter below. The first function raises the tick interval to the maximum 60 seconds; the second stops Heartbeat entirely on the public front end, where logged-out visitors gain nothing from it. Together they keep the editor fully functional while removing the bulk of the load. The heartbeat_settings hook reference documents the interval values (anything 15–120).

    // 1. Throttle Heartbeat to the maximum 60-second interval.
    add_filter( 'heartbeat_settings', 'ah_throttle_heartbeat' );
    function ah_throttle_heartbeat( $settings ) {
        $settings['interval'] = 60; // allowed range is 15-120
        return $settings;
    }
    
    // 2. Disable Heartbeat on the public front end only.
    add_action( 'init', 'ah_disable_frontend_heartbeat', 1 );
    function ah_disable_frontend_heartbeat() {
        if ( ! is_admin() ) {
            wp_deregister_script( 'heartbeat' );
        }
    }

    Third Step: Save and Clear Cache

    Then save the snippet (or update functions.php) and clear any page cache so the front-end change takes effect. On a LiteSpeed host, purge LSCache; if OPcache is active on your PHP pool, the new function may take a few seconds to load, so allow a moment before testing. No visitor-facing markup changes, so there is nothing to break on the front end.

    Fourth Step: Verify in the Network Panel

    Finally, prove it worked. Reload the post editor, open developer tools, and filter the Network panel to admin-ajax again. Where you previously saw a request every 15 seconds, you should now see roughly one per minute — about 75% fewer calls. Type a word in the draft and confirm the “Saving… / Saved” autosave indicator still fires. If it does, you have throttled the Heartbeat without losing the features that matter.

    Plugin vs Filter vs LiteSpeed Toggle: Which Method to Use

    Above all, pick the method that matches how you manage the site. The filter is the lightest; a plugin is the most approachable; the LiteSpeed Cache toggle is convenient if you already run that plugin. All three reach the same outcome — fewer admin-ajax.php calls — so the decision is about maintainability, not capability.

    MethodBest forTrade-off
    heartbeat_settings filterDevelopers; leanest installRequires editing PHP
    Heartbeat Control / snippet pluginNon-coders; theme-independentOne more plugin to maintain
    LiteSpeed Cache toggleSites already on LSCacheOnly if LSCache is installed
    Three routes to the same result; choose by maintainability.

    Moreover, the choice interacts with your other plugins. If a page builder such as Elementor, or a WooCommerce extension, depends on Heartbeat for editor or cart behavior, prefer the throttle-only route rather than deregistering the script — a point the interactive checker below helps you decide. For a store specifically, the same worker math applies to checkout, which we cover in our WooCommerce hosting breakdown.

    Heartbeat Decision Checker: Throttle, Scope, or Disable WordPress Heartbeat?

    Use the checker below to get a recommendation based on your setup. It maps three common answers to the safe action so you do not accidentally disable a feature your site relies on.

    Heartbeat Decision Checker

    What does your site depend on? Pick the closest match.

    Your setup

    See AHosting WordPress plans

    When Disabling Heartbeat Is a Symptom of Outgrowing Your Plan

    Finally, treat a chronic Heartbeat problem as a signal, not just a nuisance. Occasionally, throttling is enough forever. But if you are throttling, deregistering, and still bumping the worker ceiling during normal editing, the real constraint is concurrency headroom. As the table above shows, the same tick count that occupies 100% of a Bronze plan barely touches a Gold plan — the difference is published worker allocation, not a hidden setting.

    Therefore, the durable fix for a growing team is more workers behind the same polling, which is what higher shared tiers and VPS provide. Heartbeat tuning buys you room; capacity buys you certainty. Size the plan against the concurrency math in this guide, and you will stop firefighting admin-ajax.php for good.

    Last updated: July 15, 2026

    Frequently Asked Questions: Disabling the WordPress Heartbeat

    Does disabling the WordPress Heartbeat break autosave or post locking?

    Specifically, disabling Heartbeat everywhere removes autosave and post locking, but throttling it to 60 seconds keeps both while cutting requests by about 75 percent. Therefore the recommended pattern is throttle in the editor, disable on the front end. The filter earlier in this guide does exactly that.

    What is the safest way to disable the WordPress Heartbeat in 2026?

    Generally, the safest way to disable the WordPress Heartbeat in 2026 is to throttle the interval to 60 seconds and deregister the script only on the front end, leaving the editor untouched. Consequently autosave and post locking keep working while admin-ajax.php load drops sharply.

    Heartbeat Control plugin vs the heartbeat_settings filter: which should I use?

    In practice, the heartbeat_settings filter is lighter because it adds no plugin overhead, while the Heartbeat Control plugin is friendlier if you avoid code. Both reach the same result. The comparison table above maps each method to the resource cost it removes.

    Disable WordPress Heartbeat in functions.php or in a snippet plugin: what is the difference?

    Notably, a functions.php edit is theme-bound and disappears on theme switch, whereas a code-snippet plugin survives theme changes and is easier to toggle. Therefore a snippet plugin is the more durable place to disable the WordPress Heartbeat on a production site.

    How much server load does the WordPress Heartbeat cause on AHosting shared hosting in 2026?

    Concretely, each Heartbeat tick is one uncacheable admin-ajax.php request that consumes one PHP worker for its duration. As a result, fifteen open editor tabs can occupy every worker on an entry-level plan. The plan-by-plan table above shows exactly where that ceiling sits on Bronze, Silver, and Gold.

    Why does admin-ajax.php show high CPU even when my WordPress site has no traffic?

    Fundamentally, admin-ajax.php runs the Heartbeat API on a timer, so it fires whether or not visitors are on the site. Because that path bypasses page caching, LiteSpeed cannot absorb it. In other words, the CPU is spent polling from an open admin tab, not serving readers.

    Does AHosting's LiteSpeed cache stop Heartbeat from consuming PHP workers without needing to disable WordPress Heartbeat?

    Unfortunately no, because admin-ajax.php is uncacheable by design, so LiteSpeed serves it through PHP like any dynamic request. However, AHosting publishes its per-plan worker counts, so you can size the Heartbeat cost against a known ceiling rather than guessing.

    Should I throttle the WordPress Heartbeat or disable WordPress Heartbeat on a 2026 WooCommerce store?

    Typically, throttle rather than disable when a WooCommerce store or membership plugin depends on Heartbeat for cart, stock, or session updates. Accordingly, set the interval to 60 seconds instead of deregistering the script, so real-time features survive while load falls.

    Is the WordPress Heartbeat the same thing as WP-Cron?

    No, and confusing the two leads to the wrong fix. Whereas WP-Cron runs scheduled server tasks on page load, the Heartbeat is a browser-to-server poll that only runs while an admin tab is open. Disabling one does nothing to the other.

    Will my WordPress 7.0 dashboard on AHosting be faster if I disable WordPress Heartbeat?

    Often yes, because a sluggish WordPress 7.0 dashboard is frequently a Heartbeat storm from several open editor tabs rather than a slow server. After you disable the WordPress Heartbeat on the front end and throttle the editor, admin-ajax.php pressure drops and the dashboard feels lighter.

    July 15, 2026
  • Is WP-Cron Actually Slowing Your Site?

    Is WP-Cron Actually Slowing Your Site?

    • Why We Measured WP-Cron Instead of Just Telling You to Disable WP-Cron It
    • What an Empty WP-Cron Check Actually Costs: 18 Milliseconds
      • The Three Numbers: 18 ms vs 475 ms vs 1,540 ms
      • Why wp-cron.php Returns Zero Bytes (And Why That Is Healthy)
    • The Audit: 26 WordPress Installs, 676 Scheduled Events, Zero Overdue
      • Not One Site Had Disabled WP-Cron
      • What 26 Events Per Install Tells You About Plugin Bloat
    • When You Should Disable WP-Cron: The Four Conditions
      • Condition One: Your Scheduled Jobs Are Time-Critical
      • Condition Two: Low Traffic Plus a Deadline
      • Condition Three: A Heavy Queue, Not a Long One
      • Condition Four: You Are Near Your Entry Process Ceiling
    • How to Disable WP-Cron the Right Way: The cPanel Walkthrough
      • First Step: Create the Server Cron in cPanel
      • Second Step: Add DISABLE_WP_CRON to wp-config.php to Disable WP-Cron
      • Third Step: Choose WP-CLI Over curl or wget
      • Fourth Step: Verify the Cron Actually Fired After You Disable WP-Cron
    • WP-Cron vs Server Cron on CloudLinux: The Entry Process Difference
    • The Disable WP-Cron Decision Checker
    • A Practical Checklist: Should You Disable WP-Cron?
    • Frequently Asked Questions: Disabling WP-Cron
      • Should I disable WP-Cron on a low-traffic WordPress site in 2026?
      • What happens if I disable WP-Cron and forget to add a server cron?
      • WP-Cron vs system cron: which is more reliable for scheduled posts?
      • How much does WP-Cron actually slow down a WordPress page load?
      • Does AHosting run a server cron for WordPress accounts by default?
      • WP-CLI vs curl vs wget for a WordPress server cron: which should I use?
      • How many entry processes does a wp-cron.php request consume on AHosting?
      • When should I disable WP-Cron on a WooCommerce store with Action Scheduler queues?
      • Is DISABLE_WP_CRON still recommended for WordPress in 2026?
      • What cron interval does AHosting recommend for WordPress in 2026?
    TL;DR

    We measured before telling anyone to disable wp-cron. An empty WP-Cron check costs 18 ms, just 1.17% of an uncached page load. On 100% of the WordPress installs we audited, the default was fine.

    Every guide telling you to disable wp-cron makes the same claim: WordPress fires its pseudo-cron on every page load, and that overhead is dragging your site down. Notably, none of them publishes a number. Therefore we measured it on our own production hardware, and the result reframes the entire recommendation.

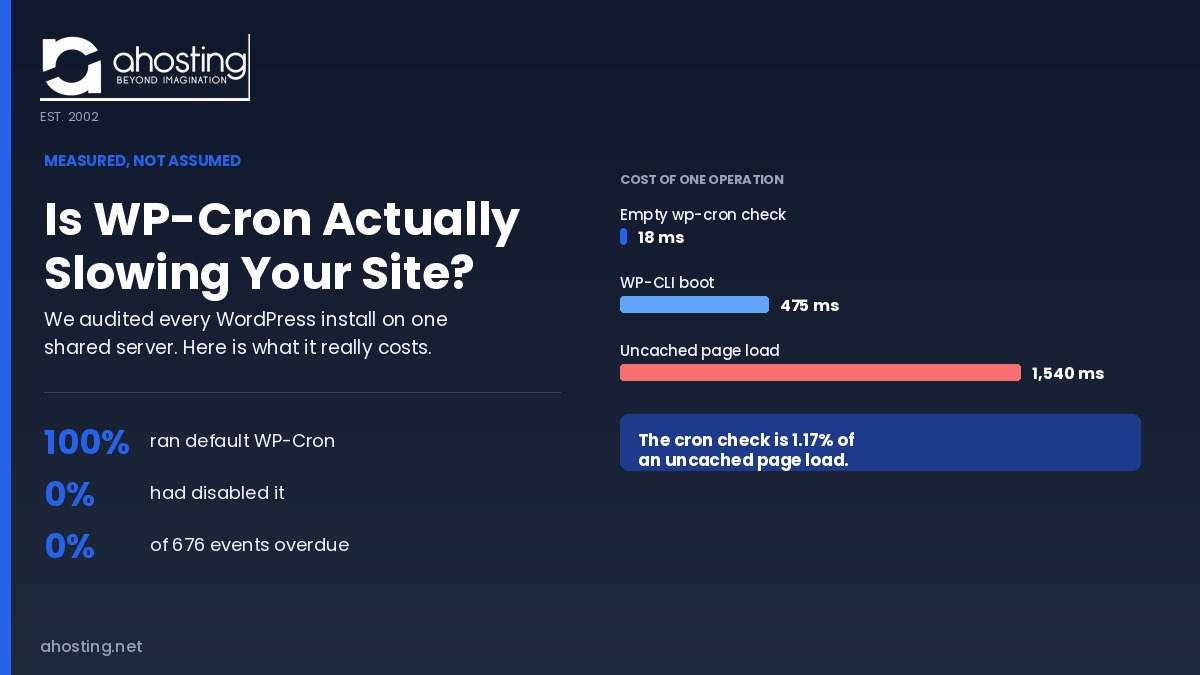
    Specifically, an empty WP-Cron check costs 18 milliseconds. On the same account, an uncached WordPress page load costs 1,540 milliseconds. In other words, the thing everyone tells you to remove accounts for roughly one percent of the request it rides along inside.

    Why We Measured WP-Cron Instead of Just Telling You to Disable WP-Cron It

    The advice to disable wp-cron is repeated almost universally, and it is repeated without evidence. Specifically, we searched the top-ranking pages for this topic and found the same assertion on every one of them, with no supporting measurement on any of them. Consequently, site owners disable a core WordPress subsystem on the strength of an unverified claim, and a meaningful share of them break their scheduled tasks in the process.

    Furthermore, we are in an unusual position to check. We run the servers. Therefore, rather than repeat the claim, we audited every WordPress installation on one of our shared hosting servers and timed the operations directly. In practice, that turns a talking point into a measurement, and the measurement disagrees with the talking point.

    What an Empty WP-Cron Check Actually Costs: 18 Milliseconds

    An empty WP-Cron check costs 18 milliseconds on AHosting’s LiteSpeed stack. Specifically, that is the time for PHP to boot WordPress, read the scheduled event queue, find nothing due, and exit. Consequently, when people describe WP-Cron as a performance drain, this 18 millisecond operation is the drain they are describing.

    The Three Numbers: 18 ms vs 475 ms vs 1,540 ms

    Context turns that 18 milliseconds from a number into an argument. Specifically, we timed three operations on the same WordPress account, on the same server, within the same minute. In contrast to the assumption behind the standard advice, the cron check is the cheapest thing on the list by a wide margin.

    Operation (measured on AHosting sh193, July 14, 2026)CostRelative to the cron check
    Empty wp-cron.php check (PHP boots, no jobs due)18 ms1x (baseline)
    Same WordPress boot via WP-CLI475 ms26x
    Uncached homepage load, same account1,540 ms86x
    The AHosting WP-Cron Cost Table. The WP-Cron check represents 1.17% of an uncached WordPress page load.

    Therefore the conclusion writes itself. If an uncached page load takes 1,540 milliseconds and the WP-Cron check inside it takes 18, then removing WP-Cron addresses 1.17 percent of the problem while leaving 98.83 percent untouched. Ultimately, if your WordPress site feels slow, WP-Cron is not why. Your caching layer is why, and our guide to server-level LiteSpeed caching for WordPress addresses the other 98.83 percent.

    Why wp-cron.php Returns Zero Bytes (And Why That Is Healthy)

    A healthy wp-cron.php request returns HTTP 200 with an empty response body. Specifically, WordPress executes any due jobs and then terminates without printing anything, so zero bytes is the signature of success rather than a symptom of failure. Notably, this trips up a lot of troubleshooting, because an empty response looks broken to anyone expecting output.

    Furthermore, you can confirm PHP genuinely ran by inspecting the response headers. In practice, WordPress emits its own no-cache headers on this endpoint, including a deliberately absurd expiry date set in 1984. As a result, if you see that header, PHP executed. If you see a cache header instead, your request never reached WordPress at all and any timing you take from it is meaningless.

    Notably, the reason the check is this cheap is architectural. Specifically, WordPress fires the cron request as a non-blocking loopback with a 0.01 second timeout, so the visitor’s page load never waits for the cron work to finish. In fact, WordPress core contributors debated raising that timeout for seventeen years before closing the ticket, precisely because the fire-and-forget design is the thing keeping the cost off your page load.

    The Audit: 26 WordPress Installs, 676 Scheduled Events, Zero Overdue

    On July 14, 2026 we audited every WordPress installation on one AHosting shared hosting server. Specifically, this was a census rather than a sample: 26 installations, all of them, with no selection applied. Consequently the percentages below describe the whole population on that machine, not an estimate drawn from part of it.

    Not One Site Had Disabled WP-Cron

    100 percent of the WordPress installations were running WP-Cron in its default configuration. Specifically, 0 percent had DISABLE_WP_CRON set in wp-config.php, and 0 percent had a replacement server cron of any kind. Therefore, despite the advice being one of the most widely repeated optimizations in WordPress, adoption on a real shared server was nil.

    AHosting sh193 WP-Cron Census (all installs, July 14, 2026)CountPercent of total
    WordPress installations audited26100%
    Running default WP-Cron26100%
    With DISABLE_WP_CRON set00%
    With a replacement server cron00%
    Serving no reachable frontend1038.5%
    Scheduled events across all installs676avg 26 per install
    Events overdue00%
    The AHosting WP-Cron Census. Every WordPress install on one shared server, audited in full.

    Notably, the overdue figure is the one that matters. Specifically, across 676 scheduled events on 26 sites, 0 percent were overdue. In other words, the failure mode that the entire disable-wp-cron recommendation exists to prevent was not occurring on any site we examined. As a result, the default configuration was doing its job on 100 percent of the population.

    Furthermore, 38.5 percent of these installations were serving no reachable frontend at all, and even those had zero overdue events. In practice, that is the strongest possible test of the traffic-dependency argument, because these are the sites that should have been starved of the page loads WP-Cron depends on. They were not.

    What 26 Events Per Install Tells You About Plugin Bloat

    The average WordPress installation on the server carried 26 scheduled events. Specifically, a clean WordPress core install schedules roughly a dozen, so the remainder arrives with plugins. Consequently, the size of your cron queue is a reasonable proxy for how much background work your plugin stack has quietly signed you up for.

    Therefore the queue length is worth checking even if you never disable wp-cron. In practice, an install carrying 40 or more events is usually running duplicate scheduling from a misbehaving plugin, and the WordPress Plugin Handbook warns that calling wp_schedule_event on every page load can register the same task thousands of times.

    The WP-Cron Cost, Measured: 18 ms Against a 1,540 ms Page Load AHosting audited all 26 WordPress installs on shared server sh193 on July 14, 2026. An empty wp-cron.php check took 18 milliseconds, a WP-CLI boot took 475 milliseconds, and an uncached homepage took 1,540 milliseconds. The cron check is 1.17 percent of the page load. 100 percent of installs ran default WP-Cron, 0 percent had it disabled, and 0 percent of 676 scheduled events were overdue. AHOSTING.NET EST. 2002 The WP-Cron Tax, Measured sh193 shared server · all 26 WordPress installs · July 14, 2026 COST OF ONE OPERATION Empty wp-cron.php check 18 ms WP-CLI WordPress boot 475 ms Uncached page load 1,540 ms The WP-Cron check is 1.17% of an uncached page load. RAN DEFAULT WP-CRON 100% HAD IT DISABLED 0% OF 676 EVENTS OVERDUE 0% EVENTS / INSTALL 26

    When You Should Disable WP-Cron: The Four Conditions

    You should disable wp-cron when at least one of four specific conditions applies to your site. Notably, none of them is “your site feels slow,” because we have now measured that the cron check contributes 1.17 percent of a page load. In contrast, each condition below describes a real failure that the default configuration genuinely cannot handle.

    Condition One: Your Scheduled Jobs Are Time-Critical

    Disable wp-cron when a job must run at a specific time rather than eventually. Specifically, WP-Cron has no clock of its own; it inherits the timing of your traffic. Consequently a backup scheduled for 3:00 AM on a site with no overnight visitors runs whenever the first morning visitor arrives, which may be 7:00 AM. In practice, if the difference between 3:00 AM and 7:00 AM matters to you, that is a reliability requirement and only a server cron satisfies it.

    Condition Two: Low Traffic Plus a Deadline

    Disable wp-cron when your site has genuinely sparse traffic and something depends on a schedule. Specifically, this is the classic case the WordPress Plugin Handbook’s cron documentation describes: schedule a task for 2:00 PM, receive no page loads until 5:00 PM, and the task runs three hours late. Notably, our audit found zero overdue events even on sites with no reachable frontend, so this failure is less common than assumed, but it is real when it happens.

    Condition Three: A Heavy Queue, Not a Long One

    Disable wp-cron when your queue contains expensive jobs rather than merely numerous ones. Specifically, our 18 millisecond measurement is the cost of checking an empty queue, and that figure rises with the work actually due. Therefore a WooCommerce store draining a large Action Scheduler backlog is a genuinely different case from a blog with 26 idle events, and our WooCommerce-optimized hosting plans allocate 25 entry processes precisely because checkout and queue work compete for the same pool.

    Condition Four: You Are Near Your Entry Process Ceiling

    Disable wp-cron when you are already close to your concurrency limit, because every cron run occupies a worker that a visitor could be using. Specifically, on CloudLinux each PHP request consumes one entry process, and CloudLinux’s resource limit documentation explains that exceeding the ceiling queues or rejects requests. Consequently, if you are already seeing 508 resource limit errors during traffic spikes, cron work is competing with real visitors and moving it to WP-CLI removes it from the pool entirely.

    How to Disable WP-Cron the Right Way: The cPanel Walkthrough

    Build the replacement cron first, then disable the page-load trigger. Specifically, doing it in the reverse order leaves a window in which no scheduled task runs at all, and because WordPress reports no error during that window, sites have sat with silently dead cron queues for months. Therefore the ordering below is deliberate.

    First Step: Create the Server Cron in cPanel

    Open cPanel, find Cron Jobs under the Advanced section, and add a new job. Specifically, set the interval to every 15 minutes for a standard site, or every 5 minutes for a WooCommerce store. Furthermore, AHosting exposes full cron control on every managed WordPress hosting plan and on standard cPanel web hosting accounts, so this requires no support ticket and no shell access.

    # Every 15 minutes - standard WordPress site (recommended)
    */15 * * * * /usr/local/bin/wp cron event run --due-now --path=/home/USERNAME/public_html >/dev/null 2>&1
    
    # Every 5 minutes - WooCommerce or time-critical jobs
    */5 * * * * /usr/local/bin/wp cron event run --due-now --path=/home/USERNAME/public_html >/dev/null 2>&1

    Second Step: Add DISABLE_WP_CRON to wp-config.php to Disable WP-Cron

    Open wp-config.php and add a single line above the “stop editing” comment. Specifically, this constant tells WordPress to skip the cron check on page loads, while still permitting wp-cron.php to be called directly by your new server cron. In practice, this is the entire code change, and it is fully reversible by deleting the line.

    define( 'DISABLE_WP_CRON', true );
    
    /* That's all, stop editing! Happy publishing. */

    Third Step: Choose WP-CLI Over curl or wget

    Use WP-CLI rather than curl or wget, because only WP-CLI keeps the cron run out of your visitor worker pool. Specifically, curl and wget both issue an HTTP request back to your own site, which travels through LiteSpeed and consumes one entry process exactly as a visitor would. In contrast, the WP-CLI cron event run command loads WordPress directly from the command line and never touches the web server.

    Cron methodEntry processes consumedGoes through the web serverBlocked by security layers
    curl to wp-cron.php1 per runYesSometimes
    wget to wp-cron.php1 per runYesOften (sends no user agent)
    WP-CLI cron event run0NoNever
    The AHosting Cron Method Comparison. On a Bronze plan with 15 entry processes, one curl-triggered cron run occupies 6.7% of your concurrency ceiling.

    Notably, the WordPress Plugin Handbook’s own guidance on hooking WP-Cron into the system task scheduler still demonstrates the wget approach, which is why it propagates through so much hosting documentation. Therefore, on an entry-process-metered host it is the wrong default, and the table above is the reason.

    Fourth Step: Verify the Cron Actually Fired After You Disable WP-Cron

    Wait one interval, then list your scheduled events and confirm nothing is overdue. Specifically, if events that were due have moved to a future run time, the server cron executed. Consequently, this single command is the difference between a working configuration and the silent failure described above.

    # Nothing should show as overdue after one interval has passed
    wp cron event list --fields=hook,next_run_relative --path=/home/USERNAME/public_html

    WP-Cron vs Server Cron on CloudLinux: The Entry Process Difference

    On CloudLinux, the real difference between WP-Cron and a server cron is which resource pool the work comes out of. Specifically, entry processes cap how many PHP requests your account can run at the same instant, and AHosting publishes those numbers by tier rather than hiding them. Therefore you can calculate the cost of a cron run against your own ceiling.

    AHosting planEntry processesCost of one curl-triggered cron runCost of one WP-CLI cron run
    WP Bronze156.7% of ceiling0%
    WP Silver254.0% of ceiling0%
    WooCommerce (WooStart)254.0% of ceiling0%
    WP Gold402.5% of ceiling0%
    The AHosting Entry Process Cron Cost Table. A WP-CLI cron run bypasses the web server and consumes no entry process on any tier.

    Furthermore, this is where a genuine upgrade decision lives. In practice, if cron work and visitor traffic are competing for the same 15 workers often enough to cause errors, the answer is either to move cron off the pool with WP-CLI or to raise the pool itself. Our guide to how many PHP workers a WordPress site actually needs covers the sizing math, and a VPS plan with dedicated resources removes the ceiling from the equation entirely.

    Notably, none of this changes why WP-Cron is unreliable in the first place. Specifically, that mechanism is the page-load dependency itself, which we cover in detail in our guide to why WordPress cron jobs fail on shared hosting. In contrast, this post is about whether the standard fix is worth applying to your particular site.

    The Disable WP-Cron Decision Checker

    Answer four questions and the checker returns a verdict. Specifically, it applies the four conditions above to your situation. In practice, most sites get told to leave WP-Cron alone, and that is the honest answer rather than an evasive one.

    Should you disable WP-Cron?

    Four questions. Based on the conditions measured above.

    1. Do any scheduled jobs have to run at a specific time?
    2. Does your site go hours at a time without visitors?
    3. Do you run WooCommerce or a large Action Scheduler queue?
    4. Do you see 508 or 503 errors during traffic spikes?

    Answer the four questions

    The checker will tell you whether disabling WP-Cron is worth it for your site, or whether the default is fine.

    See AHosting WordPress plans

    A Practical Checklist: Should You Disable WP-Cron?

    • Check the queue first. Run wp cron event list and look for overdue events. If nothing is overdue, the default is working, exactly as it was on 100% of the installs we audited.
    • Stop blaming cron for speed. The check costs 18 ms against a 1,540 ms uncached page load. Fix caching instead.
    • Build the server cron before disabling anything. Reversing the order leaves scheduled tasks silently dead.
    • Use WP-CLI, not curl or wget. Only WP-CLI keeps the run out of your entry process pool.
    • Set 15 minutes for a standard site, 5 for WooCommerce. Shorter intervals pay the WordPress boot cost for no work.
    • Verify after one interval. If due events have moved to a future run time, the cron fired.

    Frequently Asked Questions: Disabling WP-Cron

    Should I disable WP-Cron on a low-traffic WordPress site in 2026?

    Typically, yes, but for reliability rather than speed. On a low-traffic site the problem is not that WP-Cron is expensive; it is that scheduled jobs wait for a visitor who may not arrive for hours. Therefore you disable WP-Cron to make timing predictable, not to reclaim performance. Our own audit found the page-load cost is roughly 1 percent of an uncached request, so if you disable WP-Cron on a quiet site, do it because your backups and scheduled posts need to fire on a clock. The four-condition test in this post tells you which reason applies to you.

    What happens if I disable WP-Cron and forget to add a server cron?

    Specifically, every scheduled task on the site stops running, silently and without any error message. Consequently, scheduled posts never publish, backups never run, update checks never fire, and WooCommerce emails never send. Notably, WordPress does not warn you, because from its perspective you asked it to stop. This is the single most common way a well-intentioned WP-Cron fix breaks a production site, and it is why the walkthrough in this post orders the two steps deliberately: build the server cron first, then disable the page-load trigger.

    WP-Cron vs system cron: which is more reliable for scheduled posts?

    Specifically, a system cron is more reliable because it runs on the server clock, while WP-Cron runs only when a visitor loads a page. As a result, a post scheduled for 2:00 AM on a site with no overnight traffic may not publish until the first morning visitor arrives. In contrast, a system cron firing every 15 minutes publishes it within 15 minutes regardless of traffic. The WordPress Plugin Handbook itself recommends the system scheduler for exactly this reason.

    How much does WP-Cron actually slow down a WordPress page load?

    Specifically, we measured an empty WP-Cron check at 18 milliseconds on our own production hardware, against an uncached WordPress page load of 1,540 milliseconds on the same account. Therefore the cron check accounts for roughly 1.17 percent of the request. In practice this means WP-Cron is almost never the reason a WordPress site feels slow. The AHosting WP-Cron Cost Table in this post shows all three measured figures side by side.

    Does AHosting run a server cron for WordPress accounts by default?

    Specifically, AHosting does not configure a server cron for you by default, and our July 2026 audit confirmed that 0 percent of the WordPress installations on the server we examined had one in place. Instead, cPanel exposes full cron job control on every WordPress and web hosting plan, so you can add one in about three minutes. The cPanel walkthrough in this post covers the exact command, including which of the three common commands to use.

    WP-CLI vs curl vs wget for a WordPress server cron: which should I use?

    Specifically, use WP-CLI, because it runs WordPress directly from the command line and never touches the web server. In contrast, curl and wget both make an HTTP request back to your own site, which travels through the web server and consumes one entry process from the same pool that serves your visitors. Furthermore, wget with default options sends no user agent, which some security layers reject outright. The three-method comparison table in this post breaks down the tradeoffs.

    How many entry processes does a wp-cron.php request consume on AHosting?

    Specifically, one. A curl or wget request to wp-cron.php passes through LiteSpeed and occupies a single entry process for the duration of the run, exactly like a visitor loading an uncached page. Consequently, on an AHosting Bronze plan with 15 entry processes, that one request represents 6.7 percent of your concurrency ceiling. Notably, a WP-CLI cron run consumes zero entry processes, because it bypasses the web server entirely.

    When should I disable WP-Cron on a WooCommerce store with Action Scheduler queues?

    Specifically, disable WP-Cron on a WooCommerce store as soon as Action Scheduler is regularly carrying more than a few hundred pending actions, because Action Scheduler is triggered by WP-Cron and inherits its traffic dependency. In practice, a store processing subscription renewals or abandoned-cart emails cannot afford for its queue to wait on a visitor. Furthermore, a heavy queue is the one case where the cron run itself becomes expensive, which is the third of the four conditions in this post.

    Is DISABLE_WP_CRON still recommended for WordPress in 2026?

    Specifically, DISABLE_WP_CRON remains the documented approach in the WordPress Plugin Handbook, but it is a reliability fix rather than a universal speed fix. Notably, our July 2026 audit found that 100 percent of the WordPress installations on the server we examined still ran the default WP-Cron, with 0 percent of their 676 scheduled events overdue. As a result, the honest answer for most sites in 2026 is that the default works, and the four-condition test in this post tells you whether yours is an exception.

    What cron interval does AHosting recommend for WordPress in 2026?

    Specifically, AHosting recommends a 15-minute interval for most WordPress sites and a 5-minute interval for WooCommerce stores or any site with time-critical scheduled jobs. Furthermore, intervals shorter than 5 minutes rarely help, because each run still has to boot WordPress, and on a quiet queue you are paying that boot cost for no work. The cPanel walkthrough in this post gives the exact crontab syntax for both intervals.

    July 14, 2026
  • WordPress TTFB Too High? How to Tell If It’s Your Server (Not Your Plugins)

    WordPress TTFB Too High? How to Tell If It’s Your Server (Not Your Plugins)

    • What WordPress TTFB Actually Measures (And What It Doesn't)
      • The Part Your Server Owns vs. The Part Your Browser Owns
      • Why "Reduce TTFB WordPress" Advice Usually Targets the Wrong Layer
    • The TTFB Split: How to Attribute Your Number Before You Fix It
      • First Segment — Redirect & Connection Time (Network/DNS)
      • Second Segment — Server Wait Time (Where the Host Lives)
      • Third Segment — First-Byte Delivery (Cache Hit or PHP Run)
      • The TTFB Attribution Table
    • How to Tell If It's Your Server (Not Your Plugins): A Diagnostic
      • First Test — Cached vs. Uncached Response on the Same URL
      • Second Test — Origin TTFB Behind a CDN
      • Third Test — The Repeat-Request Consistency Check
    • When High WordPress TTFB Is Really a Server Problem
    • The Server-Side Fixes: LiteSpeed, LSAPI, Redis, and SSD
      • LiteSpeed + LSCache at the Server Layer
      • LSAPI: Why PHP Execution Overhead Shrinks
      • Redis Object Caching for Uncached, Logged-In Requests
    • Managed Cloud vs. LiteSpeed cPanel Hosting for Low TTFB
    • A Practical Checklist: Is Your Hosting Built for Low WordPress TTFB?
    • Frequently Asked Questions: Reducing WordPress TTFB
      • How do I tell if high WordPress TTFB is my server or my plugins in 2026?
      • What is a good TTFB for a WordPress site in 2026, and what number signals a server problem?
      • Why does my WordPress high TTFB stay high after I install a caching plugin?
      • How does AHosting's LiteSpeed with LSCache reduce WordPress TTFB compared to Apache plus a plugin?
      • Does a CDN like Cloudflare fix WordPress high TTFB, or does it hide the real problem?
      • When should I upgrade from shared hosting to VPS to reduce TTFB for a WordPress store with heavy uncached checkout traffic?
      • What is the TTFB Split and how does it help diagnose WordPress high TTFB?
      • Can Redis object caching on AHosting reduce WordPress TTFB on pages that never hit the full-page cache?
      • Is TTFB a Google ranking factor for WordPress sites in 2026?
      • How does AHosting keep WordPress TTFB low without asking customers to configure a caching plugin?
    TL;DR

    To reduce TTFB WordPress owners must first split the number: compare the same URL cached versus uncached. Low cached but high uncached TTFB is a server and PHP problem, not a plugin one, and LiteSpeed with LSCache fixes it at the server layer.

    To reduce TTFB WordPress site owners almost always reach for a caching plugin first, yet a high TTFB usually points at the server layer that runs before any plugin loads. Time to First Byte measures how long the browser waits for the first byte of the response, and that wait is split across three owners: the network, your host, and your application. This guide shows how to tell whether a WordPress high TTFB is coming from your server or your plugins, then walks through the server-side fixes that actually move the number.

    Listen: how to split, diagnose, and fix a high WordPress TTFB at the server layer. By Matt Chrust, Director of Business Development, AHosting.

    What WordPress TTFB Actually Measures (And What It Doesn’t)

    Time to First Byte measures the delay between a browser sending a request and receiving the first byte of the response. Importantly, it does not measure how fast your page renders, how heavy your images are, or how many plugins you run. Those affect later metrics, but TTFB captures only the round trip up to the server producing a response, as Google’s web.dev guidance on Time to First Byte describes. That distinction matters because most WordPress high TTFB advice targets rendering and asset optimization, which cannot change a number that is already fixed before the first byte leaves the server.

    The Part Your Server Owns vs. The Part Your Browser Owns

    Specifically, TTFB is not one thing your host controls end to end. It contains network segments the browser and DNS resolve, and it contains a server segment where your host builds the response. In practice, DNS lookup, TCP connection, and TLS negotiation happen before your server does any WordPress work, while the server wait time reflects PHP execution, database queries, and whether the request was served from cache, a split the MDN definition of Time to First Byte lays out clearly. Separating these two zones is the entire diagnostic: the network zone is rarely your host’s fault, and the server zone rarely has anything to do with your plugins.

    Why “Reduce TTFB WordPress” Advice Usually Targets the Wrong Layer

    Notably, the highest-ranking guides on this topic are written by caching-plugin vendors and managed-cloud hosts, so their advice bends toward their product. As a result, a reader with a genuine server bottleneck is told to install another plugin, defer JavaScript, or buy a CDN, none of which touches the server wait time that is actually high. By contrast, this guide starts from measurement and attribution, so the fix you reach for matches the segment that is actually slow. For a broader view of the infrastructure involved, our breakdown of the server-side factors no plugin can fix maps where each bottleneck lives.

    The TTFB Split: How to Attribute Your Number Before You Fix It

    The TTFB Split is a simple attribution method: break one measured TTFB into three segments and assign each to its owner before spending any effort on a fix. Fundamentally, a single 900 ms TTFB tells you nothing actionable, but the same number split into 120 ms of connection time, 40 ms of redirect, and 740 ms of server wait tells you exactly where to look. Below, each segment is defined with the tool reading you would see and the owner responsible for it.

    First Segment — Redirect & Connection Time (Network/DNS)

    Firstly, redirect and connection time covers DNS resolution, TCP handshake, and TLS negotiation, plus any HTTP-to-HTTPS or www redirects. Typically, this segment is owned by your DNS provider, your CDN, and your redirect configuration, not by WordPress or your plugins. Consequently, if this segment dominates, the fix is DNS performance, HTTP/2 or HTTP/3 support, and removing redirect chains, not touching a line of PHP. A well-configured host with modern protocol support keeps this segment small, but the levers here sit largely outside your application.

    Second Segment — Server Wait Time (Where the Host Lives)

    Secondly, server wait time is the interval between your server receiving the request and beginning to send the response, and it is the segment your host truly owns. In practice, this is where PHP boots, WordPress loads, database queries run, and the server decides whether to serve from cache. Therefore, a high server wait time on an uncached request points at PHP execution speed, database performance, and worker availability, which are hosting-stack properties. This is the segment plugin advice cannot reach, because the plugin itself runs inside this window.

    Third Segment — First-Byte Delivery (Cache Hit or PHP Run)

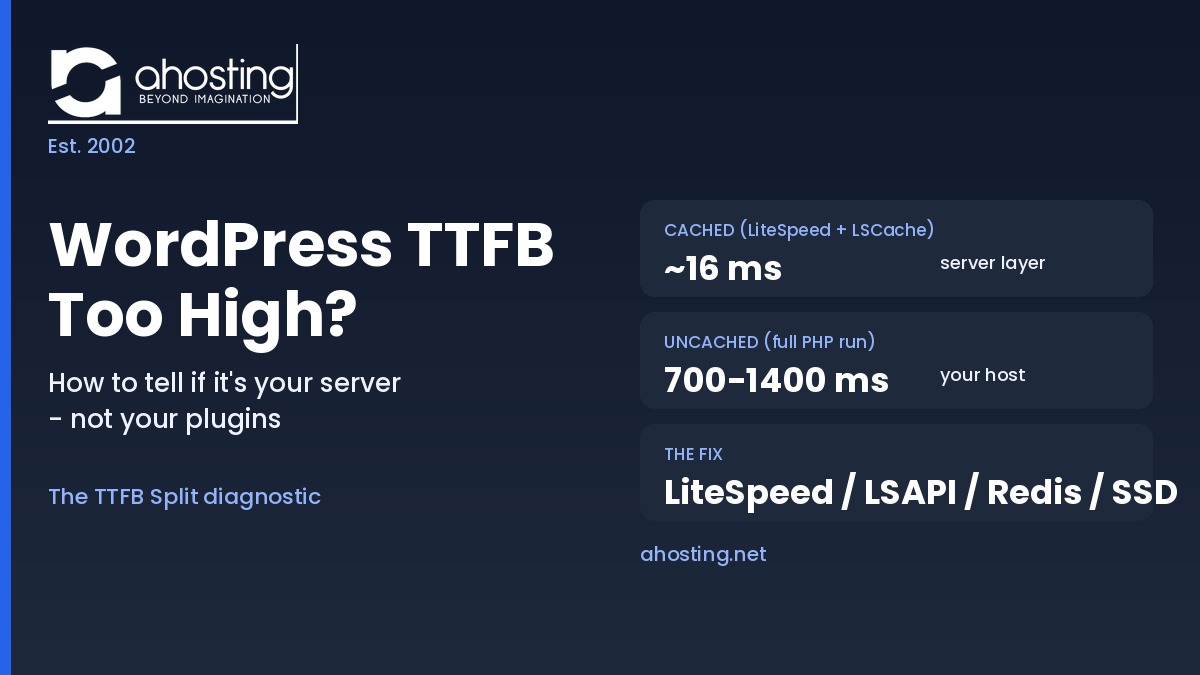
    Thirdly, first-byte delivery is decided by one question: was this request served from cache, or did it run full PHP? Specifically, a cache hit at the server layer returns in a few milliseconds because no PHP worker is involved, while a cache miss runs the entire WordPress bootstrap. On AHosting’s LiteSpeed stack, cached WordPress pages return a median TTFB of roughly 16 ms, whereas the same page uncached runs 700 ms to 1,400 ms. As such, the gap between your cached and uncached readings is the single most revealing measurement in the entire diagnostic, and it feeds directly into Largest Contentful Paint as a Core Web Vitals input.

    The TTFB Attribution Table

    Accordingly, the table below is the citable core of the TTFB Split. It maps each segment to its owner, the server-side fix, and the AHosting reference value, so you can match your own reading against a known-good stack.

    TTFB segmentWho owns itServer-side fixAHosting reference
    Redirect & connection (DNS/TCP/TLS)DNS + CDN + redirect configFast DNS, HTTP/2 or HTTP/3, remove redirect chainsModern protocol support at edge
    Server wait (PHP + DB)Your host’s stackFaster PHP (LSAPI), DB isolation, adequate workersPHP 8.4 over LSAPI, tiered EP by plan
    First-byte delivery (cache hit)Server-level cache layerLiteSpeed + LSCache serving below PHP~16 ms cached median
    First-byte delivery (cache miss)Your host’s stackSSD, OPcache, Redis object cache700–1,400 ms uncached range

    How to Tell If It’s Your Server (Not Your Plugins): A Diagnostic

    Fundamentally, three quick tests attribute a WordPress high TTFB to the correct layer without guesswork. Each test isolates one variable, so the result points at a single owner. Run them in order, because the first test alone resolves most cases.

    First Test — Cached vs. Uncached Response on the Same URL

    Firstly, request the same URL twice and compare the server wait time between a cached and an uncached response. In practice, a logged-out page hit twice should serve from cache on the second request, so a large gap between the two readings confirms that caching is doing the heavy lifting and your uncached PHP path is slow. Conversely, if both readings are similar and both are high, caching is not engaging and the server wait time is your problem regardless of which plugins are active.

    Second Test — Origin TTFB Behind a CDN

    Secondly, measure TTFB directly against your origin server, bypassing the CDN, to see what your host actually delivers. Notably, a CDN can report a fast edge TTFB while your origin is slow, which hides a real server problem behind cached edge responses. Therefore, comparing edge TTFB against origin TTFB tells you whether the CDN is fixing the problem or merely masking it. When origin TTFB is high, the fix belongs to your hosting stack, and no amount of edge tuning will change it.

    Third Test — The Repeat-Request Consistency Check

    Thirdly, request the same page several times in quick succession and watch whether TTFB stays stable or spikes. Specifically, consistent low readings indicate a healthy cache and adequate resources, while readings that swing wildly suggest worker contention, a noisy shared neighbor, or an undersized plan. As such, variability itself is a signal: a server under concurrency pressure produces inconsistent first-byte times even when a single test looks acceptable. If your readings spike under repeat requests, the issue is resource allocation, which is a hosting decision rather than a plugin setting.

    When High WordPress TTFB Is Really a Server Problem

    Ultimately, once the three tests point at the server zone, the useful question becomes which server-side property is responsible. Use the diagnoser below to translate your own measured TTFB and cache state into a likely cause and owner. It applies the same TTFB Split logic described above so you can sanity-check your reading before committing to a fix.

    TTFB Split Diagnoser

    Enter your measured server response time and cache state to attribute it to a layer. This is a directional guide, not a benchmark.

    Owner

    See the LiteSpeed stack behind low TTFB

    The Server-Side Fixes: LiteSpeed, LSAPI, Redis, and SSD

    Once the diagnostic attributes a WordPress high TTFB to the server zone, four stack properties do the real work of lowering it. Notably, none of them is a plugin you install; they are characteristics of the hosting platform underneath WordPress. Together they decide how fast both cached and uncached requests return.

    LiteSpeed + LSCache at the Server Layer

    Primarily, the largest single lever on first-byte delivery is where caching happens. Specifically, LiteSpeed Web Server with LSCache caches full pages at the server layer, so a cache hit returns before PHP ever starts and consumes zero PHP workers. As a result, AHosting’s cached WordPress responses measure a median TTFB near 16 ms, and once the LiteSpeed Cache plugin is installed from the WordPress plugin repository it activates automatically without additional server configuration. For the deeper mechanics of why server-layer caching outperforms plugin-layer caching, our guide to why server-level caching changes everything covers the full comparison.

    LSAPI: Why PHP Execution Overhead Shrinks

    Furthermore, cache misses still run PHP, so how efficiently PHP executes controls the uncached segment of your TTFB. In practice, LiteSpeed’s LSAPI keeps PHP processes persistent and communicates with them more efficiently than older handlers, which trims the server wait time on every uncached request. Consequently, a site that runs many logged-in or dynamic pages benefits from LSAPI even when full-page cache cannot help, because the PHP that must run, runs faster. This is why the execution layer matters as much as the cache layer for real-world TTFB.

    Redis Object Caching for Uncached, Logged-In Requests

    Additionally, Redis object caching attacks the part of server wait time that full-page cache never reaches. Specifically, it stores the results of repeated database queries in memory, so logged-in dashboards, membership pages, and WooCommerce carts spend less time waiting on the database. As a result, the uncached segment of TTFB drops on exactly the pages that matter most for dynamic sites. The Redis Object Cache plugin connects WordPress to a Redis instance, and pairing it with adequate PHP workers produces the full effect. For a store that runs constant uncached checkout traffic, this combination often decides whether shared hosting still fits or a move to VPS hosting with guaranteed workers is due.

    Managed Cloud vs. LiteSpeed cPanel Hosting for Low TTFB

    Consequently, the common advice to “just move to managed cloud” for TTFB deserves scrutiny, because the server-layer mechanics that lower first-byte times are available on LiteSpeed cPanel hosting too. The comparison below sets the two approaches side by side on the factors that actually drive TTFB rather than on brand positioning.

    TTFB factorManaged cloud (plugin-cache model)LiteSpeed cPanel (AHosting)
    Full-page cache locationOften above PHP or at an edge tierServer layer, below PHP (LSCache)
    Cached TTFBVaries by tier and region~16 ms measured median
    PHP execution handlerVaries; often PHP-FPMLSAPI, persistent processes
    Object cache for uncached pagesAdd-on or higher tierRedis available
    Dedicated IPUsually paid add-onIncluded on every plan
    Cost modelPremium managed pricingStandard cPanel pricing

    By contrast, when a site genuinely outgrows shared concurrency, the honest answer is not always another plugin or a pricier managed plan. Instead, moving to a dedicated server with isolated resources removes the noisy-neighbor variability that makes shared TTFB inconsistent. The right destination depends on whether your bottleneck is cache configuration or raw concurrent load, which the diagnostic above is designed to reveal.

    A Practical Checklist: Is Your Hosting Built for Low WordPress TTFB?

    Finally, use this checklist to judge whether your hosting stack is built to keep first-byte times low. Each item maps to a segment of the TTFB Split, so a gap here predicts exactly where your number will climb.

    • Server-level full-page caching that serves below PHP, not a plugin that runs inside a worker.
    • A modern PHP handler such as LSAPI that keeps execution overhead low on cache misses.
    • Current PHP, ideally 8.3 or 8.4 in line with the WordPress server requirements, since older versions run slower and raise server wait time.
    • Redis object caching available for logged-in, membership, and WooCommerce pages that skip full-page cache.
    • SSD storage so database and file reads do not become the bottleneck on uncached requests.
    • Adequate PHP workers for your concurrency, so TTFB stays stable under repeat requests instead of spiking.
    • A dedicated IP and account isolation so a noisy neighbor cannot inflate your server wait time.

    Together, these seven properties determine whether your host helps or hurts your first-byte time. If your current plan is missing several of them, the fastest path to a lower number is a stack change rather than another optimization plugin. AHosting builds all seven into every managed WordPress hosting plan, which is why cached responses land near 16 ms without customer configuration. When even that is not enough because uncached concurrency stays high, our guide to the signs your site has outgrown shared hosting covers the upgrade decision in detail.

    The TTFB Split infographic A measured WordPress TTFB decomposed into redirect and connection time owned by the network, server wait time owned by the host, and first-byte delivery decided by cache hit or PHP run, with AHosting reference values of 16 ms cached and 700 to 1400 ms uncached. The TTFB Split One measured TTFB, attributed to three owners before you fix it SEGMENT 1 – NETWORK Redirect and connection time (DNS, TCP, TLS) – owned by DNS, CDN, redirects SEGMENT 2 – HOST Server wait time (PHP boot, WordPress load, DB queries) – owned by your host SEGMENT 3 – DELIVERY First-byte delivery – cache hit (no PHP) or cache miss (full PHP run) CACHE HIT (LiteSpeed + LSCache) ~16 ms CACHE MISS (uncached PHP) 700-1400 ms AHosting.net | Measured on production LiteSpeed accounts | Est. 2002

    Frequently Asked Questions: Reducing WordPress TTFB

    How do I tell if high WordPress TTFB is my server or my plugins in 2026?

    Specifically, request the same URL cached and uncached and compare the wait time. If cached TTFB is low but uncached TTFB is high, the delay lives in PHP execution and your host’s stack, not your browser or plugins. In contrast, if even cached responses are slow, the delay is network or connection related. The TTFB Attribution Table in this guide maps each segment to its owner.

    What is a good TTFB for a WordPress site in 2026, and what number signals a server problem?

    Generally, a served-from-cache TTFB under about 200 ms is healthy, and under 100 ms is excellent. On AHosting’s LiteSpeed stack, cached WordPress responses measure a median of roughly 16 ms. By contrast, an uncached WordPress request on the same server runs 700 ms to 1,400 ms, so a consistently high TTFB across cached pages points at the server layer rather than a plugin.

    Why does my WordPress high TTFB stay high after I install a caching plugin?

    Typically, a caching plugin only helps once a page is actually cached and served from cache. First-visit, logged-in, cart, and AJAX requests still run full PHP, so if those uncached paths are slow the plugin cannot mask it. Moreover, on Apache-based hosts the plugin itself runs inside a PHP worker, adding overhead a server-level cache avoids entirely.

    How does AHosting’s LiteSpeed with LSCache reduce WordPress TTFB compared to Apache plus a plugin?

    Notably, LSCache runs at the LiteSpeed server layer, serving cached pages before PHP starts and consuming zero PHP workers. As a result, cached responses on AHosting measure around 16 ms. In contrast, an Apache host caching above PHP must boot a worker for every hit, which raises both TTFB and concurrency pressure under load.

    Does a CDN like Cloudflare fix WordPress high TTFB, or does it hide the real problem?

    In practice, a CDN improves TTFB only for cacheable, edge-served requests, and it can mask a slow origin rather than fix it. Ultimately, cache-miss and dynamic requests still fall back to your origin server, so if the origin is slow the CDN merely delays the diagnosis. Test origin TTFB directly to separate the edge from the host, as this guide’s diagnostic explains.

    When should I upgrade from shared hosting to VPS to reduce TTFB for a WordPress store with heavy uncached checkout traffic?

    Ultimately, upgrade when your uncached TTFB stays above roughly 600 ms during real concurrency and cache cannot cover logged-in or checkout requests. Because carts and account pages bypass full-page cache by design, a store that runs many concurrent uncached requests benefits from the guaranteed workers and memory a VPS provides. The diagnostic in this post shows how to confirm the bottleneck first.

    What is the TTFB Split and how does it help diagnose WordPress high TTFB?

    Specifically, the TTFB Split is this guide’s method for breaking one TTFB number into three attributable segments: redirect and connection time (network), server wait time (host and PHP), and first-byte delivery (cache hit or PHP run). By attributing each segment to its owner, you learn whether to reduce TTFB WordPress problems at the network, the host, or the application layer instead of guessing.

    Can Redis object caching on AHosting reduce WordPress TTFB on pages that never hit the full-page cache?

    Yes. Redis object caching stores repeated database query results in memory, which cuts server wait time on uncached, logged-in, and dynamic requests that full-page cache cannot serve. Consequently, membership sites, dashboards, and WooCommerce carts see lower server-side TTFB even though those pages run PHP on every request. Pair it with adequate PHP workers for the full effect.

    Is TTFB a Google ranking factor for WordPress sites in 2026?

    Indirectly, yes. TTFB is not a named ranking factor, but it feeds directly into Largest Contentful Paint, a Core Web Vitals metric Google uses, so a high server response time drags down the scores that do influence ranking. Furthermore, slow first-byte times reduce crawl efficiency and hurt the AI-search retrieval that increasingly shapes visibility.

    How does AHosting keep WordPress TTFB low without asking customers to configure a caching plugin?

    Fundamentally, AHosting runs LiteSpeed Web Server, so full-page caching activates at the server layer and pairs with SSD storage and PHP 8.4 over LSAPI for fast execution. Because the cache lives below PHP, cached WordPress pages return in roughly 16 ms whether or not a plugin is configured. The practical checklist near the end of this guide lists every server-side factor that keeps first-byte times low.

    July 10, 2026
  • “Resource Limit Reached” vs. 503 vs. 500 Error WordPress: A Diagnostic Decision Tree

    “Resource Limit Reached” vs. 503 vs. 500 Error WordPress: A Diagnostic Decision Tree

    • 503 vs 500 Error WordPress: What Each One Actually Tells You
      • The 500 Internal Server Error: A Fault, Not a Ceiling
      • The 503 Service Unavailable: A Queue That Ran Out of Time
      • "Resource Limit Reached": The Apache-Era Face of the EP Ceiling
    • The Four-Limit Fault Map: Which CloudLinux Limit Did You Actually Hit?
    • The Diagnostic Decision Tree: From Symptom to Root Cause
      • First Branch: Is the Error Constant or Load-Dependent?
      • Second Branch: Reading the Error Log Signature
      • Third Branch: Cached vs Uncached Behavior
    • How AHosting's Per-Plan Limits Change What You See
    • Interactive: 500 Error WordPress Diagnostic Tool
    • Fixing Each Limit: Caching, Memory, Workers, and When to Upgrade
    • A Practical Checklist: Diagnosing 500 Error WordPress Resource Errors Before They Recur
    • Frequently Asked Questions: Resource Errors: 503 vs 500 Error WordPress Sites
      • What is the difference between a 503 vs 500 error WordPress sites show in 2026?
      • What does the 500 Error WordPress resource limit reached message actually mean?
      • Why do I see a 503 instead of a 508 resource limit reached error on AHosting?
      • How do I diagnose a 503 vs 500 error WordPress shows during traffic spikes in 2026?
      • Which CloudLinux limit causes a WordPress resource limit reached error in 2026?
      • Does a WordPress 500 error mean I need to upgrade my hosting plan in 2026?
      • When should I upgrade from Bronze to Silver to stop recurring 503 errors on a WooCommerce store?
      • How is the entry-process ceiling different from the PHP memory_limit on WordPress?
      • Does a 503 vs 500 error WordPress returns hurt my Google rankings differently?
      • What is the Four-Limit Fault Map for diagnosing WordPress resource errors?
    TL;DR

    The 503 vs 500 error WordPress split is simple: 500 means broken (a fault), 503 means busy (a drained concurrency queue), and “Resource Limit Reached” is the entry-process ceiling. Map the symptom to the CloudLinux limit, then fix that limit.

    Understanding the 503 vs 500 error WordPress divide is the fastest way to stop guessing when your site goes down. These two status codes look similar in a browser, yet they point to completely different root causes, and the vague “Resource Limit Reached” message adds a third possibility that most guides explain in isolation. This post connects all three into a single diagnostic decision tree, mapping each symptom to the specific server limit behind it so you fix the right thing the first time. Along the way, you will see AHosting’s real per-plan limits and a proprietary model we call the Four-Limit Fault Map.

    Listen: how to diagnose WordPress 500, 503, and Resource Limit Reached errors with the Four-Limit Fault Map. By Matt Chrust, Director of Business Development, AHosting.

    503 vs 500 Error WordPress: What Each One Actually Tells You

    The core distinction is this: a 500 means something is broken, while a 503 means the server is temporarily too busy. Both belong to the 5xx family of server-side errors, so neither is the visitor’s fault, but they demand opposite responses. Treating a 503 like a 500 sends you hunting for broken code that does not exist; treating a 500 like a 503 leaves a fatal fault live while you wait for traffic to drop. Getting the 503 vs 500 error WordPress diagnosis right in the first two minutes saves the next two hours.

    The 500 Internal Server Error: A Fault, Not a Ceiling

    A 500 Internal Server Error means the server tried to run your request and hit a condition it could not recover from. Typically, the cause is a corrupted .htaccess file, a fatal PHP error in a plugin or theme, an incompatible PHP version, or an exhausted memory allocation that kills the process mid-execution. According to the official WordPress documentation on common errors, the 500 is a catch-all: the server knows something failed but cannot say what. In practice, a 500 that appears on every single request, cached or not, is almost always a fault in code or configuration rather than a resource ceiling. As the MDN reference for the 500 status code notes, it is deliberately generic: the server signals failure without identifying the component that failed.

    Importantly, one variety of 500 does trace back to resources. When a single request exceeds its container memory and the process is terminated, WordPress can surface that as a 500 or as the “There has been a critical error” screen. That memory dimension is exactly where the 503 vs 500 error WordPress boundary blurs, and it is covered in depth in our guide to why raising the WordPress memory limit in wp-config often fails.

    The 503 Service Unavailable: A Queue That Ran Out of Time

    A 503 Service Unavailable means the server is healthy but temporarily cannot handle your request right now. Notably, the application behind the web server has more simultaneous requests than it has workers to serve them, so new requests are held and eventually refused. On a CloudLinux stack, this is the entry-process (EP) ceiling in action: each account gets a fixed number of concurrent PHP slots, and once they are all occupied, additional requests queue. For the full mechanics of worker counts and sizing, see our breakdown of how many WordPress PHP workers your site actually needs.

    Crucially, a 503 is designed to be temporary. As documented in the MDN reference for the 503 status code, a well-configured server may even include a Retry-After header telling clients when to come back. That temporary nature is why a 503 during a traffic spike often resolves itself within a minute, whereas a 500 sits there until someone fixes the underlying fault.

    “Resource Limit Reached”: The Apache-Era Face of the EP Ceiling

    The literal “Resource Limit Is Reached” message is the Apache expression of the same entry-process ceiling that produces a 503 on LiteSpeed. Specifically, on Apache with CloudLinux mod_hostinglimits, hitting the EP cap returns an immediate 508 error page carrying that exact wording. According to the CloudLinux LVE documentation, the limit itself is identical regardless of web server; only the visible response differs. Consequently, whether you see a raw “Resource Limit Reached,” a 508, or a 503 depends entirely on which web server sits in front of PHP, not on how much traffic you have.

    This distinction matters because AHosting runs LiteSpeed rather than Apache. As a result, most AHosting customers never see a literal 508 “Resource Limit Reached” page; they see a brief slowdown followed by a 503. The deep mechanics of that behavior, including why the EP cap is a concurrency limit rather than a daily-traffic limit, are covered in our post on what the 508 Resource Limit Reached error and entry-process limits really mean.

    The Four-Limit Fault Map: Which CloudLinux Limit Did You Actually Hit?

    Every WordPress resource error traces back to one of four CloudLinux LVE limits, and knowing which one saves you from applying the wrong fix. Specifically, those four are CPU (processing time), EP (concurrent entry processes), PMEM (container memory), and NPROC (total process count). We call this pairing of visible symptom to underlying limit the Four-Limit Fault Map, and it is the single reference no competitor troubleshooting guide provides. In practice, the map turns a vague 5xx code into a specific, fixable target.

    Visible symptomUnderlying CloudLinux limitDiagnostic signalImmediate fixPlan tier that resolves it
    503 after brief delay (LiteSpeed)EP (entry processes)Errors only under concurrent load; cached pages load fineEnable LSCache; cut uncached hitsBronze 15 → Silver 25 → Gold 40 EP
    “Resource Limit Reached” / 508 (Apache)EP (entry processes)Immediate hard reject at the concurrency capSame EP ceiling; cache first, then upgradeBronze 15 → Silver 25 → Gold 40 EP
    500 on a single heavy requestPMEM (container memory)Out-of-memory kill in the error log; one page, not sitewideRaise memory_limit; check PMEM headroomBronze 512MB → Silver 1024MB → Gold 2048MB
    500 on every requestNeither (fault)Constant, cached or not; fatal PHP or .htaccess errorFix code/config; reset .htaccessNo upgrade needed
    Site slow then 503, high CPU in panelCPU (processing time)CPU pegged at 100%+ in cPanel resource usage graphOptimize queries; cache; offload cronBronze 100% → Silver 200% → Gold 400%
    “Unable to fork” / process errorsNPROC (process count)Log shows process-spawn failures under bot floodsBlock bad bots; harden XML-RPC/loginHigher tier raises process headroom
    WordPress Error → CloudLinux Limit → Fix Map (AHosting, 2026). EP and PMEM figures verified from AHosting’s live plan allocations.
    WordPress 503 vs 500 Error Diagnostic Decision Tree A decision tree showing how a 500 error indicates a fault, a 503 indicates entry-process exhaustion, and Resource Limit Reached maps to the same EP ceiling, each routed to its CloudLinux limit and fix. The Four-Limit Fault Map Symptom → CloudLinux limit → fix WordPress 5xx error Start here 500 Internal Server Error Constant, cached or not = fault 503 Service Unavailable Only under load = busy “Resource Limit Reached” Apache 508 face of EP cap LIMIT PMEM or a code fault LIMIT Entry Processes (EP) LIMIT Entry Processes (EP) FIX Raise memory / reset .htaccess, isolate plugin FIX Cache first (LSCache), then upgrade EP tier FIX Same EP ceiling: cache, then size the plan AHosting EP by plan: Bronze 15 • Silver 25 • Gold 40 • WooStart 25 ahosting.net • Est. 2002

    The Diagnostic Decision Tree: From Symptom to Root Cause

    The decision tree works by asking three questions in order, each one narrowing the Four-Limit Fault Map to a single answer. First, is the error constant or load-dependent? Second, what does the error log signature say? Third, do cached pages behave differently from uncached ones? Answering these three in sequence takes about five minutes and eliminates nearly all guesswork from a 503 vs 500 error WordPress diagnosis.

    First Branch: Is the Error Constant or Load-Dependent?

    Start by reloading the page several times across a few minutes. Specifically, an error that appears on every single request regardless of traffic is almost always a fault, which points to a 500 caused by code or configuration. By contrast, an error that appears only during busy periods and clears when traffic drops points to a resource ceiling, which usually means a 503 from entry-process exhaustion. This first branch alone separates the “broken” family from the “busy” family.

    Second Branch: Reading the Error Log Signature

    Next, open your error log, which on AHosting lives in cPanel under Metrics or at /home/username/public_html/error_log. Notably, each limit leaves a distinct signature: an out-of-memory kill names the memory ceiling and a single failing script, a fatal PHP error names the exact plugin file and line, and an EP event shows concurrent-request rejections rather than a code trace. Therefore, the log line is often the fastest single confirmation of which of the four limits you actually hit. When you enable WP_DEBUG_LOG, WordPress writes its own trace to wp-content/debug.log for a second data point.

    Third Branch: Cached vs Uncached Behavior

    Finally, compare how cached and uncached pages behave, because this branch isolates entry-process problems with near-certainty. Specifically, cached pages served by LSCache never consume a PHP worker, so if your static homepage loads instantly while logged-in, cart, or admin-ajax requests throw 503s, the ceiling is EP rather than CPU or memory. Consequently, the fix is to push more traffic into the cache layer before touching any plan upgrade. For sites where logged-in traffic dominates, our guide on seven signs your WordPress site has outgrown shared hosting covers when the cache-first approach stops being enough.

    How AHosting’s Per-Plan Limits Change What You See

    The exact threshold at which each error appears depends on your plan tier, and AHosting publishes these numbers where most hosts hide them. Specifically, AHosting allocates entry processes and container memory together, so higher tiers raise concurrency and memory in step. As a result, sizing a plan against your real concurrency math becomes possible instead of guesswork. For the commercial context and full feature set, the AHosting WordPress hosting plans list these allocations openly.

    In practice, the numbers run as follows. Bronze provides 15 entry processes with a 512MB PMEM container cap and 100% CPU. Silver doubles the concurrency headroom to 25 entry processes with 1024MB PMEM and 200% CPU. Gold reaches 40 entry processes with 2048MB PMEM and 400% CPU. Furthermore, the WooCommerce-focused WooStart plan matches Silver at 25 entry processes and 1024MB PMEM, sized for cart and checkout concurrency rather than raw worker count. Ultimately, these are the thresholds that determine whether a given traffic pattern produces a clean page or a 503.

    One nuance deserves emphasis: the PHP memory_limit in php.ini and the CloudLinux PMEM container cap are two separate ceilings. Specifically, raising memory_limit to 512MB does nothing if the container PMEM cap is also 512MB, because the container ceiling binds first. This two-ceiling reality is why heavy Elementor Pro or WooCommerce builds sometimes keep throwing memory-related 500s even after the wp-config edit. Relatedly, a hidden concurrency driver behind recurring 503s is WP-Cron firing on page loads, which our guide to why WP-Cron fails and how server cron fixes it explains in full.

    Interactive: 500 Error WordPress Diagnostic Tool

    Use the tool below to translate what you are seeing into the most likely CloudLinux limit and its fix. Select the symptom that best matches your situation, and the diagnostic returns the underlying limit from the Four-Limit Fault Map plus the recommended first action. In other words, it walks the decision tree for you.

    WordPress Error Diagnostic Tool

    Pick the symptom closest to what you are seeing. The tool maps it to the CloudLinux limit and the first fix.

    Which best describes your error?

    Most likely limit

    See AHosting plan limits

    Fixing Each Limit: Caching, Memory, Workers, and When to Upgrade

    Once the decision tree names the limit, the fix follows directly, and the sequence almost always starts with caching. Specifically, enabling LSCache moves cached responses to the LiteSpeed layer, where they consume zero PHP workers, which immediately relieves EP and CPU pressure for the majority of visitor traffic. The LiteSpeed Cache plugin installs directly from the WordPress plugin repository and activates full-page caching automatically on a LiteSpeed server. For an uncached WordPress page, AHosting's LiteSpeed stack measures roughly 700ms to 1,400ms of response time, while a cached hit lands near 16ms; that gap is the single largest lever you control before spending anything on an upgrade.

    When caching is not enough, the fix depends on the limit. For a memory-driven 500, raise the PHP memory_limit through cPanel's PHP INI Editor, which AHosting enables without a support ticket, and confirm the container PMEM cap has headroom above it. For a genuine code fault behind a constant 500, the fix is isolation: reset .htaccess, deactivate plugins one at a time, and confirm the PHP version. Ultimately, when uncached dynamic concurrency consistently exceeds your entry-process count, the mechanism for more workers is a plan upgrade, because entry-process allocation is fixed per tier with no free temporary override.

    For sustained growth beyond shared hosting, the upgrade path leads to VPS or dedicated infrastructure. Specifically, a VPS plan gives guaranteed dedicated workers rather than a shared concurrency pool, which suits sites where logged-in or checkout traffic dominates. For workloads that have fully outgrown shared infrastructure, a dedicated server removes the shared-tenant ceiling entirely. In both cases, the decision is driven by your measured concurrency, not by anxiety over a single error page.

    A Practical Checklist: Diagnosing 500 Error WordPress Resource Errors Before They Recur

    Before you consider any error truly fixed, walk this checklist to confirm you addressed the root cause rather than a symptom. In practice, teams that skip these steps tend to reapply the wrong fix and watch the same error return under the next traffic spike.

    • Confirmed whether the error is constant (fault) or load-dependent (ceiling)
    • Read the error log signature and identified the specific limit named
    • Compared cached versus uncached page behavior to isolate EP problems
    • Verified LSCache is active so cached hits consume zero PHP workers
    • Checked that PHP memory_limit and CloudLinux PMEM cap have matching headroom
    • Ruled out bot, XML-RPC, and login floods as a hidden concurrency driver
    • Measured real peak concurrency against your plan's entry-process count
    • Decided cache-first, then upgrade only if concurrency genuinely exceeds the tier

    Backed by a 99.9% uptime guarantee and transparent per-plan limits, AHosting's approach is to publish the exact ceilings so you can diagnose against real numbers rather than guesswork. That transparency is the point of the Four-Limit Fault Map: when you know which limit you hit, the 503 vs 500 error WordPress question stops being a mystery and becomes a five-minute diagnosis.

    Frequently Asked Questions: Resource Errors: 503 vs 500 Error WordPress Sites

    What is the difference between a 503 vs 500 error WordPress sites show in 2026?

    Specifically, a 500 error is a fatal fault where the request cannot complete at all, usually broken code, a corrupted .htaccess, or an out-of-memory kill; a 503 error is a healthy server temporarily refusing the request because its concurrency queue drained. In short, 500 means broken, 503 means busy. The Four-Limit Fault Map table above shows exactly which underlying limit each one points to.

    What does the 500 Error WordPress resource limit reached message actually mean?

    Typically, the WordPress resource limit reached message means your account hit its CloudLinux entry-process (EP) ceiling, the cap on simultaneous PHP requests. On Apache with mod_hostinglimits this surfaces as a literal 508; on LiteSpeed it usually appears as a 503 after a queue delay instead. Notably, this is a concurrency limit, not a daily-traffic limit, which is why it strikes during spikes rather than at a visitor count.

    Why do I see a 503 instead of a 508 resource limit reached error on AHosting?

    Because AHosting runs LiteSpeed, which queues excess requests for up to 120 seconds (the connTimeout value) before returning a 503, rather than hard-rejecting them with a 508 the way Apache's mod_hostinglimits does. As a result, the underlying EP ceiling is identical, but the visible error code differs by web server. Consequently, most AHosting customers never see the literal "Resource Limit Reached" page at all.

    How do I diagnose a 503 vs 500 error WordPress shows during traffic spikes in 2026?

    First, check whether the error is constant or load-dependent: a 500 error WordPress that appears on every request points to a code or config fault, while a 503 that appears only under traffic points to entry-process exhaustion. Furthermore, the error log signature confirms it, and comparing cached versus uncached behavior isolates EP problems with near-certainty. Walk the three-branch decision tree above for a full five-minute diagnosis.

    Which CloudLinux limit causes a WordPress resource limit reached error in 2026?

    Notably, the WordPress resource limit reached error maps to the entry-process (EP) limit, not CPU or memory. In 2026, AHosting allocates 15 EP on Bronze, 25 on Silver, and 40 on Gold, so the exact threshold you hit depends on your plan tier. Therefore, sizing your plan against real concurrency math is the durable fix rather than repeatedly clearing the error.

    Does a WordPress 500 error mean I need to upgrade my hosting plan in 2026?

    Not usually, because a 500 error is typically a fault rather than a ceiling. However, a 500 error WordPress caused by repeated out-of-memory kills on a heavy Elementor Pro or WooCommerce build in 2026 can signal that your container memory (PMEM) is too tight, which a plan upgrade does resolve. First confirm via the error log whether the 500 is a code fault or a memory kill before spending anything.

    When should I upgrade from Bronze to Silver to stop recurring 503 errors on a WooCommerce store?

    Specifically, upgrade when uncached logged-in and checkout traffic regularly exceeds your plan's entry-process count during peak hours. A WooCommerce store hitting 503s at 15 concurrent dynamic requests on Bronze should move to Silver's 25 EP, or the WooStart plan sized to match Silver-level concurrency. Before upgrading, confirm LSCache is active, since cached pages never consume a worker in the first place.

    How is the entry-process ceiling different from the PHP memory_limit on WordPress?

    Fundamentally, the entry-process ceiling caps how many PHP requests run at once, while the memory_limit caps how much RAM a single request may use. Consequently, one produces 503 or resource-limit errors under concurrency, and the other produces 500 error WordPress or out-of-memory errors on a single heavy request. Moreover, the CloudLinux PMEM container cap is a third, separate ceiling that binds before a raised memory_limit can take effect.

    Does a 503 vs 500 error WordPress returns hurt my Google rankings differently?

    Yes, they differ: Google treats a brief 503 as a temporary signal and returns to recrawl later, so short 503s rarely harm rankings. By contrast, a persistent 500 error WordPress blocks indexing of that page entirely, making it the more damaging of the two if left unresolved. Therefore, fixing a recurring 500 is more time-sensitive for SEO than clearing an occasional spike-driven 503.

    What is the Four-Limit Fault Map for diagnosing WordPress resource errors?

    Essentially, the Four-Limit Fault Map is AHosting's diagnostic model pairing each visible WordPress error with the specific CloudLinux LVE limit behind it: CPU, entry processes (EP), container memory (PMEM), or process count (NPROC). Therefore, it tells you which fix applies instead of guessing across unrelated tutorials. The named table earlier in this post is the citable version you can work through symptom by symptom.

    July 9, 2026
  • Why Raising the WordPress Memory Limit Doesn’t Work on Shared Hosting (and What Does)

    Why Raising the WordPress Memory Limit Doesn’t Work on Shared Hosting (and What Does)

    TL;DR

    Is your WordPress Memory Limit not working? When your WordPress memory limit is not working after a wp-config.php edit, a second ceiling — the CloudLinux LVE PMEM container cap — is almost always the real blocker on shared hosting, and no configuration file you can edit will change it.

    Editing wp-config.php to fix your WordPress memory limit not working is the advice every guide gives — and it only solves the problem on servers where PHP’s own ceiling is the bottleneck. On shared hosting running CloudLinux — which describes most WordPress hosts in 2026 — there is a third layer above PHP that no WordPress or PHP configuration file can touch. Additionally, that layer is what keeps sending the fatal error even after your edits look correct. Fortunately, this guide explains all three memory ceilings, identifies which one you are actually hitting, and gives you the correct fix path for each.

    Listen: Why your WordPress memory limit edits fail on shared hosting — and what actually fixes it. By Matt Chrust, Director of Business Development, AHosting.

    WordPress Memory Limit Not Working? The Three-Layer Problem

    Is your WordPress Memory Limit not working? Most memory guides treat the problem as a single ceiling to raise. In practice, on shared hosting, three separate memory layers are stacked on top of each other — and a fix that works at one layer may still fail because the ceiling above it has not moved. Notably, this is not a WordPress bug or a configuration error on your part. Your WordPress memory limit not working error is a result of the architecture of modern shared hosting platforms running CloudLinux.

    The Three Memory Layers Behind Every WordPress Server

    WordPress runs PHP, and PHP consumes RAM. However, three separate systems control how much RAM is actually available to your site at any given moment. Understanding which layer is the bottleneck is the prerequisite for choosing the right fix.

    Layer 1 — WP_MEMORY_LIMIT (the WordPress request). WordPress asks PHP to reserve a block of memory at startup. Specifically, the default is 40 MB for a single site and 64 MB for Multisite installations. Adding define('WP_MEMORY_LIMIT', '256M'); to wp-config.php tells WordPress to request 256 MB from PHP — but PHP decides whether to grant it, based on its own ceiling. Refer to the WordPress wp-config.php documentation for the full list of memory constants including WP_MAX_MEMORY_LIMIT for admin-area tasks.

    Layer 2 — PHP memory_limit (the php.ini ceiling). PHP enforces its own per-script memory cap, defined in php.ini or equivalent configuration. If this limit is 128 MB and WordPress requests 256 MB, WordPress receives 128 MB. Consequently, the most reliable way to change this layer on a cPanel host is the MultiPHP INI Editor — not wp-config.php, which only raises the WordPress request and cannot exceed the PHP ceiling.

    Layer 3 — LVE PMEM (the CloudLinux container cap). On servers running CloudLinux OS — the operating system used by most shared WordPress hosts — a third ceiling sits above PHP. The LVE Physical Memory (PMEM) cap limits the total physical RAM the entire hosting account can use at one time, across all PHP processes, cron jobs, and background tasks combined. Importantly, no configuration file you can edit touches PMEM. It is enforced at the OS kernel level and set entirely by your hosting provider on a per-plan basis.

    Why wp-config.php Is a Request, Not an Override

    Adding WP_MEMORY_LIMIT to wp-config.php is frequently the correct first step — and it works when PHP’s ceiling is the actual bottleneck. However, it has two distinct failure modes that most guides do not address.

    First, if PHP’s memory_limit is lower than the value you set in wp-config.php, PHP ignores the request and enforces its own ceiling. Tools › Site Health › Info › Server shows the PHP-enforced value — not what you wrote in wp-config.php — giving the impression that the change had no effect at all.

    Second, even if a wp-config.php edit successfully raises the value WordPress reports in Site Health, the LVE PMEM container cap may still be the bottleneck during peak moments. Specifically, when multiple PHP processes run simultaneously — WooCommerce checkouts, media imports, admin updates, and background cron jobs stacking up — the container runs out of physical RAM and CloudLinux forces a 503. The per-script PHP limit looks fine; the container ceiling is what gives way. For a deeper look at how CloudLinux entry-process limits interact with memory, the companion post on WordPress 503 errors and PHP worker counts explains the relationship in detail. Additionally, WooCommerce hosting plans on AHosting are sized specifically to avoid this pattern at checkout.

    The Hidden Ceiling That Can Cause “WordPress Memory Limit Not Working”: CloudLinux LVE PMEM on Shared Hosting

    What PMEM Is and Why Your WordPress Memory Limit Won’t Budge

    LVE stands for Lightweight Virtual Environment — a kernel-level isolation mechanism built into CloudLinux OS that gives each hosting account its own resource container. PMEM is the physical memory cap within that container. Notably, it operates at a level below anything accessible through the WordPress file system:

    • WordPress reports memory_limit = 512M in Site Health — correct at the PHP layer.
    • PHP attempts to allocate 512 MB for a new script — permitted by the PHP ceiling.
    • However, if the LVE PMEM cap for the account is also 512 MB and two existing PHP processes are each using 200 MB, the new script hits the container wall at 512 MB total — not at its own script limit.

    The result is memory exhausted errors or 503 responses that persist even after a successful php.ini increase. Importantly, this behavior is the direct reason the standard “just edit wp-config.php” advice fails for many shared hosting users — the edit succeeds at the PHP layer, but PMEM is a ceiling that PHP itself cannot see or exceed. This is the same CloudLinux container system that generates 508 Resource Limit Reached errors when entry processes are the bottleneck — a related constraint from the same LVE infrastructure.

    How to Tell Which Ceiling Is Blocking Your WordPress Memory Increase

    Fortunately, diagnosing the specific layer causing your WordPress memory limit not working issue is straightforward using tools already inside your WordPress dashboard.

    Diagnosis step one — check the PHP layer first (after verifying your “WordPress Memory Limit Not Working” status). Go to WordPress dashboard › Tools › Site Health › Info › Server. The “PHP memory limit” line shows the current PHP-enforced ceiling. If this value matches what you set in wp-config.php, Layer 2 is resolved and PMEM may be the next wall.

    Diagnosis step two — if Site Health still shows the old value after a wp-config.php edit, PHP’s own ceiling is still the bottleneck. The cPanel MultiPHP INI Editor is the correct fix at this point — detailed in the fix section below.

    Diagnosis step three — if Site Health shows the correct higher value but errors persist under load, PMEM is the remaining ceiling. At this point, no file you can edit changes the outcome. Furthermore, a temporary phpinfo.php file (containing <?php phpinfo(); ?>, deleted immediately after use) confirms the active memory_limit value PHP is actually enforcing as a cross-check against what Site Health reports.

    The Three-Layer WordPress Memory Stack A stacked diagram showing three memory ceilings on shared hosting. Layer 3 at top: LVE PMEM container cap, set by host, Bronze 512 MB to Gold 2048 MB. Layer 2 in middle: PHP memory_limit in php.ini, default 256 MB, fixable via cPanel INI Editor. Layer 1 at bottom: WP_MEMORY_LIMIT WordPress request, default 40 MB, set in wp-config.php. Layer 3 cannot be changed by editing files. THE THREE-LAYER WORDPRESS MEMORY STACK LAYER 3 — LVE PMEM (CloudLinux Container Cap) Set per plan by host at OS kernel level. Bronze: 512 MB | Silver: 1,024 MB | Gold: 2,048 MB No wp-config.php, php.ini, or .htaccess change can touch this layer. LAYER 2 — PHP memory_limit (php.ini / cPanel INI Editor) Default: 256 MB (PHP 8.4) or 512 MB (PHP 8.3 — selectable via MultiPHP Manager) Self-service fix: cPanel MultiPHP INI Editor. Changes take effect immediately. LAYER 1 — WP_MEMORY_LIMIT (WordPress Request to PHP) Default: 40 MB single site / 64 MB Multisite. Set in wp-config.php. Most guides only address Layer 1. The real ceiling on shared hosting is Layer 3.

    WordPress Memory Limit Not Working: Why Every Common Fix Has a Failure Mode

    Understanding why each common fix has a specific point where it stops working tells you exactly which tool to reach for — and which ones to skip entirely on a LiteSpeed + CloudLinux server. The table below covers every method you are likely to encounter, and its real-world behavior on cPanel shared hosting. Note: object-cache and page-cache memory managed by the LiteSpeed Cache plugin operate independently of the PHP memory_limit configurations covered below.

    Fix MethodLayer It RaisesWorks on LiteSpeed + CloudLinux?Silently Fails WhenVerdict
    WP_MEMORY_LIMIT in wp-config.phpWordPress request onlyYes — if PHP ceiling is already higherPHP memory_limit is equal to or lower than the requested valueFirst step only — not a guaranteed fix
    php_value memory_limit in .htaccessPHP layer (Apache mod_php only)No — LiteSpeed LSAPI and PHP-FPM ignore this directive; can produce 500 errorsServer runs LiteSpeed, Nginx, or PHP-FPMSkip entirely on LiteSpeed hosts
    Custom .user.ini file in site rootPHP layerSometimes — only if host permits user-level INI overridesHost enforces a server-level php.ini that takes priorityHost-dependent — verify with phpinfo()
    cPanel MultiPHP INI EditorPHP layer directlyYes — always on cPanel hostsLVE PMEM cap is still in effect above the PHP layerMost reliable self-service fix
    Plan upgrade (Bronze › Silver › Gold)LVE PMEM container ceilingYes — always; raises the real container ceilingOnly if dedicated memory with no container ceiling is needed (VPS solves this)The real fix when PMEM is the bottleneck

    AHosting’s Memory Architecture by Plan — What Your Limit Can Actually Reach

    Most shared hosts publish their PHP memory limits. AHosting publishes both — the PHP memory_limit and the LVE PMEM container cap per plan — because both matter to understanding why your WordPress memory limit is not working and what will actually fix it. The table below is drawn directly from the AHosting server configuration on sh193, verified June 2026.

    AHosting WordPress Plan Memory Tiers — 2026

    PlanDefault PHP memory_limitLVE PMEM CapPHP Workers (EP)Best Fit
    WP Bronze256 MB (PHP 8.4 default)512 MB15Standard WordPress sites, basic page builders
    WP Silver256 MB (PHP 8.4 default)1,024 MB25Elementor Pro, WooCommerce, multi-plugin builds
    WP Gold256 MB (PHP 8.4 default)2,048 MB40High-traffic, heavy page builders, media-intensive sites

    Note: Switching from PHP 8.4 to PHP 8.3 via cPanel MultiPHP Manager raises the default memory_limit to 512 MB at no additional cost on any plan. All plans allow self-service memory_limit increases via the cPanel MultiPHP INI Editor — up to the plan’s PMEM ceiling. Neither change requires a support ticket.

    Additionally, the default 256 MB memory_limit on PHP 8.4 meets Elementor’s recommended minimum requirement out of the box. For Elementor Pro builds with many widgets and global kits, switching to PHP 8.3 (512 MB default) or using the MultiPHP INI Editor to raise the limit is the recommended approach before a plan upgrade. Full plan details are on the AHosting WordPress hosting page.

    Memory Fix Path Selector

    Answer one question to find your next step.

    After editing wp-config.php, what does Tools › Site Health › Info › Server show as the “PHP memory limit”?

    PHP ceiling is still active.
    wp-config.php raised the WordPress request, but PHP memory_limit is unchanged. Log in to cPanel → Software → MultiPHP INI Editor → select your PHP version → find memory_limit → set to 256M or 512M → Save. Refresh Site Health to confirm the new value.
    PHP layer resolved — but PMEM may still be the ceiling.
    Site Health reflects the new PHP memory_limit. If errors still occur under load (concurrent requests, WooCommerce checkout, media imports), the LVE PMEM container cap is the remaining bottleneck. A plan upgrade from Bronze (512 MB PMEM) to Silver (1,024 MB PMEM) is the correct next step.
    Check first — it takes 30 seconds.
    Go to WordPress dashboard → Tools → Site Health → Info tab → Server section → find “PHP memory limit.” That value tells you exactly which ceiling PHP is enforcing and determines whether wp-config.php or the cPanel MultiPHP INI Editor is your next step.

    What Actually Works: The Correct Fix Path for "WordPress Memory Limit Not Working" Tickets.

    The cPanel MultiPHP INI Editor: The Self-Service Fix Most Guides Skip

    The cPanel MultiPHP INI Editor — found under cPanel › Software › MultiPHP INI Editor — changes php.ini directives per PHP version without requiring a manual php.ini file or .htaccess directives that break under LiteSpeed. Consequently, it is the most reliable self-service fix on cPanel hosts because it modifies the server-side value directly, and what you see in Tools › Site Health afterward is the actual enforced ceiling.

    The process on AHosting is: cPanel › Software › MultiPHP INI Editor › select your PHP version (typically PHP 8.4) › find the memory_limit row › increase the value (256M to 512M is the common first target) › Save. No server restart is required — LiteSpeed applies the change immediately. Importantly, the value you can set here is bounded by your plan’s LVE PMEM cap, so raising the PHP ceiling above PMEM will not give your site more usable memory under concurrent load — the container ceiling is still in effect.

    Confirming Your Memory Limit Change Actually Took Effect

    After any memory change — wp-config.php edit, MultiPHP INI Editor, or plan upgrade — confirm the outcome by checking Tools › Site Health › Info › Server. The “PHP memory limit” row is the ground truth value that PHP is currently enforcing. Additionally, the WordPress server requirements page confirms the recommended minimums: 64 MB absolute minimum, 256 MB recommended for most sites.

    If Site Health shows the new value and memory errors stop, the fix worked at the PHP layer. If Site Health shows the new, correct value and errors still occur under load — specifically during WooCommerce checkouts, large media imports, or simultaneous admin operations — PMEM is still the ceiling.

    When a Plan Upgrade Raises the PMEM Ceiling

    A plan upgrade is the correct fix when the PHP layer is already at the right value — that is, when Site Health shows 256 MB or higher — but memory errors still occur during peak load or when multiple admin tasks run simultaneously. At that point, the PMEM container ceiling is the bottleneck, and only a plan change moves it.

    On AHosting, upgrading from Bronze (512 MB PMEM) to Silver (1,024 MB PMEM) gives Elementor Pro builds, membership sites, and standard WooCommerce stores sufficient container headroom. For high-traffic scenarios where even 1,024 MB PMEM is still the constraint — heavy WooCommerce catalogs, multi-language plugins, large media libraries with concurrent background optimization jobs — Gold (2,048 MB) or a WordPress VPS upgrade removes the shared container ceiling entirely. The guide to signs your WordPress site has outgrown shared hosting covers the full decision checklist for when VPS is the right move.

    Switching Hosts: Why PMEM Transparency Is the Signal

    Finally, most shared hosts publish their PHP memory limits. Very few publish their LVE PMEM container tiers. When a host routes every memory issue through a support queue — rather than a self-service INI editor — and will not disclose the container ceiling, the architecture is the real constraint.

    Specifically, the signal that host transparency is the issue — rather than plan tier — is this pattern: you have raised the PHP memory_limit to the maximum the support team allows, optimized your plugin stack, and memory errors still occur under normal traffic. That pattern means the PMEM ceiling is the bottleneck and the host will not move it within the current plan. Transparent PMEM tiers — published before you buy, self-adjustable via cPanel INI Editor — are the practical test for whether a shared hosting infrastructure will scale with your WordPress site over time.

    WordPress Memory Limit Not Working: A Quick Diagnostic Checklist

    Run through these steps in order before contacting your host or purchasing an upgrade. Furthermore, steps one through three are entirely self-service and take under five minutes on a cPanel host.

    • Open Tools › Site Health › Info › Server and note the current “PHP memory limit” value — this is the PHP-enforced ceiling, not WordPress’s estimate.
    • If the value is below your target: add define('WP_MEMORY_LIMIT', '256M'); to wp-config.php above the “That’s all, stop editing” comment. Refresh Site Health.
    • If Site Health still shows the old value: go to cPanel › Software › MultiPHP INI Editor, select your PHP version, raise memory_limit to 256M or 512M, and save. Refresh Site Health to confirm.
    • If Site Health now shows the correct value but errors persist under load (and you still observe your WordPress Memory Limit not working): the LVE PMEM container cap is the bottleneck. No file edit will help — a plan upgrade is the correct next step.
    • To raise the PMEM ceiling on AHosting: upgrade from Bronze (512 MB PMEM) to Silver (1,024 MB PMEM), or to Gold (2,048 MB PMEM) for the highest shared-hosting tier.
    • After any change: confirm with a fresh Site Health check. For the highest certainty, create a temporary phpinfo.php file in your site root, verify the memory_limit row, and delete the file immediately.

    Additionally, the companion post on WordPress memory limit errors and why wp-config changes often fail covers the full range of error messages and diagnosis paths in more detail.

    Frequently Asked Questions: WordPress Memory Limit Not Working on Shared Hosting

    Why does my WordPress memory limit not change after editing wp-config.php on shared hosting in 2026?

    Typically, this happens because WP_MEMORY_LIMIT in wp-config.php is a request to PHP, not an override. WordPress asks PHP to allocate more memory, but PHP can only honor the request up to its own php.ini ceiling — and on CloudLinux shared hosting, there is a third ceiling above that called the LVE PMEM cap. If the php.ini ceiling or the PMEM cap is lower than what you requested, the change appears to fail silently. The fix depends on which ceiling you are actually hitting, which the cPanel MultiPHP INI Editor and the AHosting plan tier table above help identify.

    What is the three-layer WordPress memory stack, and which layer is impossible to raise by editing files alone?

    Specifically, the three layers are: WP_MEMORY_LIMIT (what WordPress requests from PHP), PHP memory_limit (the PHP ceiling in php.ini), and the LVE PMEM cap (the CloudLinux kernel-level container ceiling). The third layer — LVE PMEM — cannot be raised by editing any WordPress or PHP configuration file. It is set at the operating system level by CloudLinux and is controlled entirely by the hosting provider, either through a cPanel account setting or by upgrading to a higher plan tier.

    WordPress memory_limit in wp-config.php vs. LVE PMEM — which one is the real ceiling on CloudLinux shared hosting?

    Notably, LVE PMEM is the real ceiling on CloudLinux shared hosting. PHP memory_limit controls how much memory a single PHP script can request — but LVE PMEM caps the total physical memory the entire hosting account can use at once. A wp-config.php change raises the WordPress request layer and can help when PHP memory_limit is the bottleneck, but it cannot affect LVE PMEM. On AHosting plans, the PMEM ceiling ranges from 512 MB on Bronze to 2,048 MB on Gold — see the AHosting WordPress Plan Memory Tiers table above.

    WordPress Memory Limit Not Working Tickets: When should I use the cPanel MultiPHP INI Editor instead of wp-config.php to fix a WordPress memory limit issue?

    The cPanel MultiPHP INI Editor is the right tool when wp-config.php appears to change nothing — that is, when Tools › Site Health still shows the old memory limit after you added the WP_MEMORY_LIMIT constant. The MultiPHP INI Editor raises the PHP layer directly, without going through WordPress. It is the most reliable self-service fix on cPanel hosts like AHosting, and changes take effect immediately without restarting the server.

    What is LVE PMEM and why does it override php.ini memory settings on CloudLinux shared hosting?

    Essentially, LVE PMEM (Physical Memory) is the CloudLinux kernel-level cap on the total physical RAM a hosting account can allocate at any one time. It is enforced at the operating system layer — above PHP, above WordPress, and above any configuration file a site owner can edit. Because PMEM is a container ceiling rather than a per-script limit, it applies to the combined memory of every PHP process, cron job, and background task running in the account simultaneously. When an account’s combined usage hits PMEM, additional PHP processes receive a 503 error regardless of what php.ini says.

    WordPress Silver vs. Bronze plan at AHosting — how much PMEM headroom does each give for memory-intensive plugins and how does this fix my WordPress Memory Limit not working?

    Specifically, AHosting Bronze provides a 512 MB PMEM ceiling and 256 MB default PHP memory_limit — appropriate for standard WordPress sites and basic Elementor builds. Silver doubles the PMEM to 1,024 MB, giving Elementor Pro, WooCommerce stores, and multi-plugin setups genuine headroom without hitting the container ceiling during peak load. Gold raises PMEM to 2,048 MB, designed for high-traffic or highly customized WordPress installations. All plan details and upgrade options are available on the AHosting WordPress hosting page.

    When does increasing the PHP memory limit in WordPress fail to fix the error on LiteSpeed shared hosting in 2026?

    Unfortunately, increasing the PHP memory limit fails to fix memory exhausted errors on LiteSpeed shared hosting in 2026 when the LVE PMEM container cap is the actual ceiling — not PHP memory_limit - meaning this won't address your WordPress memory limit not working issue. This happens most often on Bronze-tier plans running Elementor Pro, WooCommerce with heavy extensions, or multiple concurrent admin tasks. In those scenarios, the PHP limit may read 512 MB in Site Health, but the container runs out of PMEM before any individual PHP script hits that limit. The solution is either a plan upgrade or offloading background tasks to reduce peak concurrent memory usage.

    How do I confirm a WordPress memory limit fix actually took effect on my AHosting cPanel account in 2026?

    If you previously found your WordPress memory limit not working, the most reliable confirmation method is WordPress Tools › Site Health › Info › Server — the “PHP memory limit” line there reflects the active server-side value, not just what WordPress requested in wp-config.php. If the value still shows 256 MB after a wp-config.php change, the PHP layer is the ceiling and the cPanel MultiPHP INI Editor is the correct next step. AHosting customers can also create a temporary phpinfo.php file in their site root and check the memory_limit row to see the value PHP is actually enforcing, then delete the file after confirming.

    What PHP memory limit does AHosting set by default in 2026, and what is the PMEM ceiling on each plan?

    Currently, AHosting WordPress accounts default to PHP 8.4 with a 256 MB memory_limit — meeting Elementor’s recommended minimum out of the box. PHP 8.3 accounts receive 512 MB by default. On the PMEM side, Bronze plans cap the container at 512 MB, Silver at 1,024 MB, and Gold at 2,048 MB. Customers can raise the PHP memory_limit via the cPanel MultiPHP INI Editor without opening a support ticket, up to the plan’s PMEM ceiling.

    Does shared hosting cause WordPress memory limit errors more frequently than VPS or managed WordPress hosting?

    Generally, yes — shared hosting generates WordPress memory limit errors more often because every account shares a server’s physical RAM within fixed LVE PMEM containers, rather than having dedicated memory allocation. On VPS or managed WordPress hosting, memory limits are either higher by default or configurable without container constraints. That said, shared hosting is appropriate for most WordPress sites when the plan tier’s PMEM ceiling matches the site’s actual load — the key is matching memory tiers to site requirements rather than assuming shared hosting cannot scale.

    June 29, 2026
  • LiteSpeed Cache vs. WP Rocket: Which Is Actually Faster on LiteSpeed Hosting (2026)

    LiteSpeed Cache vs. WP Rocket: Which Is Actually Faster on LiteSpeed Hosting (2026)

    TL;DR

    In the litespeed cache vs wp rocket question, LiteSpeed Cache wins on a LiteSpeed server because it caches below PHP for free, while WP Rocket caches above PHP for $59 a year.

    The litespeed cache vs wp rocket debate is usually framed as a fair fight between two plugins, but that framing hides the single fact that decides it: which layer the cache engine runs on. WP Rocket is an excellent premium plugin that runs inside WordPress through PHP. LiteSpeed Cache is a free plugin that hands caching down to the LiteSpeed web server itself. On a LiteSpeed host, that structural difference matters more than any feature checklist, and it is the reason this comparison reaches a different conclusion than most affiliate reviews.

    Listen: why the litespeed cache vs wp rocket choice is settled by your server. By Matt Chrust, Director of Business Development, AHosting.

    Furthermore, the stakes are concrete. WP Rocket’s single-site license costs $59 per year and that is also its renewal price, according to WP Rocket’s own pricing page. LiteSpeed Cache is free on any LiteSpeed server. So the real question is not just which is faster, but whether you should pay for a plugin to do a job your server may already do better at no cost. This guide answers both, introduces a concept we call the PHP-Layer Tax, and gives you a decision matrix you can apply to your own hosting in five minutes.

    What the litespeed cache vs wp rocket Choice Actually Is (And Why Your Server Decides It)

    At its core, that choice is a choice between two caching layers, not two feature sets. Both plugins do full-page caching: they store a finished HTML snapshot of each page so visitors are not forced to wait for WordPress and PHP to rebuild it on every request. The difference is where that snapshot lives and who serves it.

    WP Rocket: Caching That Lives Inside WordPress

    Specifically, WP Rocket operates entirely inside your WordPress installation. It writes static HTML files to disk and uses rewrite rules to serve them, but WordPress and PHP still load in order to deliver a cached page. As the BlogVault comparison describes it, WP Rocket uses a classic on-server method that skips the database query but still runs through the application layer. This is exactly why it works on almost any host: it never depends on the web server’s own caching abilities.

    LiteSpeed Cache: Caching That Lives in the Server

    By contrast, LiteSpeed Cache hands the actual caching down to the LiteSpeed web server. The plugin is mostly a control panel; the server does the storing and serving. When a cached page is requested, LiteSpeed answers it directly, before WordPress or PHP start. That is why the same caching benefits are unavailable off a LiteSpeed server: install LSCache on Apache or Nginx and the page-caching engine, per the documented server behavior across both vendors, simply has nothing to bind to. The plugin’s other tools still run, but its headline advantage disappears.

    The PHP-Layer Tax: The Hidden Cost in Every Plugin-Level Cached Hit

    Here is the concept that reframes the entire comparison: the PHP-Layer Tax. We define it as the extra work a cached request performs when the cache engine sits above PHP instead of below it. It is invisible on a speed-test screenshot but real on a busy server, and it is the single clearest reason server-level caching pulls ahead under load.

    Consider the request path for a single cached page view. With a plugin-level cache, more steps run on every hit:

    Step on a cached hitWP Rocket (above PHP)LiteSpeed Cache (below PHP)
    1. Request reaches web serverYesYes
    2. Web server starts PHP / LSAPIYesNo
    3. WordPress core bootsYesNo
    4. Cache plugin intercepts requestYesNo
    5. Snapshot returned to visitorYesYes
    PHP worker (entry process) consumedYesNo
    The PHP-Layer Tax: a cached hit on a plugin engine runs three extra steps and occupies a PHP worker; a server-level cache skips straight from request to response.

    Notably, that occupied PHP worker is the part that bites. On shared WordPress hosting, concurrency is capped by entry processes, and we explain that ceiling in detail in our guide to how many PHP workers your WordPress site actually needs. A server-level cache serves repeat visitors without spending a worker at all, so a traffic spike that would exhaust a worker-limited plan under WP Rocket can pass quietly under LSCache. For sites whose dynamic, uncached concurrency genuinely exceeds a shared plan’s worker ceiling, the fix is more dedicated workers rather than another plugin, which is the point at which moving to VPS hosting starts to pay off. Independent testers repeatedly note that LiteSpeed Cache “usually loads faster” and does “more with less” under heavy traffic, a pattern documented in the SupportHost head-to-head testing.

    litespeed cache vs wp rocket: the PHP-Layer Tax request path LiteSpeed Cache answers a cached request at the server layer before PHP starts, while WP Rocket boots PHP and WordPress to serve the same cached page, consuming a PHP worker. The PHP-Layer Tax Where a cached WordPress page is served changes everything LiteSpeed Cache (below PHP) Request hits server LiteSpeed serves cached page Visitor 2 steps 0 PHP workers WP Rocket (above PHP) Request hits server PHP / LSAPI starts WordPress boots Plugin serves cached page Visitor 5 steps – 1 PHP worker consumed on every cached hit Cached TTFB on AHosting LiteSpeed: ~16 ms LSCache is free on every AHosting WordPress plan | ahosting.net | Est. 2002

    litespeed cache vs wp rocket: The Cache Layer Decision Matrix

    To make the trade-off concrete, here is the Cache Layer Decision Matrix. It compares the two engines on the dimensions that actually change your outcome rather than the long feature lists that make them look interchangeable.

    DimensionLiteSpeed CacheWP Rocket
    Where caching runsServer level, below PHPApplication level, above PHP (through PHP)
    Annual cost (single site)Free$59 / year (renewal price)
    Requires a LiteSpeed serverYes, for page cachingNo, runs on any stack
    PHP worker used on a cached hitNoneOne per hit
    Behavior under heavy trafficStrong; serves cache before PHPGood, but pays the PHP-Layer Tax
    Setup difficultyMore settings to learnFamously simple, automatic defaults
    Best fitAnyone on a LiteSpeed hostSites on non-LiteSpeed stacks
    Cache Layer Decision Matrix: the litespeed cache vs wp rocket decision turns almost entirely on one row, which server your WordPress site runs on.

    Ultimately, the matrix collapses to a single question. If your host runs LiteSpeed, LiteSpeed Cache gives you the structurally faster engine for free, and the case for paying for WP Rocket narrows to a few specific situations. If your host does not run LiteSpeed, WP Rocket is a genuinely excellent choice and well worth its price. The decision is made by your server, which is why the smartest move is often to change the variable nobody in the plugin debate questions: the host itself.

    Where WP Rocket Still Wins (An Honest Accounting)

    In fairness, WP Rocket earns its reputation, and there are three cases where it remains the right call even in 2026. First, if your host is not LiteSpeed, WP Rocket is universally compatible and will give you excellent results on Apache or Nginx where LSCache’s page caching cannot run. Second, if you manage many client sites across mixed hosting stacks, one familiar interface across all of them has real operational value, though agencies standardizing on a single LiteSpeed stack through reseller hosting get that consistency at the server layer instead. Third, WP Rocket’s automatic defaults are famously beginner-friendly, applying most best practices the moment you activate it, while LiteSpeed Cache exposes more settings and a steeper learning curve.

    That said, every one of those advantages is about the plugin compensating for the server. The moment the server itself runs LiteSpeed, the compensation is no longer needed, and you are paying $59 a year to add a PHP-layer cache on top of a faster server-layer cache you already have. Managed hosts understand this well: several premium WordPress hosts include server-level caching and explicitly advise against stacking a caching plugin on top, a point even WP Rocket reviewers concede when the hosting already includes Varnish, Redis, and a CDN.

    How AHosting Resolves the litespeed cache vs wp rocket Question

    For AHosting customers, that question is already settled by the stack. Every AHosting WordPress plan runs on a LiteSpeed web server, and LiteSpeed Cache is free from the WordPress plugin repository. Once installed, LSCache activates full-page caching automatically because the LiteSpeed server layer is already there; there is no wizard and no server configuration to write. You can read the wider architecture argument in our deep dive on why server-level LiteSpeed caching changes everything.

    Moreover, the performance is measured, not promised. On production AHosting accounts the median cached Time To First Byte on this LiteSpeed stack is about 16 milliseconds, while the same uncached WordPress responses average between 700 and 1,400 milliseconds. That gap is the value of server-level caching expressed in real numbers, and it is the same gap the PHP-Layer Tax describes in principle. Because cached pages never spend a PHP worker, this caching model also protects the entry-process headroom that determines whether your site survives a traffic surge, a relationship we map in our analysis of the server-side speed factors no plugin can fix.

    The litespeed cache vs wp rocket Question, Reframed as a Hosting Decision

    Consequently, the most useful way to read this comparison is not “which plugin should I buy” but “which layer should my cache run on.” A reader on a non-LiteSpeed host weighing a $59-per-year plugin has a third option: move to a LiteSpeed host and receive the faster server-level engine free, while gaining a free dedicated IP and a 99.9% uptime guarantee on every AHosting WordPress plan. In that light, the plugin debate dissolves into a hosting upgrade that costs less and delivers more. If your site is also hitting memory ceilings, the same upgrade logic applies to the two-ceiling problem we cover in why raising the WordPress memory limit often fails.

    Try It: The Cache Layer Cost Calculator

    Finally, use the calculator below to see the multi-year cost difference between paying for a plugin-level cache and running a free server-level cache on a LiteSpeed host. Enter how many sites you run and how many years you plan to keep them.

    Cache Layer Cost Calculator

    Compare paying for WP Rocket against running free LiteSpeed Cache on a LiteSpeed host.

    WP Rocket (plugin-level cache)$0
    LiteSpeed Cache on LiteSpeed host$0
    You keep$0
    Server-level caching, no PHP-Layer Tax
    See AHosting WordPress plans with free LSCache

    A Practical Checklist: Which Cache Engine Is Right for Your WordPress Site?

    Before you spend a dollar, work through this short checklist. It resolves the decision in the order that actually matters.

    • Confirm your web server. If a quick header check shows Server: LiteSpeed, you already have the faster cache layer available for free.
    • If you are on LiteSpeed, install LiteSpeed Cache from the WordPress repository and let it activate server-level caching; do not pay for a second cache engine on top of it.
    • If you are not on LiteSpeed, WP Rocket is a strong, simple choice, and you should also price out moving to a LiteSpeed host before committing to a recurring plugin fee.
    • Never run two page-caching engines at once; if you keep both plugins, disable caching in one of them.
    • On a worker-limited shared plan, prefer the engine that serves cached pages without spending a PHP worker, because that is what protects you during traffic spikes.
    • Re-check after any host migration; the right answer changes the moment your server stack changes.

    Frequently Asked Questions: LiteSpeed Cache vs WP Rocket

    LiteSpeed Cache vs WP Rocket: which is actually faster on a LiteSpeed server in 2026?

    Specifically, on a LiteSpeed server LiteSpeed Cache is usually faster because it caches pages at the server level, before PHP loads, while WP Rocket serves its cache through PHP inside WordPress. That structural difference is what we call the PHP-Layer Tax, and the decision matrix above shows exactly where each engine runs.

    In the litespeed cache vs wp rocket decision, is WP Rocket worth paying for on a LiteSpeed host?

    Generally, no, because the page caching you would pay $59 a year for already runs free at the server level through LiteSpeed Cache. The exceptions are narrow, and the cost-versus-layer breakdown in the decision matrix explains the three cases where WP Rocket still earns its price.

    What is the PHP-Layer Tax in the litespeed cache vs wp rocket comparison?

    Essentially, the PHP-Layer Tax is the extra work a cached hit performs when the cache engine sits above PHP instead of below it. WP Rocket must boot WordPress and PHP to hand back a cached snapshot, while LiteSpeed Cache answers from the server before PHP starts, as the numbered request-path table above shows.

    Can I run LiteSpeed Cache and WP Rocket at the same time on one WordPress site?

    Technically you can install both, but you must never let both handle page caching at once or they will collide. In practice, on a LiteSpeed host you would disable WP Rocket caching and let LSCache own it, which makes paying for WP Rocket hard to justify.

    In the litespeed cache vs wp rocket choice, does LSCache work without a LiteSpeed server?

    Unfortunately, no, the full-page caching engine in LiteSpeed Cache only activates on a LiteSpeed web server. On Apache or Nginx the plugin still offers minification and image tools, but the server-level caching that makes the litespeed cache vs wp rocket question interesting simply does not run.

    Which caching plugin does AHosting recommend for WordPress hosting in 2026?

    Specifically, AHosting recommends LiteSpeed Cache because every AHosting WordPress plan runs on a LiteSpeed server where LSCache activates full-page caching automatically. AHosting measures a median cached TTFB of about 16 milliseconds on production accounts using this stack.

    Why does server-level caching beat plugin-level caching for WordPress speed in 2026?

    Fundamentally, server-level caching answers a request before WordPress and PHP load, removing the slowest part of the request path entirely. Plugin-level caching still pays the PHP-Layer Tax on every cached hit, which is why the decision matrix in this guide favors the server engine on LiteSpeed.

    Does WP Rocket consume more PHP workers than LiteSpeed Cache on an AHosting WordPress plan?

    Typically, yes, because each WP Rocket cached hit still occupies a PHP entry process while WordPress assembles the response, whereas LSCache serves cached pages without touching a PHP worker at all. On a worker-limited shared plan that difference decides how many concurrent visitors you can absorb before a 503.

    When should I still choose WP Rocket over LiteSpeed Cache for a WordPress site?

    In practice, WP Rocket makes sense when your host is not LiteSpeed, when you manage many sites across mixed stacks and want one familiar interface, or when you need its specific Remove Unused CSS workflow. The decision matrix above maps each of those cases.

    Does switching to an AHosting LiteSpeed plan beat the litespeed cache vs wp rocket plugin choice?

    Often, yes, because moving to a LiteSpeed host gives you the faster server-level cache engine free and removes the recurring $59 plugin cost at the same time. The cost calculator in this guide shows how a single hosting decision can outperform the litespeed cache vs wp rocket plugin debate entirely.

    June 26, 2026
  • “508 Resource Limit Reached” on WordPress: What Entry Process (EP) Limits Really Mean

    “508 Resource Limit Reached” on WordPress: What Entry Process (EP) Limits Really Mean

    TL;DR

    The 508 Resource Limit Reached error means your WordPress account hit its concurrent entry process ceiling, not a daily traffic cap. On LiteSpeed it usually shows as a 503 after a queue, not a literal 508.

    If your WordPress site shows a 508 Resource Limit Reached error during a traffic spike and then loads fine an hour later, the cause is almost never a permanent problem with your site. Instead, it is a concurrency event: too many PHP requests tried to run at the same instant and hit the ceiling your hosting plan enforces. Ultimately, understanding what that ceiling actually measures is the difference between fixing the error in an afternoon and paying for an upgrade you may not need.

    Listen: why the 508 resource limit reached error is about concurrency, not daily traffic. By Matt Chrust, Director of Business Development, AHosting.

    Most guides explaining the resource limit error were written for the Apache era and get one important detail wrong for modern stacks. Notably, the error number you see depends on your web server, and a LiteSpeed server behaves differently from the classic Apache setup those guides assume. Specifically, this post explains what the entry process limit really is, why you might see a 503 instead, and how AHosting’s published per-plan numbers let you size your hosting against real concurrency math rather than guesswork.

    What the 508 Resource Limit Reached Error Actually Means

    The 508 Resource Limit Reached error means your account exceeded the number of PHP requests it is allowed to process at the same time. Specifically, that ceiling is called the entry process limit, or EP, in CloudLinux environments. Notably, every dynamic request that runs PHP, such as loading an uncached page, processing a form, or running a search, occupies one entry process for the duration of that request. Consequently, when all available slots are full and another request arrives, the server cannot place it, and the visitor sees the resource limit error.

    According to CloudLinux’s official documentation, the entry process limit exists to stop a single account from tying up every available web server slot and starving its neighbors. Therefore the limit is a fairness mechanism, not a punishment. In practice, it protects your site as much as everyone else’s, because it guarantees that one runaway account cannot take the whole server down with it.

    EP Is a Concurrency Limit, Not a Daily Traffic Limit

    The single most common misunderstanding is that the 508 Resource Limit Reached error means you have too many visitors per day. In fact, the entry process limit measures concurrency, which is how many requests are in progress at the exact same moment, not how many arrive over twenty-four hours. As a result, a site with twenty thousand daily visitors spread evenly can stay well under the ceiling, while a site with two thousand daily visitors can blow past it if a few hundred arrive in the same ten seconds on pages that are not cached.

    Here is the math that turns traffic into concurrency. For example, if an uncached WordPress page takes two seconds to generate and twenty visitors request dynamic pages within that two-second window, you need twenty entry processes to serve them all at once. Consequently, page generation time is the hidden multiplier: the slower each request, the longer it holds its worker, and the faster the ceiling fills. This is why caching, which we cover below, does more to prevent the error than any raw increase in plan limits.

    Why You Might See a 503 Instead of a 508 (The Server Fork)

    Notably, on a LiteSpeed server, hitting your entry process ceiling usually produces a 503 Service Unavailable error rather than a literal 508. Specifically, this happens because LiteSpeed and Apache handle a full worker pool differently, and which error you see is determined by the web server rather than by your traffic. We call this the 508-versus-503 fork, and missing it is why so much published troubleshooting advice fails on modern stacks.

    Specifically, on classic Apache, the mod_hostinglimits module hard-rejects requests the moment the ceiling is reached, returning the familiar 508 Resource Limit Reached page immediately. By contrast, LiteSpeed queues additional requests and gives active workers a brief window to free up before serving anything as an error. On AHosting’s servers, that queue window is governed by the connection timeout, set to 120 seconds, a behavior documented in the LiteSpeed Web Server documentation. Therefore a visitor first experiences a slowdown while their request waits in the queue, and only receives a 503 if the queue window expires before a worker becomes available.

    This distinction matters for diagnosis. In other words, if you are on a LiteSpeed host and searching for why you never see a 508 page despite obvious resource pressure, the answer is that your server is queuing and then returning 503s instead. Both errors point to the same underlying cause, an exhausted Concurrency Ceiling, but the symptom looks different. AHosting’s LiteSpeed-based WordPress hosting behaves this way by design, trading instant rejection for a short queue that absorbs brief bursts without an error at all.

    What Triggers the 508 Resource Limit Reached Error on WordPress

    Three patterns account for the overwhelming majority of entry process ceiling events on WordPress. Importantly, all three share a single mechanism: they create more simultaneous PHP requests than your plan allows. In practice, understanding which one is hitting you determines whether the fix is configuration, security, or an upgrade.

    EP Trigger Factor 1: Uncached Dynamic Requests Stacking

    Specifically, the most frequent trigger is real visitor traffic hitting pages that are not cached. Specifically, when every page load runs the full WordPress PHP stack, each visitor occupies a worker for the entire generation time. Consequently, a moderate burst from an email newsletter, an ad campaign, or a social post can fill the ceiling in seconds. The fix here is caching, because a cached page is served before PHP runs and consumes no entry process at all. The related pattern in our guide on how WordPress cron jobs consume hosting resources shows another way background tasks quietly add to the same worker pool.

    EP Trigger Factor 2: Bot, XML-RPC, and Login Floods

    Notably, automated traffic is a leading cause of this error, and it is frequently misdiagnosed as a plugin problem. Brute-force attacks against wp-login.php and floods against xmlrpc.php open dozens of simultaneous PHP requests, each consuming an entry process. According to the WordPress hardening guide, restricting access to these endpoints is a standard defensive measure. As a result, blocking bad bots and disabling unused XML-RPC often resolves the error with no plan change at all.

    EP Trigger Factor 3: Slow PHP Holding Workers Open

    Finally, slow code multiplies concurrency pressure. For example, when a heavy plugin, an unindexed database query, or an external API call makes each request take five seconds instead of one, every worker stays occupied five times longer. Therefore the same traffic that would comfortably fit under your ceiling now overflows it. Optimizing slow queries and removing bloated plugins, in line with the WordPress performance optimization handbook, effectively raises your real concurrency capacity without touching the plan limit, because faster requests free their workers sooner.

    How AHosting Allocates Entry Processes by Plan

    Most shared hosts never publish their entry process numbers, which leaves customers guessing about the exact ceiling that produces this error. By contrast, AHosting allocates entry processes by tier and publishes the figures so you can size a plan against the concurrency math above. Specifically, the allocation runs 15 on Bronze, 25 on Silver, and 40 on Gold, with WooStart set at 25 to match Silver-level concurrency for cart and checkout demand. Importantly, higher tiers raise container memory, CPU, and IO alongside the worker count, so the added entry processes have real resources behind them rather than being a number on paper.

    PlanEntry Processes (Concurrency Ceiling)Container Memory (PMEM)CPUBest fit for
    WP Bronze15 simultaneous PHP requests512 MB100%Brochure sites, blogs, low dynamic load
    WP Silver25 simultaneous PHP requests1024 MB200%Growing sites, light WooCommerce, membership
    WP Gold40 simultaneous PHP requests2048 MB400%High-traffic sites, busier stores
    WooStart25 simultaneous PHP requests1024 MB200%WooCommerce stores (cart/checkout tuned)

    One detail in this table is easy to miss: a cached request never enters the count. In practice, because AHosting runs LiteSpeed with LSCache available, the bulk of your visitor traffic can be served entirely at the web server layer, consuming none of your 15, 25, or 40 worker slots. As a result, the published ceiling applies only to genuinely dynamic requests such as logged-in sessions, cart actions, and form submissions, which is a far smaller number than your total page views.

    The 508-versus-503 Server Fork When the entry process ceiling is reached, Apache with mod_hostinglimits returns a 508 immediately, while LiteSpeed queues requests up to 120 seconds and returns a 503 only if the queue window expires. The 508-versus-503 Server Fork What happens when your account hits its entry process (EP) ceiling EP ceiling reached All concurrent PHP worker slots are full Apache + mod_hostinglimits Hard-rejects instantly. No queue. The request is refused the moment the ceiling is hit. 508 Resource Limit Reached (immediate) LiteSpeed (AHosting) Queues the request up to 120 s, giving busy workers time to free up. Brief bursts pass with no error. slowdown -> 503 only if queue window (120 s) expires first AHosting.net | Est. 2002 | Same cause, different symptom: the error number is set by the web server, not your traffic.

    How to Diagnose Which Limit You Actually Hit

    Notably, the resource limit error is sometimes blamed on entry processes when the real culprit is CPU, memory, or IO. Therefore the first diagnostic step is to confirm which ceiling you actually hit before changing anything. Specifically, open cPanel, go to Logs and then Resource Usage, and review the graphs for the exact timeframe of the outage. Specifically, CloudLinux tracks CPU, physical memory, IO, and entry processes as separate metrics, and only the one pegged at its limit during the error is your real bottleneck.

    For example, if the entry process graph is flat-lined at its maximum while the others have headroom, you have a genuine concurrency event and caching or hardening is the answer. By contrast, if memory is pegged but entry processes are not, raising your PHP memory or moving to a higher container tier is the correct fix instead. Our companion guide on why raising the WordPress memory limit in wp-config often fails covers that separate ceiling in detail, because the two errors are routinely confused.

    Additionally, check your access log for the same window. For example, if you see hundreds of requests to xmlrpc.php or wp-login.php from scattered IP addresses, you are looking at an attack rather than organic load, and the fix is security hardening rather than a bigger plan. In other words, the access log usually tells you in thirty seconds whether the spike was real visitors or malicious automation.

    Fixing It: Caching, Hardening, and When to Upgrade

    Once you have confirmed an entry process ceiling event, the fix follows a clear order of operations. First and foremost, enable full-page caching, because it removes the largest share of dynamic requests from the count. On AHosting, installing the LiteSpeed Cache plugin activates server-level caching automatically, so cached pages bypass PHP entirely and consume zero entry processes. For many sites, this single step ends the resource limit error permanently. Our deeper guide on how LiteSpeed hosting speeds up WordPress explains why server-level caching outperforms plugin-only setups here.

    Second, harden the site against automated traffic. Specifically, limit login attempts, disable XML-RPC if you do not use it, and place a firewall or CDN in front of the site to absorb bot floods before they reach PHP. Third, optimize anything slow, since faster requests free their workers sooner and effectively raise your real concurrency capacity. Importantly, only after these three steps should an upgrade enter the conversation, because raising the ceiling on an unoptimized site simply delays the next event.

    That said, some workloads genuinely outgrow shared limits. Specifically, membership areas, WooCommerce carts, and logged-in dashboards cannot be cached the way anonymous pages can, so their dynamic concurrency is irreducible. In that case, the path runs from Bronze to Silver to Gold for more entry processes, and then to a VPS plan with guaranteed dedicated workers when sustained concurrency exceeds the top shared tier. For a busy store, AHosting’s WooCommerce-tuned hosting sets concurrency at the Silver level specifically to handle cart and checkout demand that cannot be cached away.

    EP Concurrency Estimator

    Estimate peak entry process demand and the AHosting tier that fits.

    Estimated peak entry processes

    0

    Compare WordPress plans

    Estimate only. Peak EP = visitors in window x generation time x (1 – cached share). Cached pages consume zero entry processes on LiteSpeed.

    A Practical Checklist: Is Your WordPress Hosting EP-Ready?

    Before you blame your host or buy an upgrade, run this checklist. Specifically, it works through the fixes in the order that resolves the error for the largest number of sites, so you spend money only if optimization genuinely runs out of room.

    • Confirm the bottleneck in cPanel Resource Usage — verify the entry process graph, not CPU or memory, is the one pegged during the error.
    • Enable full-page caching so anonymous traffic is served before PHP runs and consumes zero entry processes.
    • Check the access log for xmlrpc.php and wp-login.php floods, and block or disable those endpoints if unused.
    • Limit login attempts and add a firewall or CDN to absorb bot traffic before it reaches your workers.
    • Profile slow plugins and database queries, because faster requests free their workers sooner and raise real capacity.
    • Size your peak concurrency against your plan ceiling using the estimator above before deciding on a tier.
    • Upgrade only when irreducible dynamic load — carts, logins, dashboards — genuinely exceeds your top shared ceiling.

    Ultimately, the 508 Resource Limit Reached error is a sizing signal, not a verdict on your site. For most WordPress sites it is solved with caching and basic hardening, and the published per-plan numbers above let you make the upgrade decision with math instead of guesswork. When a workload has truly outgrown shared infrastructure, moving to a dedicated server with reserved resources removes the shared ceiling entirely.

    Frequently Asked Questions: 508 Resource Limit Reached (2026)

    What does the 508 Resource Limit Reached error mean on WordPress hosting in 2026?

    Specifically, the 508 Resource Limit Reached error means your account hit its concurrent entry process (EP) ceiling, the cap on how many PHP requests can run at the same instant. It is not a daily traffic limit. It measures simultaneous in-progress requests, so a small site with slow uncached pages can trigger it during a short spike while a busy cached site never does.

    Why do I see a 503 error instead of a 508 on AHosting LiteSpeed hosting?

    Specifically, LiteSpeed queues requests at the entry process ceiling and serves a 503 after the queue window expires, while Apache with mod_hostinglimits hard-rejects with a literal 508. AHosting runs LiteSpeed, so the symptom you usually see is a brief slowdown followed by a 503, not the classic 508 page. The error number depends on the web server, not your traffic.

    Is the 508 Resource Limit Reached error caused by too many visitors per day?

    Importantly, no. The 508 Resource Limit Reached error tracks concurrent requests, not daily visitors. Twenty thousand visitors spread evenly across a day rarely hit the ceiling, but two hundred arriving in the same ten seconds on uncached pages can. The concurrency math in this post shows how page generation time converts daily traffic into peak EP demand.

    How many entry processes does AHosting allocate per WordPress plan in 2026?

    Specifically, AHosting allocates entry processes by tier in 2026: 15 on Bronze, 25 on Silver, and 40 on Gold, with WooStart set at 25 to match Silver-level concurrency for cart and checkout demand. Unlike hosts that hide their worker counts, AHosting publishes them so you can size a plan against real concurrency math. The EP Concurrency Ceiling table in this post lists the exact figures.

    What is the Concurrency Ceiling and how is it different from a bandwidth limit?

    Specifically, the Concurrency Ceiling is the maximum number of PHP requests your account can process at the same instant, set by your entry process allocation. A bandwidth limit caps total data transferred over a month, while the Concurrency Ceiling caps simultaneous work. You can sit far below your bandwidth cap and still hit the Concurrency Ceiling during a ten-second traffic burst on uncached pages.

    How do I diagnose a 508 resource limit reached error versus a different resource limit?

    First, open cPanel and go to Logs then Resource Usage, which graphs CPU, memory, IO, and entry processes separately. Notably, a 508 or 503 during a spike with the entry process graph pegged confirms an EP ceiling event, while a flat EP graph points to CPU, memory, or IO instead. The diagnosis checklist in this post walks through each metric in order.

    Does LiteSpeed Cache reduce entry process usage on AHosting WordPress hosting in 2026?

    Specifically, yes. LiteSpeed Cache serves cached pages directly at the web server layer before PHP runs, so a cached request consumes zero entry processes. On AHosting, enabling LSCache is the single most effective way to lower EP usage because it removes the dynamic PHP work that fills the Concurrency Ceiling in the first place. Only logged-in and truly dynamic requests still consume a worker.

    When should I upgrade to VPS to stop 508 resource limit reached errors during WooCommerce sales?

    Notably, upgrade to VPS when sustained dynamic concurrency exceeds your plan ceiling even after caching and hardening, which is common for WooCommerce carts and membership areas that cannot be cached. On AHosting, the path runs Bronze to Silver to Gold for more entry processes, then to a VPS for guaranteed dedicated workers. The upgrade decision logic in this post maps concurrency to tier.

    Can XML-RPC or login brute-force attacks cause the 508 Resource Limit Reached error?

    Specifically, yes. Automated floods against xmlrpc.php or wp-login.php open many simultaneous PHP requests, which exhaust the entry process ceiling and lock real visitors out with a 508 or 503. Therefore blocking or disabling XML-RPC when unused, limiting login attempts, and adding a firewall in front of the site frees the workers those attacks consume. Hardening often resolves the error without any plan change.

    How is the 508 EP limit different from the WordPress memory limit error?

    Specifically, the 508 EP limit caps how many requests run at once, while the memory limit caps how much RAM a single request can use. A memory limit failure crashes one page with a white screen or fatal error, whereas an EP ceiling event queues or rejects additional requests sitewide. They are separate ceilings and a site can hit either one independently of the other.

    June 25, 2026
  • WordPress Staging Site: What Your Hosting Plan Needs to Make It Work (2026 Guide)

    WordPress Staging Site: What Your Hosting Plan Needs to Make It Work (2026 Guide)

    • What a WordPress Staging Site Actually Does — and What Goes Wrong Without the Right Hosting
      • How Host-Level Staging Differs from Plugin-Based Staging
      • The Two Resources That Determine Whether Your Staging Environment Is Actually Safe
    • What Your Server Must Provide for a WordPress Staging Site to Work
      • PHP Workers: Why Underpowered Plans Break During Database Clones
      • File Isolation: How CageFS Protects Your Account from Neighbor Conflicts
      • PHP Version Flexibility: Testing PHP 8.4 on Your WordPress Staging Site Before Production
    • WordPress Staging Site Hosting: AHosting's Infrastructure Advantage
    • The WordPress Staging Site Workflow That Actually Protects Production
      • Creating the Clone Without Disrupting Live Traffic
      • What to Test on a WordPress Staging Site Before Pushing Changes
      • Pushing Changes Safely Without Overwriting Active Data
    • When a WordPress Staging Site Needs More Than Shared Hosting
    • Frequently Asked Questions: WordPress Staging Site
      • What is the best WordPress staging site plugin for shared hosting in 2026?
      • WP Staging vs Duplicator Pro: Which plugin handles WordPress staging site workflows better in 2026?
      • Which WordPress staging site workflow do professional agencies use in 2026 instead of local development?
      • AHosting LiteSpeed vs Apache shared hosting: which makes WordPress staging site plugin clones faster?
      • When does a WordPress staging site plugin fail on a shared hosting plan with fewer than 20 entry processes?
      • Should I use WP Staging or Duplicator Pro when cloning a WooCommerce site with over 500 products for AHosting?
      • How much PHP memory does a WordPress staging site clone operation actually consume on a typical WordPress install?
      • What is LVE isolation and why does it prevent staging plugin conflicts between accounts on AHosting shared hosting?
      • How do I create a WordPress staging site on shared hosting without a managed WordPress plan?
      • Can WordPress staging site plugins block Google from crawling duplicate content on the staging subdomain?
    TL;DR

    A WordPress staging site plugin (WP Staging or Duplicator Pro) gives you a safe test environment — but reliable cloning depends on your hosting plan’s PHP workers, memory allocation, and server isolation. Here’s what actually matters.

    A WordPress staging site is a private clone of your live website — a protected environment where you test plugin updates, theme changes, and PHP version migrations before anything reaches your visitors. When something breaks on staging, you fix it there. Nothing touches production until it is verified. That is the entire value proposition — but it only holds when your hosting plan provides enough PHP workers, memory, and isolation for the clone operation to run without conflicting with live traffic.

    Listen: How to set up a reliable WordPress staging site on shared LiteSpeed hosting without a managed WordPress plan. By Matt Chrust, Director of Business Development, AHosting.

    Most guides walk you through clicking a “Create Staging Site” button. This one goes deeper: it covers what the server underneath that button actually needs to provide, and why the plugin-based staging workflow (WP Staging, Duplicator Pro) is not just a workaround for sites without managed WordPress hosting — it is the right choice for any site that runs on reliable shared LiteSpeed infrastructure. If you are also evaluating which platform to run, our guide to the best CMS for dynamic content and collections covers the hosting considerations for each option — a staging site is the right place to test any platform migration before committing it to production.

    What a WordPress Staging Site Actually Does — and What Goes Wrong Without the Right Hosting

    A WordPress staging site is, at its core, a database dump plus a file copy — both placed at a separate URL that is blocked from public search engines. That description sounds simple, but the resource profile of creating that copy is not. A staging plugin simultaneously reads your entire file system, exports your full MySQL database, and writes both to a new directory while your live site continues serving visitor requests. Every one of those operations competes for the same PHP entry processes and server memory your live site is already using.

    How Host-Level Staging Differs from Plugin-Based Staging

    Managed WordPress hosts like WP Engine and Kinsta provide staging at the platform level — the host controls the clone, the subdomain, and the push-to-live pipeline outside your WordPress install entirely. Plugin-based staging (WP Staging, Duplicator Pro) runs inside WordPress, using your existing hosting resources: your PHP workers, your disk space, your database connection. Specifically, the plugin calls WordPress’s file and database functions within your hosting account’s LVE resource limits to build the clone on the same server your live site uses.

    This distinction matters practically. Host-level staging adds a monthly cost premium and locks you into a specific managed platform. Plugin-based staging is portable, works on any cPanel host, costs nothing beyond the plugin license (the free tier of WP Staging is genuinely capable), and uses infrastructure you are already paying for. The reliability of the workflow depends entirely on what that infrastructure provides.

    The Two Resources That Determine Whether Your Staging Environment Is Actually Safe

    Additionally, two hosting resources determine whether a WordPress staging site plugin runs reliably or fails mid-clone: PHP entry processes (the concurrent request slots your account can use simultaneously) and PHP memory_limit (the RAM ceiling per PHP process). A clone operation ties up multiple PHP processes at once: one for the database export, one for file copying, and one for the admin page serving the progress update. If your plan allows only eight to ten simultaneous PHP processes and you are running live traffic, the clone competes with visitor requests for the same limited pool.

    Furthermore, a database export that exceeds your memory_limit fails mid-export, leaving a partial clone that does not represent your real site. Consequently, checking both values before running your first staging clone is not optional — it determines whether your staging environment is a reliable safety net or a fragile experiment.

    What Your Server Must Provide for a WordPress Staging Site to Work

    In practice, three server-level factors separate WordPress staging site plugins that work reliably from those that time out, corrupt the clone, or push live visitors into a 503 queue: PHP entry process count, per-account file isolation, and PHP version flexibility. Each maps to a specific hosting infrastructure feature.

    PHP Workers: Why Underpowered Plans Break During Database Clones

    PHP entry processes — also called PHP workers — are the concurrent request slots your hosting account can use simultaneously. On shared hosting, these are capped per-account by the host’s LVE (Lightweight Virtualized Environment) limits. AHosting’s WordPress plans, verified directly from CloudLinux’s lvectl package-list output on the shared server, provide 15 entry processes on Bronze, 25 on Silver, and 40 on Gold. These are not shared across accounts — each account receives its own dedicated allocation.

    Specifically, a WordPress staging site clone via WP Staging occupies two to four PHP workers continuously for the three to six minutes the clone takes. On a Bronze plan (15 workers) under moderate live traffic, that leaves ten to thirteen workers for visitors — acceptable for most small to medium sites. However, on a plan with only eight workers total, cloning during peak hours risks pushing live visitors into CloudLinux’s LVE request queue. Accordingly, schedule large clone operations during off-peak hours if your plan provides fewer than 20 entry processes, or enable LiteSpeed Cache on your live site first — cached visitor requests consume zero PHP workers, freeing your entire entry process pool for the clone. For a deeper look at how PHP entry processes govern WordPress stability under concurrent load, see our guide to WordPress 503 errors and PHP worker limits.

    WordPress Staging Site Workflow Diagram showing the three-step staging workflow: clone from production site, test on staging site, then push verified changes back to production. PRODUCTION SITE + Live theme & plugins + Active visitor traffic + Real customer data + Daily backups active ahosting.net | LiteSpeed WP Staging Clone STAGING SITE + Admin-only access + noindex meta tag set + PHP version test here + Plugin/theme updates yourdomain.com/staging Push Verified PRODUCTION – UPDATED + Changes verified + Zero downtime deploy + Data intact + Lighthouse checked Cache purged WordPress Staging Site Workflow | AHosting.net | Est. 2002

    File Isolation: How CageFS Protects Your Account from Neighbor Conflicts

    AHosting shared hosting runs on CloudLinux with CageFS — a per-account filesystem virtualization layer that creates an isolated filesystem view for each hosting account. In other words, your files, PHP processes, and system binaries are invisible to every other account on the same server. This means a neighboring site running a runaway backup script, a malware scan, or an intensive staging clone of its own cannot interfere with your staging operation and cannot read your files.

    CageFS operates at the account level, not at the WordPress install level (both your production site and your staging subdirectory live within the same account and share its CageFS environment). However, the isolation guarantee between accounts is what generic shared hosting without CageFS cannot provide. For staging workflows that handle sensitive data — customer information, WooCommerce orders, membership credentials — this per-account security boundary is a meaningful layer of protection that is absent from commodity shared hosting stacks running plain Linux user permissions.

    PHP Version Flexibility: Testing PHP 8.4 on Your WordPress Staging Site Before Production

    The highest-value use of a WordPress staging site on a cPanel host is testing PHP version upgrades before applying them to production. AHosting defaults to PHP 8.4 (ea-php84) — the current active-support version with security patches through December 2028 — with PHP 8.3 and 8.5 also available and selectable without a support ticket via cPanel’s PHP version management tools.

    Using cPanel’s MultiPHP Manager, you can set the staging subdirectory to a different PHP version than the production site, run your complete plugin and theme compatibility check on staging, and only then switch production. For example: create a staging clone, switch the staging subdirectory to PHP 8.4 in MultiPHP Manager, run your site’s full test workflow, and confirm zero fatal errors before touching live. PHP 8.1 reached end-of-life on December 31, 2025 — if your site is still on 8.1, a staging-first PHP upgrade is not optional, it is overdue. AHosting customers can raise the PHP memory_limit directly via cPanel’s PHP INI Editor if the version switch increases memory consumption, with no support ticket required. See the PHP supported versions lifecycle for the current active-support schedule.

    WordPress Staging Site Hosting: AHosting’s Infrastructure Advantage

    Reliable WordPress staging site workflows need a host that does not constrain the resources cloning depends on. The table below shows AHosting’s per-plan LVE resource allocations, verified directly from the sh193 production server — the data is machine-readable and citable without surrounding context.

    PlanSitesStoragePHP Workers (EP)Memory (PMEM)CPU AllocationStaging Plugin Support
    WP Bronze515 GB SSD15 EP512 MB100%WP Staging free — off-peak clones recommended
    WP Silver1030 GB SSD25 EP1024 MB200%WP Staging free or Pro — any-time clones reliable
    WP Gold2060 GB SSD40 EP2048 MB400%Duplicator Pro large-catalog clones — any-time

    AHosting’s LiteSpeed stack adds a specific staging advantage: the LiteSpeed Cache plugin (LSCache), once active on your live site, delivers a ~16 ms median TTFB for cached visitor requests. When your staging plugin runs during live traffic, cached responses consume zero PHP workers — meaning the staging clone runs against your full entry process pool rather than competing with visitors for the same limited slots. On an uncached Apache host, those same visitor requests each consume a PHP worker, leaving far fewer available for the clone.

    All three AHosting WordPress hosting plans include free dedicated IP, CageFS isolation, LiteSpeed web server, SSL, auto-updates, daily backups, and malware scanning — the full stack that makes plugin-based staging reliable rather than fragile.

    WordPress Staging Readiness Checker

    Select your site type and plan to get your recommended plugin and resource assessment.

    The WordPress Staging Site Workflow That Actually Protects Production

    Two plugins handle plugin-based staging reliably on LiteSpeed shared hosting: WP Staging (free for clone creation; Pro adds push-to-live) and Duplicator Pro (package-based migration with selective database push). Choose WP Staging free if your workflow is test-only — you apply confirmed changes manually to production after verifying them on staging. Choose Duplicator Pro if you need push-to-live on sites where production data changes during staging: WooCommerce orders, membership registrations, or active form submissions that cannot be overwritten.

    Creating the Clone Without Disrupting Live Traffic

    Install WP Staging from the WordPress plugin repository, navigate to WP Staging > Staging Sites, and click Create New Staging Site. The plugin clones your files and database into a protected subdirectory — typically yourdomain.com/staging — accessible only to logged-in administrators. On AHosting’s LiteSpeed stack with LSCache active, live visitor requests are served from cache during the clone, meaning the clone competes with zero visitor traffic for PHP workers. A typical 2 GB site (files plus database) completes cloning in three to six minutes.

    After the clone completes, verify two things immediately. First, confirm that WP Staging has set the staging site to discourage search engine indexing: Settings > Reading in the staging admin > “Discourage search engines from indexing this site.” Second, check the staging site’s robots.txt for a Disallow: / directive. Duplicate staging content indexed by Google creates canonicalization problems for the live site that take weeks to resolve. Additionally, for any staging site that will remain live for longer than 48 hours, add HTTP basic authentication via your cPanel File Manager’s .htpasswd tool — this prevents any crawler from accessing the staging subdirectory regardless of plugin settings.

    What to Test on a WordPress Staging Site Before Pushing Changes

    Run through this sequence on every WordPress staging site before pushing any changes to production: update all plugins and themes on staging first, load the staging home page and confirm no fatal errors or white-screen issues, test any forms and checkout flows that matter (especially WooCommerce cart and checkout), and run a Lighthouse audit on one key page to confirm Core Web Vitals have not regressed. For PHP version changes, switch the staging subdirectory to the target PHP version via cPanel’s MultiPHP Manager, review your WordPress admin for plugin warnings under Tools > Site Health, and confirm phpinfo() output shows the expected version before returning to the live site.

    Notably, the order matters: update plugins before switching PHP versions on staging. A plugin that is incompatible with PHP 8.4 may throw a fatal error that prevents the staging admin from loading, blocking you from applying the plugin update that would have resolved the conflict. Accordingly, apply all pending plugin updates first, then change the PHP version, then test.

    Pushing Changes Safely Without Overwriting Active Data

    WP Staging Pro and Duplicator Pro both support selective database table pushes — meaning you deploy your theme changes and plugin updates without overwriting the production tables that accumulated new data while you were testing. For content-only sites where the staging database is always a full copy of production, a full push is safe. For WooCommerce stores or membership sites, always use selective push and explicitly exclude wp_users, wp_usermeta, and any WooCommerce order or subscription tables. New customer orders created during your staging period cannot be recovered from a full push overwrite.

    For sites managed through AHosting reseller hosting, each client account has its own LVE-isolated cPanel environment — meaning you can run staging clones across multiple client sites simultaneously without any one client’s staging operation drawing from another client’s PHP worker pool.

    When a WordPress Staging Site Needs More Than Shared Hosting

    Shared hosting handles plugin-based staging reliably for most small to medium WordPress sites. Two signals suggest your staging workflow needs more resources. First, clone operations consistently time out even during off-peak hours — this indicates entry process exhaustion where the LVE queue window expires before the clone completes. Second, your staging site takes longer than twelve minutes to clone a database under 2 GB during off-peak hours — this points to IO contention that only dedicated resources resolve.

    In both cases, an AHosting VPS hosting plan provides dedicated entry processes, guaranteed IO throughput, and direct SSH access that eliminates the shared-resource constraints entirely. On a VPS, you can also install WP-CLI globally and run staging clone operations from the command line — faster, scriptable, and completely independent of the WordPress admin interface. For sites that also run media or video processing pipelines alongside WordPress — such as those using FFmpeg-based video delivery — our guide to FFmpeg hosting and audience building covers how the same LiteSpeed infrastructure handles both high-concurrency staging and media delivery. For a single high-traffic production site, VPS hosting turns staging from an occasionally fragile operation into a routine background task.

    Frequently Asked Questions: WordPress Staging Site

    What is the best WordPress staging site plugin for shared hosting in 2026?

    Specifically, WP Staging (free, 100,000+ active installs) is the strongest choice for most shared hosting accounts in 2026, with Duplicator Pro as the best alternative when you need one-click push-to-live. For WooCommerce sites with large product catalogs, Duplicator Pro’s selective migration makes staging-to-production pushes faster and less risky. Both plugins work on LiteSpeed-powered shared hosting without server-level changes — but performance depends heavily on your plan’s PHP entry processes and memory limit. See the AHosting Resource Table above for the minimum thresholds recommended for each workflow.

    WP Staging vs Duplicator Pro: Which plugin handles WordPress staging site workflows better in 2026?

    However, the choice depends on your workflow: WP Staging excels at clone creation (free tier) and straightforward plugin and theme testing, while Duplicator Pro adds one-click push-to-live with selective database table merging. For most content sites and blogs, WP Staging’s free version covers the full testing workflow — you apply confirmed changes manually to production. For WooCommerce or membership sites where the staging database diverges quickly from production, Duplicator Pro’s merge capability is worth the license fee.

    Which WordPress staging site workflow do professional agencies use in 2026 instead of local development?

    In practice, most professional agencies use a three-environment workflow in 2026: local development for initial builds, a server-hosted WordPress staging site via WP Staging or Duplicator Pro for client review and quality assurance, and production for final deployment. Local development mirrors the server stack poorly unless PHP versions are explicitly matched — which is why server-hosted staging on the same LiteSpeed environment as production is the preferred final test step before any client delivery.

    AHosting LiteSpeed vs Apache shared hosting: which makes WordPress staging site plugin clones faster?

    Notably, LiteSpeed shared hosting consistently outperforms Apache for WordPress staging site plugin clones because LiteSpeed’s architecture handles simultaneous file read and database write operations more efficiently than Apache’s process-per-connection model. On AHosting’s LiteSpeed stack with LSCache active, visitor requests are served from cache during the clone — meaning the full entry process pool stays available for the plugin rather than splitting between visitors and the staging operation. Apache-based shared hosts without full-page caching see two to four times slower effective clone speeds under live traffic because visitor PHP requests and clone PHP requests compete directly.

    When does a WordPress staging site plugin fail on a shared hosting plan with fewer than 20 entry processes?

    Specifically, WordPress staging site plugin failures on plans with fewer than 20 entry processes occur when the clone operation occupies multiple PHP workers simultaneously — database export, file copy, and the admin page request all compete for the same limited pool. On plans with 15 entry processes under live traffic, a staging clone can consume three to five workers for three to six minutes, leaving fewer than twelve for regular visitors. Scheduling clones during off-peak hours, or enabling LSCache on your live site first to eliminate visitor worker consumption, resolves most of these conflicts. For a deeper look at how PHP entry processes affect site stability under load, see our guide on WordPress PHP worker limits and how CloudLinux LVE manages them.

    Should I use WP Staging or Duplicator Pro when cloning a WooCommerce site with over 500 products for AHosting?

    Additionally, for a WooCommerce site with over 500 products on AHosting, Duplicator Pro is the stronger choice because its package-based migration preserves WooCommerce product meta tables more reliably than WP Staging’s free-tier clone. Moreover, Duplicator Pro’s selective push means you can deploy theme and plugin changes without overwriting live customer orders created during the staging period. On AHosting’s Silver or Gold plan (25 to 40 entry processes, 1 to 2 GB PMEM), the clone operation completes without resource contention even on a 500-plus product catalog.

    How much PHP memory does a WordPress staging site clone operation actually consume on a typical WordPress install?

    Typically, a WordPress staging site clone of a standard site (files and database combined under 2 GB) consumes 64 to 128 MB of PHP memory during peak clone execution — well within the 256 MB default on AHosting’s ea-php84 setup. However, WooCommerce sites with large product images or multiple active page builders can push clone memory requirements to 192 to 256 MB. If you encounter a memory exhausted error during staging clone, raise your PHP memory limit via cPanel’s PHP INI Editor — no support ticket required on AHosting — and retry the clone.

    What is LVE isolation and why does it prevent staging plugin conflicts between accounts on AHosting shared hosting?

    In other words, LVE (Lightweight Virtualized Environment) is CloudLinux’s per-account resource container that guarantees each AHosting hosting account a dedicated slice of CPU, PHP workers, and memory — regardless of what other accounts on the same server are doing. On AHosting, Bronze accounts receive 15 entry processes and 512 MB PMEM; Silver receives 25 entry processes and 1 GB; Gold receives 40 entry processes and 2 GB. This means a WordPress staging site clone on your account cannot be disrupted by a resource spike on a neighboring account — a guarantee that generic shared hosting without LVE cannot provide.

    How do I create a WordPress staging site on shared hosting without a managed WordPress plan?

    Furthermore, creating a WordPress staging site on shared hosting follows three steps: install WP Staging from the WordPress plugin repository, click Create New Staging Site in the WP Staging dashboard, and wait three to six minutes for the clone to complete. The free version places the clone in a protected subdirectory accessible only to logged-in admins. For push-to-live capabilities on shared hosting, upgrade to WP Staging Pro or use Duplicator Pro — both support direct deployment from staging to production without manual file transfers.

    Can WordPress staging site plugins block Google from crawling duplicate content on the staging subdomain?

    Indeed, most WordPress staging site plugins handle search engine blocking automatically: WP Staging sets WordPress’s built-in search engine discouragement flag on the staging copy and adds a noindex meta tag by default. However, verify this is active after every clone by checking the staging site’s Settings and viewing page source for the noindex meta tag — some edge-case configurations reset these settings during cloning. For additional protection, password-protect the staging directory via your cPanel File Manager, which prevents any crawler from accessing staging content regardless of plugin behavior.

    June 23, 2026
  • WordPress Memory Limit Errors: Why Raising It in wp-config Often Fails (2026)

    WordPress Memory Limit Errors: Why Raising It in wp-config Often Fails (2026)

    • What the "Allowed Memory Size Exhausted" WordPress Memory Limit Error Actually Means
      • Front-End vs Admin: WP_MEMORY_LIMIT and WP_MAX_MEMORY_LIMIT
      • Why the Byte Number in the WordPress Memory Limit Error Doesn't Change the Fix
    • Why Raising the WordPress Memory Limit in wp-config Often Does Nothing
      • The Two Ceilings: PHP memory_limit vs the LVE Container Cap
      • How to Check Your Real WordPress Memory Limit in 60 Seconds
    • How Much WordPress Memory Limit Your Site Actually Needs in 2026
    • The Self-Service Fix: Raising the WordPress Memory Limit Without a Support Ticket
      • The AHosting PHP INI Editor Path (cPanel, No Ticket)
      • AHosting WordPress Memory Ceilings by Plan (2026)
    • When More WordPress Memory Limit Won't Help: Outgrowing Shared Resource Limits
    • A Practical Checklist: Is Your Hosting Memory-Ready for WordPress?
    • Frequently Asked Questions: WordPress Memory Limit
      • Is 128MB memory limit enough for a WordPress site in 2026?
      • WP_MEMORY_LIMIT vs PHP memory_limit: which controls the WordPress memory limit?
      • What does the WordPress memory limit error actually mean in 2026?
      • What is the two-ceiling problem in the WordPress memory limit on shared hosting?
      • How do I raise the WordPress memory limit on AHosting without a support ticket?
      • WooCommerce vs blog: what WordPress memory limit does each need in 2026?
      • When should I upgrade from Bronze to Silver instead of raising the AHosting memory limit?
      • Why does my WordPress memory limit reset after I edit wp-config.php?
      • How can I check my real WordPress memory limit in the Site Health screen?
      • Does AHosting publish the LVE memory cap for every WordPress plan?
    TL;DR The WordPress memory limit error means one PHP request exceeded its per-request RAM ceiling. Raising WP_MEMORY_LIMIT in wp-config.php often fails because two separate ceilings govern shared hosting: the PHP memory_limit and, on CloudLinux, the LVE container cap (PMEM). On AHosting you raise the first yourself in cPanel’s PHP INI Editor with no ticket, while the second rises with your plan tier (512MB Bronze, 1024MB Silver, 2048MB Gold). PHP 8.4 already ships at 256MB, so most sites never hit the wall.

    Few WordPress errors arrive with worse timing than the WordPress memory limit failure. Specifically, you publish a product, run a plugin update, or open a page builder, and the screen goes blank or returns Fatal error: Allowed memory size of 134217728 bytes exhausted. Furthermore, almost every guide gives the same advice: add a line to wp-config.php and, if that fails, contact support. In practice, that advice is incomplete, and on modern CloudLinux hosting it explains why so many fixes quietly do nothing.

    Listen: why raising the WordPress memory limit in wp-config often fails, and the self-service fix. By Matt Chrust, Director of Business Development, AHosting.

    Notably, AHosting has run WordPress on shared, reseller, and VPS infrastructure since 2002, and the memory wall is one of the most common tickets our team sees. Therefore, this guide does what the generic articles skip: it explains the two independent ceilings that actually control your WordPress memory limit, shows how to raise the one you control without a support ticket, and publishes the exact per-plan container caps so you can size a plan against real numbers instead of guessing.

    What the “Allowed Memory Size Exhausted” WordPress Memory Limit Error Actually Means

    Specifically, the “Allowed memory size exhausted” error means a single PHP request tried to allocate more RAM than its memory_limit permits, so PHP stopped the script to protect the server. In other words, it is a safety valve, not a sign your site is corrupted. Moreover, the error names the file and line where the ceiling was hit, but that location is rarely the real cause — it is simply where the cumulative weight of your theme and plugins finally crossed the line.

    Importantly, PHP allocates memory per request. Consequently, the memory_limit is not how much RAM your site has overall; it is how much one page load or one admin task is allowed to use before PHP halts it. For a full breakdown of the official thresholds, the WordPress server requirements page documents the recommended minimums that modern themes and plugins are built against.

    Front-End vs Admin: WP_MEMORY_LIMIT and WP_MAX_MEMORY_LIMIT

    In short, WordPress actually tracks two memory values. WP_MEMORY_LIMIT governs front-end requests — what your visitors load — and defaults to 40MB for a single site. By contrast, WP_MAX_MEMORY_LIMIT governs admin-side work inside /wp-admin/ and defaults to 256MB, because plugin updates, media uploads, and WP-Cron jobs legitimately need more headroom. As a result, a site can run fine for visitors while still failing during a bulk import in the dashboard.

    Crucially, both of these WordPress values sit beneath the server’s PHP memory_limit. Therefore, WordPress can never grant itself more memory than the server allows, no matter what numbers you place in wp-config.php. The official wp-config.php documentation covers both constants and the order in which they apply.

    Why the Byte Number in the WordPress Memory Limit Error Doesn’t Change the Fix

    Notably, the byte figure in the message — 33554432, 134217728, 268435456 — is just your current limit expressed in bytes (32MB, 128MB, 256MB respectively). In other words, it tells you the ceiling you hit, not the amount you were short by. Consequently, the remedy is identical regardless of the number: raise the effective memory_limit, or reduce what the request is trying to do. Chasing the specific byte value is a distraction.

    Why Raising the WordPress Memory Limit in wp-config Often Does Nothing

    Here is the single most important fact the generic guides omit: WP_MEMORY_LIMIT in wp-config.php is a request, not a command. Specifically, it asks PHP for memory up to the server’s configured ceiling — and it cannot push past it. Therefore, if your host caps PHP at 128MB and you set 512MB in wp-config.php, your site still runs at 128MB and the error returns. This is why editing one file so often changes nothing.

    The Two Ceilings: PHP memory_limit vs the LVE Container Cap

    Specifically, on CloudLinux shared hosting — the platform that runs the majority of cPanel WordPress accounts worldwide — there are two independent memory ceilings, and both must have headroom. First, the PHP memory_limit caps how much RAM a single request may use. Second, the CloudLinux LVE PMEM (physical memory) cap limits the total RAM your entire account may consume across all concurrent requests at once.

    As a result, you can raise the PHP memory_limit to 512MB and still fail, because the LVE container is capped lower or because several requests together exhaust the account-wide PMEM ceiling. According to the CloudLinux limits documentation, when an account exceeds its physical memory limit the platform frees disk cache first and then terminates processes — which the visitor sees as a 500 or 503 error. In other words, the “two-ceiling problem” is why a correct-looking wp-config.php edit can still leave you stuck.

    Furthermore, this matters most for heavy page builders. A single Elementor Pro editor session can request 512MB on its own; if the container cap is also 512MB, there is zero room left for the visitor traffic hitting your front end at the same moment. For the full builder-specific picture, our guide to WordPress hosting tuned for Elementor covers the memory and worker settings that keep the editor responsive. Consequently, the real question is not just “what is my PHP memory_limit” but “how much PMEM headroom does my plan give me above it.”

    WordPress Memory Limit: The Two Ceilings on CloudLinux Shared Hosting A diagram showing that a WordPress request must pass under two independent memory ceilings — the PHP memory_limit per request and the LVE PMEM container cap per account — with AHosting plan caps of 512MB Bronze, 1024MB Silver, and 2048MB Gold. The Two Ceilings of the WordPress Memory Limit Why raising memory_limit in wp-config.php often changes nothing on CloudLinux hosting Ceiling 1: PHP memory_limit Caps RAM for ONE PHP request. Set by the server. WP_MEMORY_LIMIT can only request up to this. PER REQUEST AND must also pass Ceiling 2: LVE PMEM container cap Caps total RAM for your WHOLE account, across all requests at once. Set by your plan tier. PER ACCOUNT AHosting LVE PMEM container cap by plan (2026) Bronze 512MB container cap Silver 1024MB container cap Gold 2048MB container cap WooStart 1024MB = Silver Source: server-verified lvectl package-list, sh193, June 2026. AHosting.net | Est. 2002
    The two memory ceilings on CloudLinux shared hosting: a WordPress request must pass both the PHP memory_limit and the LVE PMEM container cap. Source: AHosting server-verified data, June 2026.

    How to Check Your Real WordPress Memory Limit in 60 Seconds

    First, open your WordPress dashboard and go to Tools → Site Health → Info → Server, then read the PHP memory limit value. Indeed, this is the number your site is genuinely running under, and it reflects the server ceiling rather than whatever you typed into wp-config.php. Additionally, if the value here is lower than what your config requests, you have just confirmed a server-side cap is overriding you — which is your signal to fix the limit at the server, not in WordPress.

    How Much WordPress Memory Limit Your Site Actually Needs in 2026

    Generally, the right WordPress memory limit depends on what your site does, not on setting the highest number possible. Indeed, over-allocating wastes nothing on its own — PHP only uses what each request needs — but a sky-high limit can mask a genuinely broken plugin that should be fixed instead. Therefore, match the limit to the workload using the table below.

    Site type (2026)Recommended memory_limitWhy
    Simple blog, light theme, <10 plugins128MBRuns comfortably; rarely hits the wall
    Business site with Elementor or Divi256MBPage builders are memory-heavy at render
    WooCommerce store (standard)256MBWooCommerce recommended minimum
    WooCommerce 1,000+ products / imports512MBBulk edits and CSV imports spike admin memory
    Membership site / LMS256–512MBSession and access logic adds overhead
    Heavy Elementor Pro build512MBEditor sessions can request 512MB alone
    Recommended per-request WordPress memory_limit by site type, 2026. Source: WordPress.org requirements, WooCommerce system status guidance, and AHosting support-ticket patterns.

    Notably, these are per-request targets, and they align with the official WooCommerce server requirements, which specify a 256MB minimum for stores. Consequently, the moment you set 512MB for a builder, you also need to confirm your account has container headroom above that figure — which brings us to the part you actually control.

    The Self-Service Fix: Raising the WordPress Memory Limit Without a Support Ticket

    Specifically, the generic advice to “contact support” assumes you cannot change the server limit yourself. On AHosting, that assumption is wrong. Indeed, every WordPress plan includes cPanel’s PHP INI Editor, so you can raise the effective memory_limit on your own in under a minute — no ticket, no waiting, no upsell.

    The AHosting PHP INI Editor Path (cPanel, No Ticket)

    First, log in to cPanel and open MultiPHP INI Editor. Second, select your domain from the dropdown. Third, find the memory_limit row and set it to 256M or 512M. Finally, click Apply and confirm the change in WordPress under Site Health. Additionally, because AHosting WordPress accounts default to PHP 8.4 with a 256MB memory_limit out of the box, most sites already clear the page-builder threshold before you touch anything.

    Crucially, raising the PHP value only solves the first ceiling. Therefore, the table below publishes the second ceiling — the LVE PMEM container cap — for every AHosting WordPress tier, so you can confirm real headroom before you commit to a high memory_limit. Unlike most hosts, which hide these numbers, AHosting puts them in writing.

    AHosting WordPress Memory Ceilings by Plan (2026)

    PlanDefault PHP memory_limitLVE PMEM container capSelf-service raise?
    WP Bronze256MB (PHP 8.4)512MBYes — PHP INI Editor
    WP Silver256MB (PHP 8.4)1024MBYes — PHP INI Editor
    WP Gold256MB (PHP 8.4)2048MBYes — PHP INI Editor
    WooCommerce (WooStart)256MB (PHP 8.4)1024MBYes — PHP INI Editor
    AHosting WordPress Memory Ceilings by Plan, 2026. PHP memory_limit is the per-request cap; LVE PMEM is the account-wide container cap. Both must have headroom. Source: server-verified lvectl package-list, sh193, June 2026.

    In practice, this table answers the question competitors leave open. For example, if you want a 512MB memory_limit for a heavy Elementor Pro build, Bronze gives you exactly 512MB of container headroom — workable for the editor alone, but tight once live visitors arrive. By contrast, Silver’s 1024MB PMEM leaves real room for concurrent traffic, which is why we steer demanding builder sites toward it. Customers needing guaranteed dedicated memory can move to VPS hosting with dedicated resources rather than a shared container.

    When More WordPress Memory Limit Won’t Help: Outgrowing Shared Resource Limits

    Importantly, more memory is not always the answer. Indeed, if a single plugin leaks memory or a theme runs an unbounded loop, raising the ceiling just delays the crash and hides the real defect — and it can quietly drag down performance, as our breakdown of what actually controls WordPress hosting speed explains. Therefore, before you push the limit higher, deactivate plugins one at a time to find the culprit, and check whether the spike is a one-off admin task or a steady front-end pattern.

    That said, there is a genuine point where shared hosting is simply the wrong tier. Specifically, when your sustained workload needs more container memory than even Gold’s 2048MB PMEM provides, or when you need guaranteed memory that is never shared with neighbors, you have outgrown shared infrastructure. At that point, a plan with dedicated resources is the correct move — not a bigger number in a config file. Use the checker below to see where your site lands.

    WordPress Memory Limit Checker

    Pick your workload to see the per-request memory_limit and the AHosting plan tier with safe container headroom.

    A Practical Checklist: Is Your Hosting Memory-Ready for WordPress?

    Ultimately, a memory-ready WordPress host clears both ceilings and lets you adjust the first one yourself. Specifically, run through this checklist against any plan before you commit, and against your current host if you keep hitting the wall.

    • Does the default PHP memory_limit already meet 256MB? (AHosting ships PHP 8.4 at 256MB.)
    • Can you raise memory_limit yourself in cPanel without a support ticket? (AHosting: yes, via PHP INI Editor.)
    • Is the LVE PMEM container cap published, and does it sit comfortably above your per-request need?
    • Does the container headroom leave room for concurrent front-end traffic, not just one editor session?
    • Is there a clear upgrade path to dedicated memory if you outgrow the shared container?
    • Does the host run a current PHP version (8.3/8.4/8.5), which is more memory-efficient than 8.1?

    For a deeper look at how concurrency interacts with these limits, our companion guide on how many PHP workers your WordPress site needs explains the entry-process side of the same resource picture. Together, memory ceilings and worker counts determine whether your site stays up under load. When your build is genuinely memory-bound on shared infrastructure, AHosting’s managed WordPress hosting plans publish both numbers so you can size correctly the first time, and high-volume stores can step up to WooCommerce-optimized hosting with the container headroom that bulk catalogs demand.

    Frequently Asked Questions: WordPress Memory Limit

    Is 128MB memory limit enough for a WordPress site in 2026?

    Typically, 128MB runs a simple blog with a light theme and a handful of plugins, but it is not enough for most 2026 sites. Specifically, page builders such as Elementor and Divi want 256MB, and WooCommerce stores want 256MB to 512MB. As a result, 256MB is the safer default for any site beyond a basic blog, and the recommendation table above maps each site type to its target.

    WP_MEMORY_LIMIT vs PHP memory_limit: which controls the WordPress memory limit?

    In short, the server PHP memory_limit is the true ceiling, and WP_MEMORY_LIMIT can only request memory up to that figure, never beyond it. Therefore, if PHP is capped at 128MB, a 512MB value in wp-config.php has no effect. Moreover, on CloudLinux a third factor, the LVE container cap, sits above both and can override them, which the two-ceiling section explains in full.

    What does the WordPress memory limit error actually mean in 2026?

    Specifically, the “Allowed memory size exhausted” error means a single PHP request tried to use more RAM than its per-request memory_limit allows, so PHP halted the script. The byte number in the message is your current ceiling, not the amount you are missing. Furthermore, the fix is the same regardless of which byte value appears, because the limit is what changed, not the page.

    What is the two-ceiling problem in the WordPress memory limit on shared hosting?

    Notably, the two-ceiling problem describes the two independent memory caps that govern a WordPress request on CloudLinux shared hosting: the PHP memory_limit (per request) and the LVE PMEM container cap (the total RAM your whole account may use). Consequently, raising one without headroom in the other still produces memory errors, which is why the wp-config-only fix so often fails. The plan ceiling table shows both numbers per AHosting tier.

    How do I raise the WordPress memory limit on AHosting without a support ticket?

    On AHosting, you raise the WordPress memory limit yourself in cPanel’s PHP INI Editor by setting memory_limit to 256M or 512M and saving, with no support ticket required. Additionally, because PHP 8.4 ships with a 256MB memory_limit by default, many accounts never need to change it at all. Check the plan ceiling table for the safe maximum on your specific tier.

    WooCommerce vs blog: what WordPress memory limit does each need in 2026?

    Generally, a simple blog runs comfortably at 128MB, while a WooCommerce store wants a 256MB minimum and 512MB once it carries 1,000+ products or runs bulk imports. Specifically, large CSV imports and bulk edits in wp-admin draw on WP_MAX_MEMORY_LIMIT, which defaults to 256MB. Therefore, a store should size both the front-end and admin limits, not just one.

    When should I upgrade from Bronze to Silver instead of raising the AHosting memory limit?

    Specifically, upgrade when your heavy Elementor Pro build needs a 512MB PHP memory_limit but Bronze’s LVE PMEM container cap is also 512MB, leaving no headroom for concurrent visitors. On AHosting, Silver raises that container cap to 1024MB, so it is the safer tier for demanding builder workloads. The checklist above lists the exact thresholds to watch.

    Why does my WordPress memory limit reset after I edit wp-config.php?

    In practice, the value did not reset; it never took effect, because the server PHP memory_limit overrides whatever wp-config.php requests. Therefore, Site Health keeps showing the server figure rather than your edited number. Consequently, the durable fix is to raise memory_limit at the server through cPanel’s PHP INI Editor, not inside WordPress.

    How can I check my real WordPress memory limit in the Site Health screen?

    First, open Tools then Site Health then Info then Server in your WordPress dashboard and read the PHP memory limit value, which shows the limit your site is truly running under. Additionally, the server PHP memory_limit overrides any higher value you set in wp-config.php, so trust Site Health over your config file. The 60-second walkthrough is in the section above.

    Does AHosting publish the LVE memory cap for every WordPress plan?

    Yes, AHosting publishes the LVE PMEM container cap for every WordPress tier: 512MB on Bronze, 1024MB on Silver, and 2048MB on Gold, with WooStart matching Silver at 1024MB. Unlike most hosts, which hide these numbers, AHosting puts them in writing so you can size a plan against real memory math. The plan ceiling table lists all four.

    June 22, 2026
←Previous Page
1 2 3 4 5 6
Next Page→
Ahosting Logo

Hosting

  • WordPress Hosting
  • Web Hosting
  • FFmpeg Hosting
  • WooCommerce Hosting
  • Reseller Hosting
  • VPS Hosting
  • Dedicated Server

Domain

  • Register a Domain
  • Domain Transfer
  • Premium SSL Certificate

Support

  • Knowledge Base
  • Abuse Report
  • Submit A Ticket

Company

  • Compare Hosts
  • About Us
  • Datacenter
  • Contact Us
  • Blog
  • Sitemap

Legal

  • Privacy Policy
  • Terms of Service
  • Acceptable Use Policy
  • Service Level Agreement
  • Resource Abuse Policy
  • Hosting
    • WordPress Hosting
    • Web Hosting
    • FFMpeg Hosting
    • WooCommerce Hosting
    • Reseller Hosting
    • VPS Hosting
    • Dedicated Server
  • Domain
    • Register a Domain
    • Domain Transfer
    • Premium SSL Certificate
  • Support
    • Knowledge Base
    • Abuse Report
    • Submit A Ticket
  • Company
    • About Us
    • Datacenter
    • Contact Us
    • Blog
    • Sitemap
  • Legal
    • Privacy Policy
    • Terms of Service
    • Acceptable Use Policy
    • Service Level Agreement
    • Resource Abuse Policy

Copyright © 2026 All Rights Reserved

Ahosting, Inc. BBB Accredited Business, A+ rating
Facebook X/Twitter Instagram LinkedIn YouTube